
Basics: Online Responder (Online Certificate Status Protocol, OCSP)
Certificates usually have a "CRL Distribution Points" extension that tells an application where the certificate's associated certificate revocation list (CRL) can be found.
This is like a telephone directory: It contains all the serial numbers of certificates that have been revoked by the certification authority (and are still within their validity period). Every application that checks the revocation status must download and evaluate the entire certificate revocation list.
As the size increases, this procedure becomes increasingly inefficient. As a rule of thumb, 100,000 revoked certificates already correspond to approx. 5 MB file size for the certificate revocation list.
The Online Certificate Status Protocol (OCSP) was developed for this purpose (under the leadership of ValiCert): It is similar to a directory assistance service where applications can request the revocation status for individual certificates, thus eliminating the need to download the entire CRL. OCSP is specified in RFC 6960 .
Sometimes it is necessary for a certificate issued by a certification authority to be withdrawn from circulation even before its expiration date. To make this possible, a certification authority keeps a certificate revocation list. This is a signed file with a relatively short expiration date, which is used in combination with the certificate to check its validity.
How it works
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Instead of downloading a (supposedly large) CRL, a client queries the Online Responder for the revocation status of each certificate to be checked and receives a signed response as to whether the certificate has been revoked or not. If the certificate revocation list is a phone book, OCSP is thus the directory assistance to which targeted specific queries can be sent.
In the Microsoft implementation, OCSP in turn uses CRLs as its data source. This means that there is no direct connection to the certification authority database, and by default the responder cannot determine whether a requested certificate has actually been issued by the certification authority (Deterministic "Good" ).
The availability of OCSP can be specified within the Authority Information Access (AIA) attribute in an issued certificate or configured globally on the checking computer . The OCSP extension is located under AIA, since the Online Responder is also an authority (Validation Authority, VA).
If an OCSP address is present in the certificate to be checked, modern Windows operating systems prefer it over certificate revocation lists. This behavior thus applies to all Windows applications that use the Microsoft CAPI to check certificates.
Disadvantages when using OCSP
However, OCSP brings some disadvantages along with its advantages:
- OCSP is often understood as a security feature due to the supposedly real-time revocation check, but it is merely a tool for improving the performance of the revocation status infrastructure, since there is no guarantee that the client will not ultimately fall back on the certificate revocation list after all. That being said, OCSP responses also have a validity period, just like a certificate revocation list. The end date for this validity period is taken 1:1 from the underlying certificate revocation list.
- If the certificate to be checked also contains a CRL distribution point in addition to the OCSP address and the Online Responder is not available, (Windows) clients fall back on the certificate revocation list. This means that the exclusive use of OCSP cannot be guaranteed.
- OCSP is location dependent, i.e. in a distributed infrastructure all clients would connect to the central Online Responder over potentially slow and failure-prone WAN lines, which can effectively even increase CRL check time as well as network load.
However, it may well be worth considering implementing OCSP even though it is not (yet) needed from the current point of view. Should the need arise in the future to revoke a very large number of certificates in a short period of time, as was the case with the Heartbleed incident, revocation checking via certificate revocation lists would quickly reach the limit of its capabilities.
On the usefulness of using OCSP
OCSP is an additional IT service that ties up human, technical and financial resources. In view of the fact that "live" revocation (desired in many cases) is not feasible, the question arises as to when the use of OCSP makes sense.
Reasons for this may be:
- Auditing, if done correctly (see article "Force domain controller (or other participants) to use an Online Responder (OCSP) " for an application example).
- Performance with a large number of (expected) revoked certificates and correspondingly large certificate revocation lists. In most environments, however, these sizes will never be reached in practice.
- As an emergency option. Should the need arise in the future to revoke a large number of certificates at once, as was the case with the Heartbleed vulnerability, for example. But as already mentioned, most environments tend not to exceed the break-even point at which OCSP is more efficient than a certificate revocation list.
- Application-specific peculiarities can make the use of an Online Responder useful: For example, when creating document signatures, Adobe Reader and Adobe Acrobat use the OCSP response (if any) for the signing certificate at the time of signing as proof that the certificate was valid at that time.
Please also note that Google Chrome and the Chromium-based Microsoft Edge (codenamed Anaheim) do not perform a revocation status check by default anyway.
Pitfalls
It cannot be guaranteed that OCSP will be used due to various influencing factors.
These include:
- Magic Number
- Service availability
- Client implementations or settings that may override the certificate content
Magic Number
The Magic Number is proprietary to the implementation of OCSP in the Windows ecosystem.
Microsoft Windows (the Microsoft CAPI) offers the special feature of a "magic number", i.e. a counter that is incremented for each certification authority. If the counter is exceeded and the certificate also has a CRL distribution point (CDP), this is used for future requests for efficiency reasons. See article "Configure the "Magic Number" for the Online Responder ".
OCSP is skipped if the service is not available
Windows clients fall back to existing CRL distribution points if a configured Online Responder is not available.
Revocation information is not "live": the client-side cache
Both CRLs and OCSP responses are cached by Microsoft CryptoAPI / CAPI for the period of their validity.
This statement applies to applications that use the CryptoAPI / CAPI on Windows, such as Internet Explorer, Edge or Google Chrome. However, the behavior may differ for other applications (e.g. Mozilla Firefox) or operating systems.
On Windows operating systems, there are two types of caches for revocation information:
- Hard disk cache. This cache can be used by all applications and is persistent, i.e. available even after a restart of the computer.
- Working memory cache. This cache is application-specific and only exists during the runtime of the application. If the application is terminated, this cache is also deleted.
See also article "View and clear the CRL address cache (CRL URL Cache) ".
OCSP was not developed as a security feature but as an efficiency and thus performance feature. The OCSP response is valid (in the Microsoft implementation) exactly as long as the underlying certificate revocation list.
Revocation information is not "live": the server-side cache
For reasons of efficiency, the Microsoft Online Responder is preceded by a cache in the IIS web server, which keeps OCSP responses, once signed, during their validity period so that they do not have to be signed again for further requests for the same certificate and generate load on the server and any existing hardware security module (HSM) . This circumstance also contradicts the assumption of a live revocation status check.
Significance of the OCSP responses
Since the Microsoft Online Responder uses certificate revocation lists as its data source, it has no information about whether a requested certificate for which no revocation status could be determined was actually issued by the certification authority and can be found in its database.
However, it is possible to additionally check the serial numbers of the certificates to be checked against a list of certificates issued by the certification authority, in order to detect and possibly raise an alarm on certificates issued by using the private key of the certification authority directly (see article "Signing certificates bypassing the certification authority ").
See article "Configure deterministic "Good" for the Online Responder (OCSP) " for more information.
OCSP response signing certificates cannot be revoked
The OCSP signing certificate must not contain any revocation status information to avoid a loop situation (the revocation status would eventually be checked again by OCSP).
Therefore, OCSP response signing certificates are certificates that require special protection, and they should either be protected with a hardware security module (HSM) or at least have a very short certificate lifetime.
Therefore, in the default setting of the Microsoft Online Responder, signing certificates are valid for only 14 days and are automatically renewed by the Online Responder service (two days before their expiration).
Due to this restriction, the use of hardware security modules is highly recommended for OCSP response signing certificates, but this again increases the complexity and error-proneness of the setup.
The use of OCSP can only be configured globally at the level of the certification authority
It should be noted here that this is a restriction on the part of the Microsoft certification authority, as CDP/AIA and OCSP addresses can only be set globally at certification authority level. RFC 6960 does indeed provide for the use of CRL distribution points in OCSP signing certificates, but with the Microsoft certification authority it is not possible to set a corresponding exception only for OCSP response signing certificates.
The TameMyCerts policy module for the Microsoft certification authority offers the possibility to define CDP, AIA and OCSP addresses per certificate template.
Such a setup also defeats the purpose of OCSP, as the certificate revocation list must be signed by the same certification authority, and the Microsoft OCSP implementation uses this very list as its data source, as previously stated.
If you configure an OCSP address for issued certificates, it applies to all certificates issued by the certification authority.
The Online Responder should be a domain member in order to be managed in a meaningful way
Another disadvantage becomes apparent here: if the Online Responder servers are not to be located in the same Active Directory as the certification authorities (if they are, one creates a bridge from the Internet to the online certification authorities in the case of Online Responders connected to the Internet), the OCSP response signing certificates cannot be renewed automatically. Manual renewal at two-week intervals is also not practical.
Even if hardware security modules are used, the validity of an OCSP response signing certificate should not exceed a few months. In this case, there is therefore no way around renewing the certificates manually (or scripted if necessary) on a regular basis.
Manual processes can pose a risk to the availability of the Online Responder (see below), while automatic processes pose a security risk (due to authentication and the necessary network connection).
HTTPS is possible, but not useful
OCSP requests are transmitted via the HTTP protocol. Often, for compliance reasons, it is desired that all HTTP traffic be protected via SSL (or TLS) (HTTPS).
Although this is theoretically possible, it only offers disadvantages, since the revocation status of the web server certificate required for SSL would in turn have to be checked, and ultimately no SSL can be used here. There are no advantages because no confidential information is transmitted. Tamper protection is provided by the fact that OCSP responses are signed by the Online Responder using the OCSP response signing certificate.
See also article "Use HTTP over Transport Layer Security (HTTPS) for the CRL distribution points (CDP) and the Online Responder (OCSP) " for more information.
Sequence of an OCSP communication
If an OCSP-enabled application checks the revocation status of a certificate, it evaluates its Authority Information Access (AIA) extension. If there is an entry of the type "On-line Certificate Status Protocol" (object identifier (OID) 1.3.6.1.5.5.7.48.1), the URL stored there is then called up with an OCSP request.
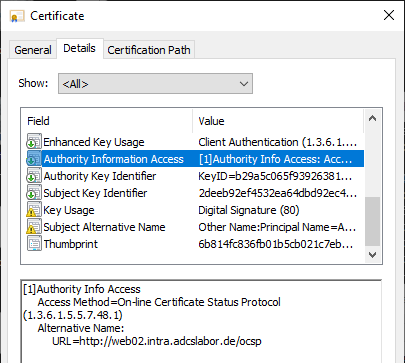
The communication with the Online Responder is done via HTTP and deliberately without SSL. Both the POST and the GET method can be used here.
HTTP-based OCSP requests can use either the GET or the POST method to submit their requests.
— https://datatracker.ietf.org/doc/html/rfc6960#appendix-A.1
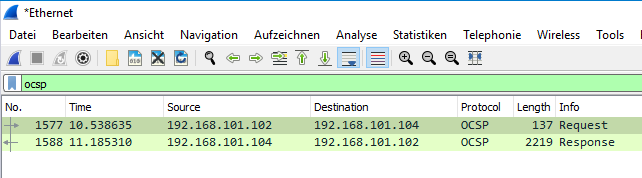
The OCSP request includes the "name hash" and the "key hash" (since both "name matching" and "key matching" are possible, see "Basics: Finding certificates and validating the certification path ") of the issuing certification authority as well as the serial number of the requested certificate.
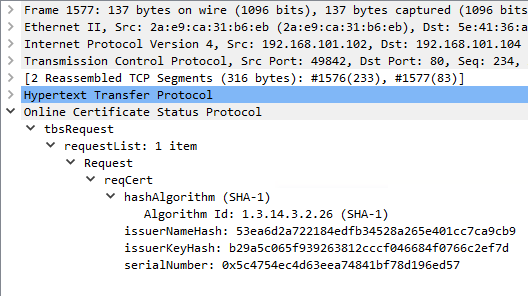
If the Online Responder knows the issuing certification authority, it checks the underlying certificate revocation list of the certification authority to see whether the serial number of the requested certificate is entered there.
The OCSP response is signed with the signing certificate of the Online Responder. The signing certificate must be signed by the same (certification authority) key as the certificate to be verified so that the OCSP response is accepted by the requesting system.
The signed response of the Online Responder contains the status as well as the validity period of the OCSP response.
| Status | Description |
|---|---|
| Good | The certificate is not on a certificate revocation list known to the OCSP responder. |
| Revoked | The certificate is on a certificate revocation list known to the OCSP responder. |
| Unknown | The certificate could not be assigned to or was not issued by a certification authority known to the OCSP responder. |
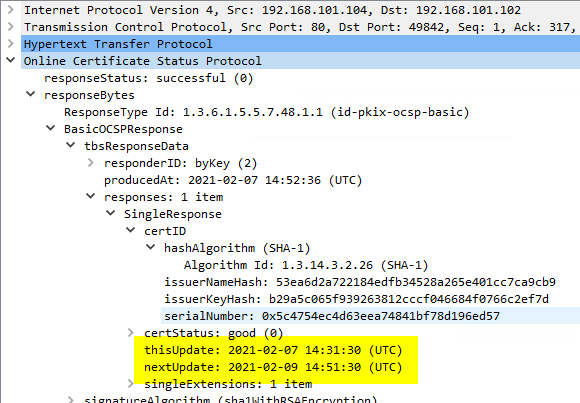
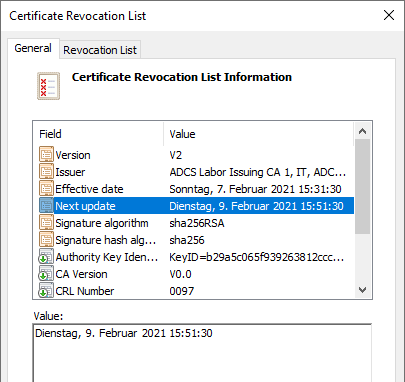
If you take a look at the underlying certificate revocation list of the certification authority, you will find the exact same dates for start and expiration.
Please note that the times in the shown shell dialog are localized, but in the OCSP response the UTC times are given.
Availability of the Online Responder
Availability requirements
The requirements for the availability of the Online Responder depend on various factors:
- Availability of alternative methods for revocation status checking.
- Use cases that depend on the revocation status.
Applications that use the Microsoft CryptoAPI or CAPI for revocation checking fall back on the certificate revocation lists if an Online Responder is unavailable.
If the certificates to be checked are configured without CRL distribution points (i.e. OCSP-only), the availability of the Online Responder is therefore much more critical. A failed Online Responder infrastructure can therefore render all issued certificates and the associated use cases unusable in one fell swoop.
Some applications (for example, Adobe Reader and Adobe Acrobat for document signatures) use OCSP responses as a time stamp to ensure that document signatures continue to be considered valid after the signing certificate used expires.
Factors influencing the availability of an Online Responder
The following factors influence the availability of an Online Responder:
- The network infrastructure (e.g. load balancers, network components, connectivity, name resolution, etc.).
- Server infrastructure setup (will a cluster or a single server be used?).
- Availability of the certification authority and its private keys (both the certificate revocation lists used and the signing certificates for the Online Responders must be signed by it on a regular basis).
- Configuration of the OCSP response signing certificate template (in the default configuration, it is configured for a validity period of two weeks and a renewal two days before expiry).
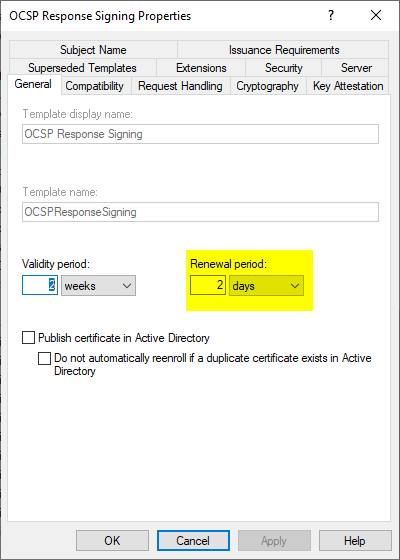
Thus, in the default configuration and depending on the use case, even with a generous configuration of the certificate revocation list validity period and overlap, there would only be a time window of two days in the event of an (assumed) certification authority failure until the Online Responder fails.
The certificate template for the OCSP response signing
The default certificate template for OCSP response signing is configured for a validity period of only two weeks. The background to this short time window is that OCSP response signing certificates must not contain any revocation status information and it is accordingly not possible to revoke a compromised OCSP response signing certificate.
Since the OCSP response signing certificate must always be issued by the corresponding certification authority (using the same key that was used to sign the certificate being verified), autoenrollment cannot be used for the certificate request. The Microsoft Online Responder therefore includes its own routine for certificate requests. It applies the time window configured in the certificate template for certificate renewal. Greater resilience can thus be achieved by configuring this time window to be as long as possible.
See also article "Configuring a certificate template for Online Responder (OCSP) response signing certificates "
External sources
- How Certificate Revocation Works (Microsoft)
- RFC 6960: X.509 Internet Public Key Infrastructure Online Certificate Status Protocol - OCSP (Internet Engineering Task Force)
- Online Certificate Status Protocol (Wikipedia)
- What is the status of revocation checking in browsers? (Ryan Hurst)
- The Slow Death of OCSP | Feisty Duck (Ivan Ristić)