
Basics: Name Constraints
Name constraints are part of the X.509 standard and are described in RFC 5280 . They are a tool that can be used as part of qualified subordination to control the scope of a certification authority certificate in a fine-grained manner.
Excursus: qualified subordination
The objective of qualified subordination is to restrict the extent to which a certification authority or a certification authority hierarchy is trusted.
Components of qualified subordination can be:
| Component | Description |
|---|---|
| Path length constraint (Path Length Constraint) | This can be used to define how many hierarchy levels (i.e. subordinate certification authorities) may follow the certification authority in question. |
| Extended Key Usage constraints (Extended Key Usage Constraints) | This can be used to specify which Extended Key Usages may be accepted in certificates issued by the certification authority. |
| Issuance policy constraints (Issuance Policies) | This can be used to specify for which certificate policies the certification authority may confirm conformity in issued certificates. |
| Name constraints (Name Constraints) | This can be used to define for which namespaces the certification authority may issue certificates. |
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Motivation for using them
Don't forget: PKI is a distributed system. The root CA may belong to a different organization than the subordinate CAs.
Reasons for using name constraints may include:
- As a PKI operator, you delegate certification authority certificates to your customers and want to limit their scope of use to prevent misuse.
- You operate a certification authority whose certificate issuance is delegated to third parties. Examples of this would be certificate requests submitted manually, those submitted via the Network Device Enrollment Service , or those submitted by mobile device management (MDM) systems.
- You want to limit the potential damage if a certification authority is compromised.
A good example of the consistent application of qualified subordination, and of name constraints in particular, is the Bayerische SSL-CA-2015-01 whose CA certificate is publicly viewable.
Specification in the RFC
Name constraints are specified in RFC 5280 . They can only be applied to subordinate certification authority certificates.
The defined constraints can be specified in the form of a list of permitted and/or in the form of a list of prohibited namespaces for the Subject Distinguished Name and the Subject Alternative Names of issued certificates. If prohibited namespaces are defined, they take precedence over permitted namespaces.
The following types of constraints are possible, among others:
| Type | Description |
|---|---|
| directoryName | Constraints on the Relative Distinguished Names (RDNs) in the Subject Distinguished Name. |
| rfc822Name | Constraints on email addresses in the Subject Alternative Name. |
| uniformResourceIdentifier | Constraints on URLs in the Subject Alternative Name. |
| dNSName | Constraints on DNS names in the Subject Alternative Name. |
| iPAddress | Constraints on IP addresses in the Subject Alternative Name. |
As a minimum, the RFC requires that applications that check certificates understand at least constraints on the directoryName and recommends that at least the rfc822Name, uniformResourceIdentifier, dNSName, and iPAddress are also understood.
Please note that name constraints cannot enforce the presence of any of the defined Subject or Subject Alternative Name parts. If the defined part is not present in the certificate request, this is considered valid (in part, restrictions are possible):
Restrictions apply only when the specified name form is present. If no name of the type is in the certificate, the certificate is acceptable.
To ensure that all participants speak a common language as far as possible, standards are defined by the IETF in RFCs (Request for Comments). RFC 5280 , the relevant standard for certificate profiles in PKI, unambiguously requires that the "Name Constraints" certificate extension must be marked as critical.
Conforming CAs MUST mark this extension as critical
Applications that check the certificate chain and do not know the "Name Constraints" certificate extension will therefore not be able to process it and thus will not be able to accept the issued certificates.
Compatibility note: Apple does not play along
For Mac OS, correct processing of name constraints was implemented with version 10.13.3 . There are unconfirmed indications that name constraints might now be supported by Apple iOS.
As is often the case in the area of public key infrastructure, the saying here is once again: "It always depends on the implementation in the application".
And unfortunately there is the problem that all Apple products are not compliant with RFC 5280 since they do not support name constraints. Accordingly, they will reject certificates from correctly constrained certification authorities (at least this part is implemented in compliance with the RFC).
Applications conforming to this profile MUST be able to process name constraints [...] the application MUST either process the constraint or reject the certificate.
Since Apple also does not give browser and app makers the choice of using their own cryptographic libraries, either no Apple devices can be used with name constraints or no name constraints can be used with Apple devices.
The only remaining way out on the PKI side would be to violate the RFC and not mark the name constraints extension as critical.
The Bayerische SSL-CA-2015-01 , mentioned above as a positive example, does exactly that, by the way, and thus does not fully comply with RFC 5280, since the name constraints extension in its certification authority certificate is not marked as critical - the reason is obvious.
The same statement can be found from one of the inventors of Active Directory Certificate Services, who also represented Microsoft in the IETF:
For customers this means if you must interoperate with Opera or Safari (yes even on iPad and iPhone) the use of a certificate with a "Critical" "Name Constraints extension" in it will result in the certificate chain looking invalid. [...] This issue can be addressed by not marking the extension Critical, when this is done the clients that understand Name Constraints will continue to honor the policies expressed in it and those that do not will simply ignore the extension. This is of course a trade-off of security in exchange for compatibility, with that said one with far more positive trade-offs than negative ones.
— Least Privilege and Subordinate Certificate Authorities (Ryan Hurst)
Implementation in Microsoft PKI
Microsoft Active Directory Certificate Services will refuse to issue certificates that violate the name constraints. However, this can be switched off with the CRLF_IGNORE_INVALID_POLICIES flag (not recommended), or one could issue certificates directly using the private key . The aim of name constraints is therefore not (only) to prevent the issuance of invalid certificates, but to ensure their (non-)acceptance by those who are to check or use them.
The name constraints are written into the certification authority certificate of the certification authority concerned (they are set by the respective parent authority).
The constraints can either be included in the certificate request of the certification authority concerned (capolicy.inf ), or the parent certification authority applies an appropriate configuration before issuing the certification authority certificate.
The basic structure of the definition looks like this:
[NameConstraintsExtension]
Include = PermittedSubtrees
Exclude = ExcludedSubtrees
Critical = True

[PermittedSubtrees]
; Direktiven hier

[ExcludedSubtrees]
; Direktiven hier
The definition may also be written in the following alternate notation:
[Strings]
szOID_NAME_CONSTRAINTS = "2.5.29.30"

[Extensions]
Critical = %szOID_NAME_CONSTRAINTS%
%szOID_NAME_CONSTRAINTS% = "{text}"
_continue_ = "SubTree=Include&"
_continue_ = ; Direktiven hier, jede Zeile mit & beenden
_continue_ = "SubTree=Exclude&"
_continue_ = ; Direktiven hier, jede Zeile mit & beenden
The following directives are possible:
| Definition according to RFC 5280 | Entry in capolicy.inf | Example |
|---|---|---|
| directoryName (Subject) | DirectoryName | DC=intra,DC=adcslabor,DC=de |
| dNSName (SAN) | DNS | intra.adcslabor.de .intra.adcslabor.de |
| rfc822Name (SAN) emailAddress (Subject) | @adcslabor.de .adcslabor.de | |
| iPAddress (SAN) | IPAddress | 10.0.0.0, 255.0.0.0 172.16.0.0, 255.255.0.0 192.168.0.0, 255.255.255.0 |
| (not specified) userPrincipalName | UPN | intra.adcslabor.de .intra.adcslabor.de |
The SAN type userPrincipalName is not specified in RFC 5280 because it is proprietary to the Microsoft ecosystem. It is therefore not guaranteed that other PKI implementations can interpret it correctly (or at all).
It is also possible to specify the "empty" keyword. This can be used to explicitly disallow certain Subject Alternative Name types. For the directoryName type this directive cannot be used. For permitted namespaces, the keyword has no effect.
Note on some incorrect documentation
Common documentation claims that it is necessary to put a dot in front of a defined DNS namespace in order to allow subdomains, for example. In fact, this is not required at all. See the corresponding passage in the relevant RFC .
DNS name restrictions are expressed as host.example.com. Any DNS name that can be constructed by simply adding zero or more labels to the left-hand side of the name satisfies the name constraint. For example, www.host.example.com would satisfy the constraint but host1.example.com would not.
Effectively, the enrollee or the certification authority can freely choose the "left" part of the DNS name, including subdomains.
However, it does make a lot of sense to put a dot in front, as this allows only the issuance of identities below the specified domain, but not for the domain itself.
Problem case: Subject Distinguished Name
If you set up name constraints only for DNS names, any identity can still be requested as the Subject Distinguished Name. The only way to restrict the Subject Distinguished Name is to define constraints of type "directoryName".
However, this does not allow you to set constraints for the commonName, which is only one part of the Subject Distinguished Name and from which the identity is formed in many cases. Either you allow all values or none at all.
Thus, it is not possible to restrict the commonName to certain identities (e.g. only hosts below intra.adcslabor.de).
Reasonable exceptions
There are some certificate types that are necessary for operating the certification authority, and their Subject Distinguished Names should therefore always be included in the list of permitted directoryNames:
| Certificate type | Description |
|---|---|
| CA Exchange | Always issued by the certification authority. Contains the commonName of the certification authority with a "-Xchg" suffix and all other RDNs that also appear in the certification authority certificate. If the exception for this is missing, these certificates cannot be generated. As a result, failed certificate requests regularly end up in the database and pkiview.msc is not fully usable. |
| Enrollment Agent | Used for the Registration Authority
certificates of the Network Device Enrollment Service
. If the exception for this is missing, NDES cannot be used with this certification authority. |
| Online Responder | Used for the response signing certificates of the Online Responder
. If the exception for this is missing, no Online Responder can be used with this certification authority. |
A solution for some (but not all) cases
So, in the following example, let's try to set name constraints for a certification authority that is to issue only web server certificates .
Suppose we want to restrict a certification authority that is to issue certificates only for hostnames within the DNS domain intra.adcslabor.de. We know that we cannot restrict the commonName in any meaningful way.
Putting server names into the subject was not even intended when the X.509 standard was defined. Therefore, RFC 2818 has required for HTTPS since as early as 2000 that the Subject Alternative Name, in the form of the dNSName attribute, be used instead of the commonName in the subject.
If a subjectAltName extension of type dNSName is present, that MUST be used as the identity. Otherwise, the (most specific) Common Name field in the Subject field of the certificate MUST be used. Although the use of the Common Name is existing practice, it is deprecated and Certification Authorities are encouraged to use the dNSName instead.
RFC 5280 in turn specifies that in such a case the subject field may be empty:
Further, if the only subject identity included in the certificate is an alternative name form (e.g., an electronic mail address), then the subject distinguished name MUST be empty (an empty sequence), and the subjectAltName extension MUST be present. If the subject field contains an empty sequence, the subjectAltName extension MUST be marked critical.
The subject field identifies the entity associated with the public key stored in the subject public key field. The subject name MAY be carried in the subject field and/or the subjectAltName extension.
[...]
If subject naming information is present only in the subjectAltName extension (e.g., a key bound only to an email address or URI), then the subject name MUST be an empty sequence and the subjectAltName extension MUST be critical.
For this use case, one could at least define a name constraint for a certification authority certificate that does not accept any commonNames in the subject - which, with regard to RFC 2818 (and thus only for web server certificates ), would be perfectly acceptable.
Consequently, this only works if the certification authority is used exclusively for web server certificates. The identities in the certificates can only be mapped in the Subject Alternative Name in the form of a dNSName (or an iPAddress, but this is not discussed here).
It is therefore essential to set a directory name constraint so that no invalid commonNames, but only the defined commonNames, can be used in the certificate request.
The goal can be achieved, for example, by setting the constraint for permitted namespaces to a predefined value, e.g. "CN=INVALID". This means that only an empty subject distinguished name or one of the defined values is possible. However, it is generally sufficient if one of the exceptions for the cases described above is present in order to achieve this goal.
A corresponding content in a minimal capolicy.inf would look like this:
[Version]
Signature= "$Windows NT$"

[Strings]
szOID_NAME_CONSTRAINTS = "2.5.29.30"

[Extensions]
Critical = %szOID_NAME_CONSTRAINTS%
%szOID_NAME_CONSTRAINTS% = "{text}"
_continue_ = "SubTree=Include&"
_continue_ = "DNS = .intra.adcslabor.de&"
_continue_ = "DIRECTORYNAME = CN=ADCS Labor Test Issuing CA 1-Xchg&"

[Certsrv_Server]
LoadDefaultTemplates=0
In addition, it is highly recommended to restrict the Extended Key Usages for the certification authority so that only the defined use cases are supported. A path length constraint is also very useful.
Functional test
For the test, we have a certification authority certificate issued with the defined constraints.
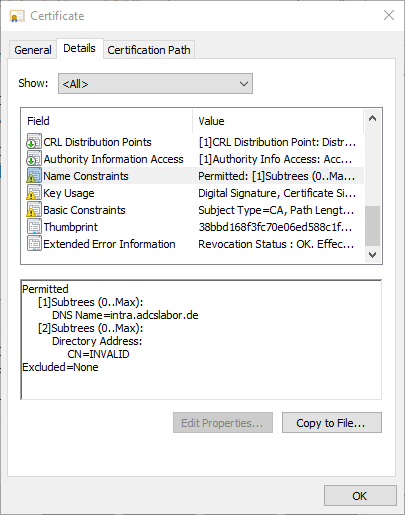
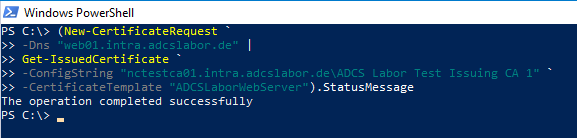
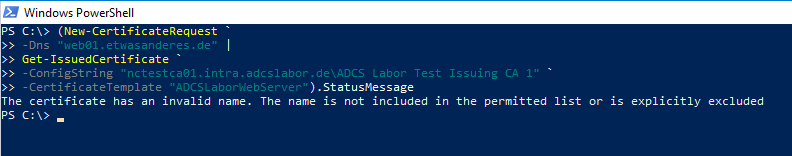
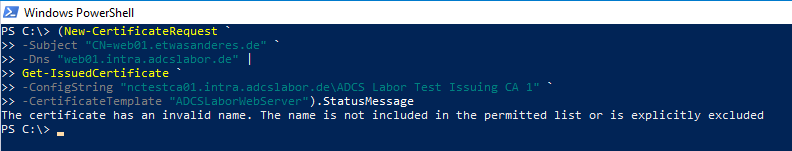
The tests were performed with the PSCertificateEnrollment PowerShell module.
If we request a certificate for a DNS name within intra.adcslabor.de, the certificate request is approved.
If we request a certificate for a DNS name within an undefined DNS domain, the certificate request is rejected as expected.
If we request a certificate for a DNS name within intra.adcslabor.de, and an undefined commonName, the certificate request is rejected as expected.
Assessment of practical suitability
Name constraints allow some influence on the certificate content. The advantage is that violations are also detected when a certificate is checked (...can be - if implemented) and such certificates would then not be accepted.
However, the constraints can only be implemented incompletely. For example, it is only possible to restrict certificate issuance to identities within certain DNS namespaces. However, it is not possible to restrict which identities are requested here.
Likewise, it should be remembered that the RFC only requires that constraints on the directoryName be understood. Thus, there is no guarantee that all participating applications will also understand the other types .
In general, of course, the whole construct is also very inflexible, since no changes are possible afterwards without re-signing the certification authority certificate.
The TameMyCerts Policy Module for the certification authority can be a more flexible alternative.
Conclusion
For some cases, name constraints according to RFC 5280 are therefore completely unsuitable. Even where there are no technical obstacles, they are only suitable to a limited extent for cases in which the enrollee can supply the identity in the certificate request.
External sources
- Constraints: what they are and how they're used (Microsoft)
- X.509 Name Constraints certificate extension - all you should know (Vadims Podans)
- Name Constraints Extension (PKI Solutions, Inc.)
- RFC 5280 - Internet X.509 Public Key Infrastructure Certificate and Certificate Revocation List (CRL) Profile (Internet Engineering Task Force)
- RFC 2818 - HTTP Over TLS (Internet Engineering Task Force)
- Can I restrict a Certification Authority to signing certain domains only? (Discussion on security.stackexchange.com)
- Are X.509 nameConstraints on certificates supported on OS X? (Discussion on security.stackexchange.com)
- Issue 407093: Incorrect Name Constraint Validation (Chromium Project)
- EJBCA - Open Source PKI Certificate Authority - User Guide (PrimeKey)
- Apple iOS 9 bug regarding CA's name constraints (Ivo Vitorino on LinkedIn)
- About the security content of macOS High Sierra 10.13.3, Security Update 2018-001 Sierra, and Security Update 2018-001 El Capitan (Apple)