
Restoring certificates from the SMTP Exit Module data
If you restore a certification authority from a backup after a disaster has occurred , you will probably find that certificates were issued in the period between the last backup and the system failure with corresponding data loss.
These certificates are now not stored in the restored certification authority database, so they cannot be restored if needed.
If you are using the SMTP Exit Module, you can at least determine the serial numbers of the certificates from the sent e-mails and revoke them.
Sometimes it is necessary for a certificate issued by a certification authority to be withdrawn from circulation even before its expiration date. To make this possible, a certification authority maintains a certificate revocation list (CRL). This is a signed file with a relatively short expiration date, which is used in combination with the certificate to check its validity.
The basis for the successful restore of a certification authority in the event of a disaster is that a functioning backup is available. How to create one is described in the article "Creating a backup of a certification authority ".
Instead of the SMTP Exit Module, it would also be possible to develop your own exit module which writes the certificates, for example, to the file system (on a remote server or in connection with a DFS replication) or uploads them to an external database.
Procedure
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Check if the serial number already exists
First, check if the serial number already exists in the certification authority database.
certutil -view -restrict "SerialNumber={Seriennummer}"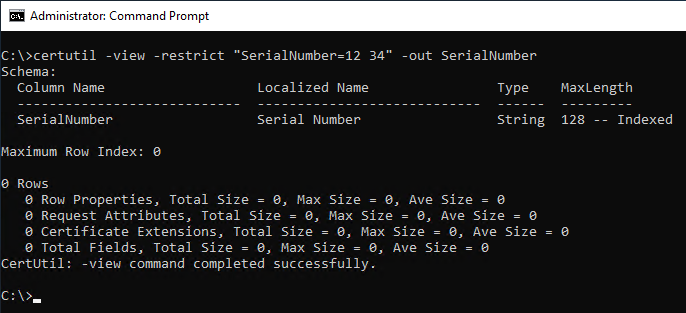
Create dummy certificate
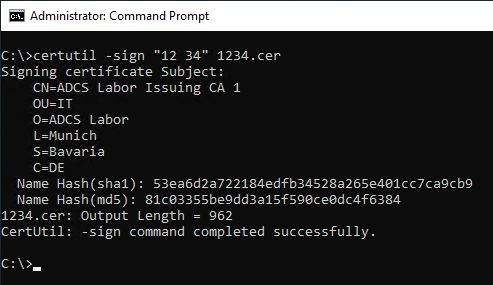
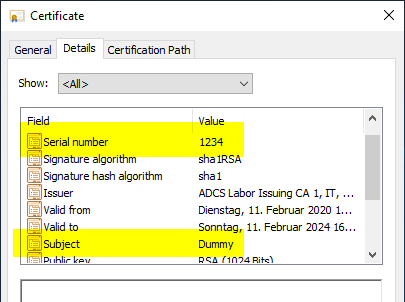
In the event of a disaster, in most cases one is no longer in possession of the certificates. Since the revocation of a certificate requires that a corresponding certificate is in the certification authority database, a dummy certificate with the corresponding serial number must first be generated. As "signing certificate", select that of the certification authority.
certutil -sign "{Seriennummer}" {Dateiname}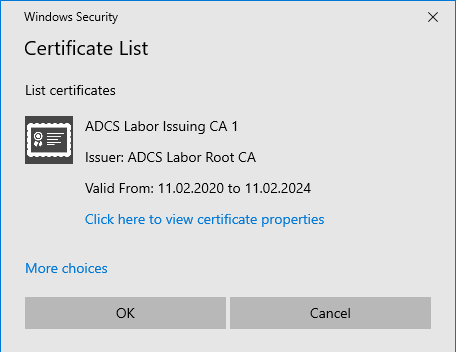
Import dummy certificate into the certification authority database
The created certificate can now be imported into the certification authority database.
certutil -importcert {Dateiname}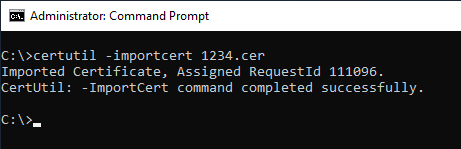
Certificate revocation
It can then be revoked via the Certification Authority management console or the command line.
certutil -revoke {Seriennummer} {Grundcode}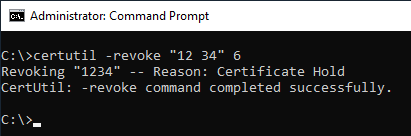
The possible codes for the revocation reason can be found in the table below:
| Code | Designation | Description |
|---|---|---|
| 0 | Unspecified | This is the default setting and indicates that there is no specific reason for the revocation. |
| 1 | Key Compromise | The private key of a certificate was stolen or otherwise known to unauthorized third parties. |
| 2 | CA Compromise | The private key of the certification authority was stolen or otherwise known to unauthorized third parties. |
| 3 | Affiliation Changed | If the content of the certificate (e.g. the name of the user) has changed, a new certificate must be issued. |
| 4 | Superseded | The revoked certificate was replaced with a new certificate. |
| 5 | Cessation of Operation | The operation of the service belonging to the certificate was discontinued, for example, because there is a new service under a different name. |
| 6 | Certificate Hold | The certificate is revoked temporarily. This revocation type is the only one where the revocation can be subsequently undone. |
| 8 | Remove from CRL | If a certificate was revoked with reason "Certificate Hold" and delta CRLs are used, the unrevoked certificate is listed in the delta CRL with this code until the entry in the base CRL is removed. |
| -1 | Unrevoke | If a certificate has been revoked with reason "Certificate Hold", this code can be used to unrevoke it via the command line. Likewise, in the audit event 4870 the undoing of a certificate revocation is marked with this code. |
Publish a new CRL
For the revocation to be effective, a new CRL still needs to be published.
certutil -crlSee also article "Create and publish a certificate revocation list ".
Please note that until the expiration date of the previous CRL, it cannot be guaranteed that PKI participants will recognize the revocation as such, since (at least in the Windows ecosystem) CRLs are kept in a client-side cache . The same also applies to responses from the Online Responder (OCSP) .
Error when using Windows Server 2008 R2
The following error may occur on Windows Server 2008 R2:
CertUtil: -CRL command FAILED: 0xc0000005 (-1073741819)
CertUtil: The instruction at 0x%081x referenced memory at 0x%081x. The memory could not be %s.
In this case, it helps to install this hotfix.
Can I also revoke certificates this way if my certification authority has been compromised?
Triggered by the work of Will Schroeder and Lee Christensen in the summer of 2021, discussions have developed that certificates signed by bypassing the certification authority could also be revoked in this way.
In principle and from a purely technical point of view, this is correct, but it does not solve the actual problem. If someone is able to sign certificates with the private key of the certification authority, a single certificate revocation helps quite little, since control over the private key of the certification authority is still lost.
If the private key of a certification authority is compromised, in my opinion the only way to return to "secure" operation is to decommission the affected certification authority as quickly as possible while removing trust in it (at least revoking the CA certificate), and a complete rebuild.
It goes without saying that the underlying attack vectors must have been shut down beforehand.
External sources
- You cannot publish a CRL for an imported certificate after the certificate is revoked in Windows Server 2008 R2 (Microsoft)
- Crafting a dummy certificate with specific serial number in Microsoft ADCS (PKI Solutions, Inc.)
- Certified Pre-Owned (Will Schroeder)