
How the TameMyCerts Policy Module for Active Directory Certificate Services (ADCS) can detect and prevent attacks against the ESC6 and ESC7 attack vectors
With the supposedly good intention of making it possible to issue such certificate requests with a SAN, unfortunately far too many guides advise enabling the EDITF_ATTRIBUTESUBJECTALTNAME2 flag on the certification authority.
If this flag is enabled, a very large attack surface is offered, as any enrollee can now instruct the certification authority to issue certificates with any content. This type of attack is known in the security scene as ESC6 and ESC7 .
TameMyCerts is a policy module to secure the Microsoft certification authority (Active Directory Certificate Services). It extends the functions of the certification authority and enables the extended application of rule sets to enable the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem and is available under a free license. It can be downloaded via GitHub and used free of charge.
TameMyCerts is open source and can be used free of charge. For use in the corporate sector, however, we recommend concluding a maintenance contract. This ensures that you receive qualified support and that the module can be further developed to a high quality in the long term.
ESC6 and ESC7 exploit certification authorities that have the EDITF_ATTRIBUTESUBJECTALTNAME2 flag enabled globally. If this flag is enabled in the configuration of a certification authority - whether intentionally or by mistake - an attacker can send a request attribute with malicious content to the certification authority while submitting a certificate request. The certification authority is then instructed to enter the content of the submitted attribute in the Subject Alternative Name (SAN) of the issued certificate, regardless of what was configured in the certificate template.
TameMyCerts ensures that such attempts to exploit the certification authority are detected and prevented if the flag should be enabled on the certification authority. The rejected certificate request is logged so that an alarm can be raised and further measures taken.
The fact that TameMyCerts can detect malicious request attributes and log corresponding attempts is the core of the Certiception Honeypot Toolkit for Active Directory Certificate Services and thus allows attackers to be unmasked at an early stage.
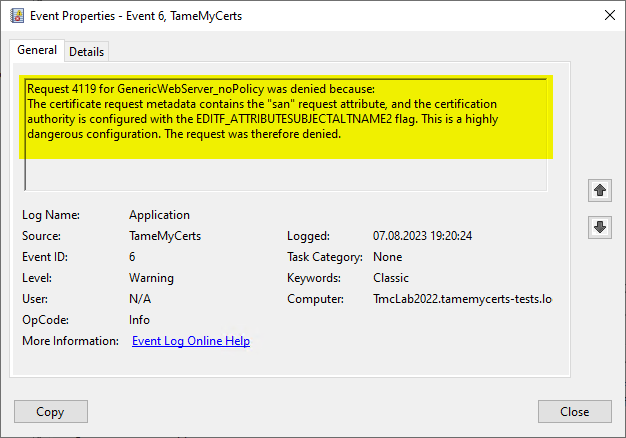
Preventing ESC6 and ESC7 attacks with TameMyCerts
Administrators sometimes enable this flag with the intention of attaching SAN certificate extensions to certificate requests that do not include one, for example because the application or appliance used cannot create certificate requests with a SAN. In most cases, these are web server certificates that require a SAN extension for modern browsers to accept the connection. To solve this problem, TameMyCerts has a corresponding function to securely and automatically transfer detected DNS names and IP addresses from the Subject Distinguished Name to a newly created SAN extension .