
How the TameMyCerts Policy Module for Active Directory Certificate Services (ADCS) can repair incoming certificate requests to make them RFC compliant
Starting with version 58, Google has decided to remove support for the Subject Distinguished Name of web server certificates in the Chrome browser and instead only accept certificates with Subject Alternative Name.
Since then, web server certificates without a Subject Alternative Name in the form of a dNSName have been rejected by Google Chrome and other Chromium -based browsers (i.e. also Microsoft Edge ). Other browser manufacturers quickly adopted this approach, so that this problem now affects all popular browsers.
The problem in the corporate environment
This behavior is fully compliant with IETF RFC 2818 , which dates back to the year 2000. Certificates for web servers must therefore use the Subject Alternative Name (SAN) in the form of a DNS name for their identity.
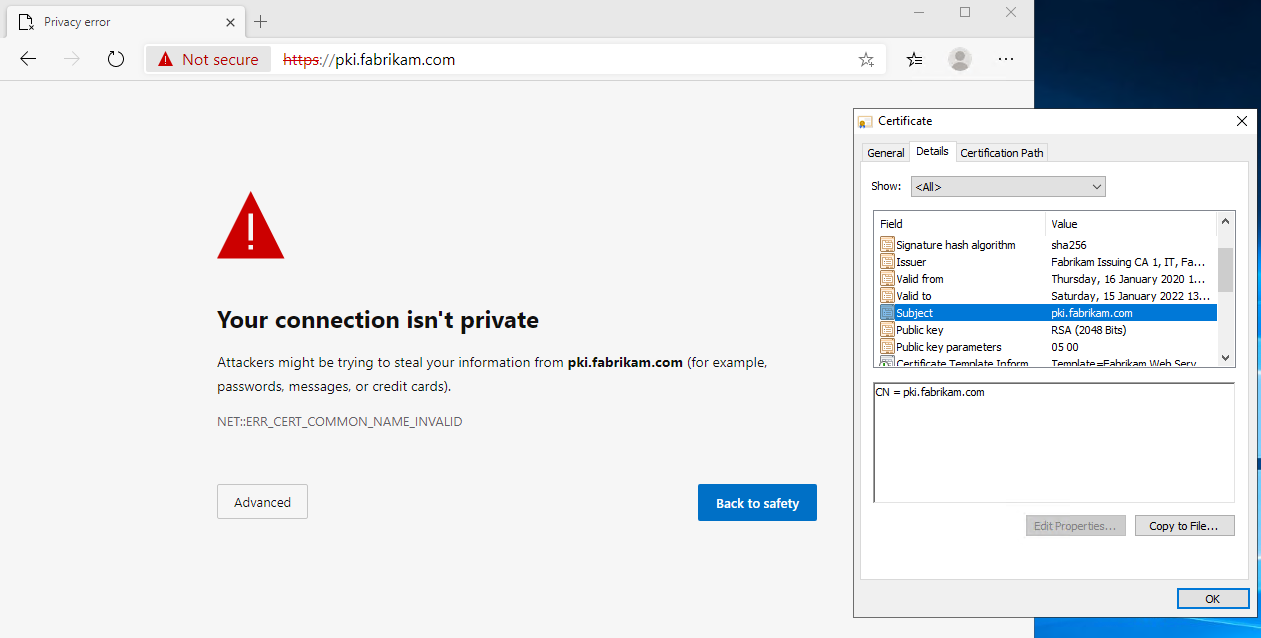
The certificate used does not contain a Subject Alternative Name for the identity and is therefore displayed as invalid.
Unfortunately, there are still many products (e.g. firewalls, telephone systems, routers and other appliances) in use in companies that cannot create certificate requests with a SAN.
Workarounds are dangerous
With the supposedly good intention of making it possible to issue such certificate requests with a SAN, far too many guides unfortunately advise enabling the flag EDITF_ATTRIBUTESUBJECTALTNAME2 on the certification authority.
However, this opens up a huge attack surface, as the certification authority then accepts any SANs from the enrollee for all published certificate templates - including those of malicious actors, which in the worst case can lead to a complete takeover of the Active Directory .
Workarounds are cumbersome
This means that a responsible PKI administrator previously only had the cumbersome, manual option to subsequently add a SAN to a certificate request .
Fortunately, there are better ways to reach your destination.
The solution
With the TameMyCerts Policy Module for Microsoft Active Directory Certificate Services, there is now a way to securely and fully automatically correct corresponding certificate requests - without having to activate insecure settings on the certification authority.
TameMyCerts is a policy module to secure the Microsoft certification authority (Active Directory Certificate Services). It extends the functions of the certification authority and enables the extended application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem and is available under a free license. It can be downloaded via GitHub and used free of charge.
TameMyCerts even recognizes whether corresponding insecure flags are set on the certification authority and rejects certificate requests that exploit the setting.
TameMyCerts is open source and can be used free of charge. For use in the corporate sector, however, we recommend concluding a maintenance contract. This ensures that you receive qualified support and that the module can be further developed to a high quality in the long term.
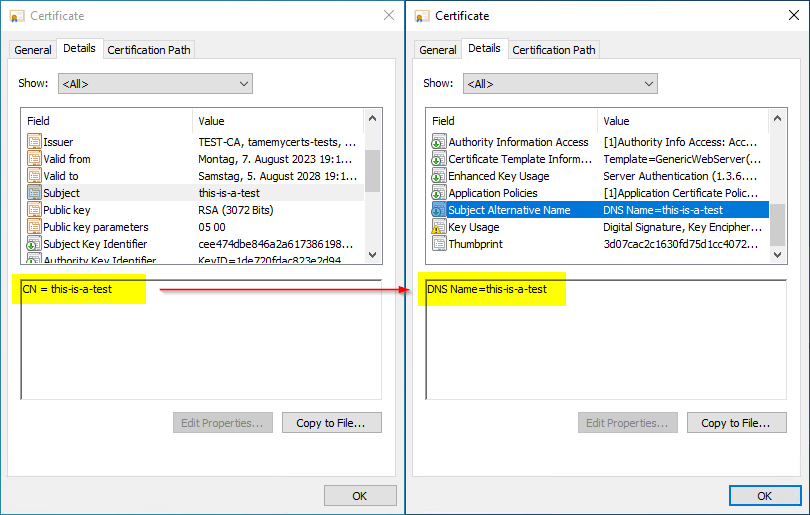
The DNS name found in the Subject Distinguished Name was automatically transferred to a SAN certificate extension.