
Create and publish a certificate revocation list
Sometimes it is necessary for a certificate issued by a certification authority to be taken out of service even before its expiration date. To make this possible, a certification authority maintains a certificate revocation list (CRL). This is a signed file with a relatively short expiration date, which is used in combination with the certificate to check its validity.
After a certificate has been revoked, a new CRL must be created and published so that entities that check the revocation status are informed of the revocation. Since the CRL has a relatively short expiration date, it must be reissued at regular intervals even if the content is not changed.
Required permissions
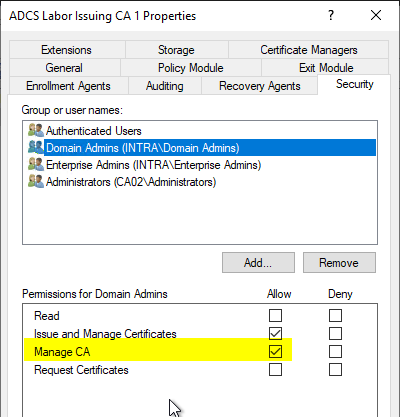
To create a CRL, the executing user needs the "Manage CA" permission on the certification authority on which the CRL is to be issued.
Creating a CRL via the command line
A CRL can be created with the following command line command with elevated privileges ("Run as administrator"):
certutil -crl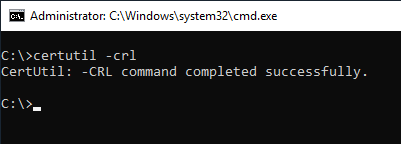
You will be informed via the command line whether the command was successful.
Creating a CRL via the graphical user interface
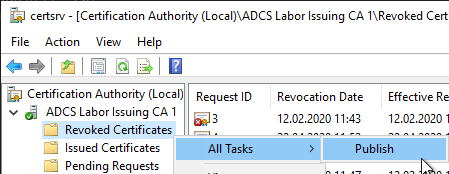
In the Certification Authority management console (certsrv.msc), right-click "Revoked Certificates" and select "All Tasks" - "Publish".
In the following dialog you can choose whether you want to issue a base CRL or (if enabled) a delta CRL.
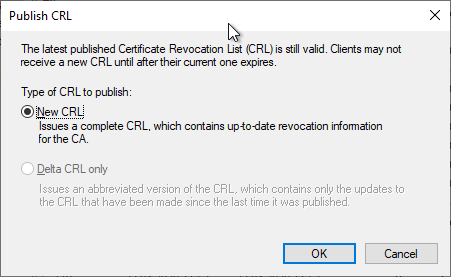
You do not get a direct feedback whether the command was successful. If there is no error message, the CRL has been issued.
Publishing the CRL
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Depending on the configuration of the certification authority, it may now still be necessary to publish the CRLs to the CRL distribution points (CDP).
- The configuration of the CRL distribution points of a certification authority is described in the article "Configuring the CRL distribution points (CDP) and the Authority Information Access (AIA) extension of a certification authority".
- Manual publishing to an LDAP CDP is described in the article "Publishing a certificate revocation list to an Active Directory CRL distribution point ".
Optional: Perform emergency signing of certificate revocation lists
The most important component of a PKI in terms of availability is not the certification authority, as is often assumed, but the CRL distribution points. If a certification authority is unavailable, initially no new certificates can be issued, but the certificates already issued can continue to be used without hindrance as long as their revocation status can be verified. In addition to the pure availability of the CRL distribution points, the revocation information must of course also be valid in terms of its signature. CRLs have a defined expiration date after which they can no longer be used. If a certification authority has now failed, it can also no longer publish new CRLs. The process of emergency signing of CRLs is provided for this case.
The procedure for performing an emergency signing of a CRL is described in the article "Performing emergency signing of certificate revocation lists ".