Configuring a Certificate Template for Online Responder (OCSP) Response Signing Certificates
To use the Online Certificate Status Protocol (OCSP), it is necessary to configure an appropriate certificate template.
The Online Responder (Online Certificate Status Protocol, OCSP) is an alternative way of providing revocation status information for certificates. Thanks to OCSP, entities that want to check the revocation status of a certificate do not have to download the complete list of all revoked certificates, but can send a specific request for the certificate in question to the Online Responder. For a more detailed description, see the article "Basics: Online Responder (Online Certificate Status Protocol, OCSP) ".
Certificate template configuration
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
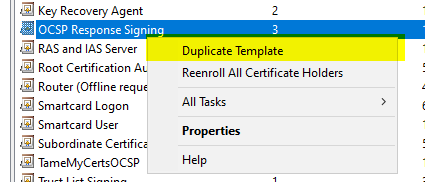
Active Directory Certificate Services ships with the default certificate template "OCSP Response Signing", which should be used as the starting point for a new certificate template.
"Compatibility" tab
Support for OCSP was introduced with Windows Vista and Windows Server 2008. Since OCSP requires some special settings, the default certificate template for OCSP is always a version 3 certificate template.
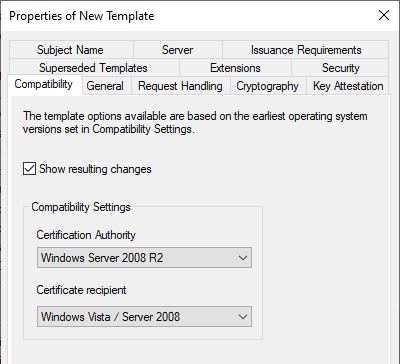
The compatibility settings can therefore be kept unchanged.
"General" tab
By default, two weeks are configured for the validity period ("Validity Period") and two days for the renewal period ("Renewal Period").
Since OCSP response signing certificates cannot be revoked, the shortest possible validity period makes a lot of sense.
The OCSP response signing certificates are not requested and renewed by autoenrollment, but by the Online Responder directly. It evaluates the certificate renewal setting and renews the certificate according to the settings.
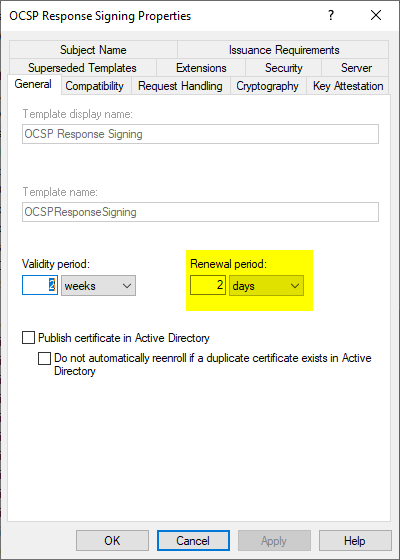
In order to achieve the greatest possible resilience in the event of a failure of the certification authority, a logic similar to CRL overlap should be applied, i.e. the aim should be to renew the certificate as early as possible. If this is not possible, the previous certificate can continue to be used for as long as possible in this way.
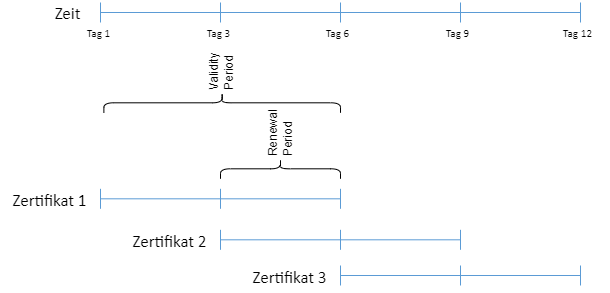
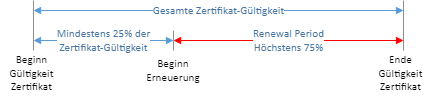
Note that, in contrast to autoenrollment, the rule that 80% of the certificate validity must have passed first does not apply. However, the certificate template configuration dialog does not allow renewal periods greater than 75% of the certificate validity.
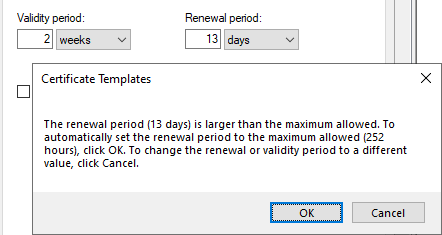
The ratio between certificate validity and renewal period should be planned accordingly.
"Cryptography" tab
Since this is a schema version 3 certificate template , and the Online Responder only supports these, only key storage providers can be used.
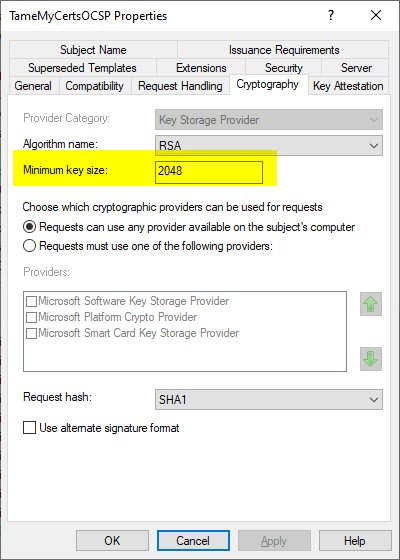
By default, the key size is configured to 2048 bits with an RSA key. By now, it is advisable to increase this to 3072 bits . The use of elliptic curves is technically possible , but may cause compatibility problems.
To protect the key material, it can be very useful to use a hardware security module (HSM) . However, care must be taken that there are no storage space restrictions (e.g. when using a SafeNet HSM) that could jeopardize availability at a later date.
"Server" tab
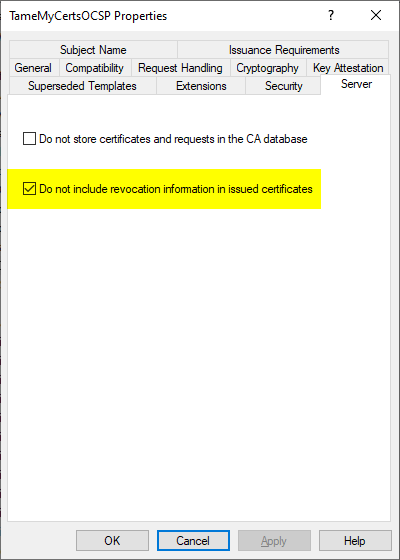
Since OCSP response signing certificates themselves must not contain revocation status information, the "Do not include revocation information in issued certificates" option must be enabled. This is already the case by default.
"Security" tab
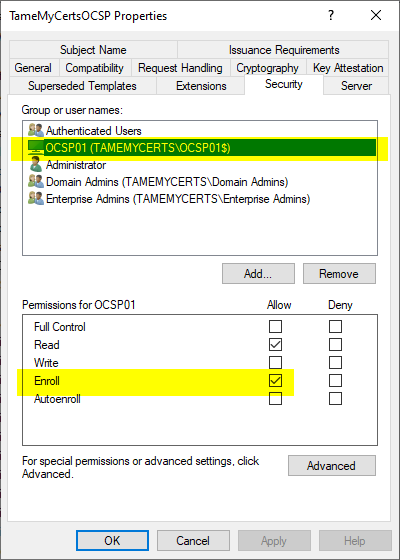
To request the certificates, the computer accounts of the Online Responder servers must be granted the "Enroll" permission (note: not "Autoenroll"). This can be done by explicitly adding the computer accounts or via a security group.