
Perform emergency signing of certificate revocation lists
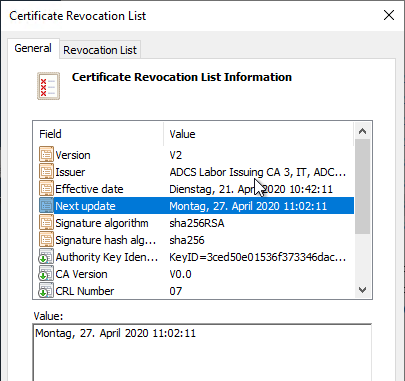
The most important component of a PKI in terms of availability is not the certification authority, as is often assumed, but the CRL distribution points. If a certification authority is unavailable, initially no new certificates can be issued, but the certificates already issued can continue to be used without hindrance as long as their revocation status can be verified. In addition to the pure availability of the CRL distribution points, the revocation information must of course also be valid in terms of its signature. Certificate revocation lists (CRLs) have a defined expiration date after which they can no longer be used. If a certification authority has now failed, it can also no longer publish new CRLs. The process of emergency signing of CRLs is provided for this case.
Basics
The basic idea behind emergency signing is to re-sign an existing CRL directly with the private key, bypassing the certification authority, and to enter a new, extended expiration date in the CRL in the process. So if the failure of the certification authority lasts longer than the validity of the CRL, the emergency CRL can extend it as often as needed, as long as access to the private key of the certification authority is possible.
The first step to be taken after a certification authority failure should therefore not be to analyze the error or even to restore the certification authority from the backup , but first to generate an emergency CRL.
There is also nothing to be said against proactively carrying out this process as long as the certification authority is still working properly. In this way, provisions have already been made for the event of a failure of the certification authority. Also for the migration of a certification authority to another server or in case of upcoming maintenance work, a prior emergency signing can be very helpful.
Performing the emergency signing
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
If the certification authority is no longer available, the private key of the certification authority must first be restored on another system. See the following articles:
- Restoration of a certification authority certificate with software key
- Restoration of a Certification Authority Certificate with Hardware Security Module (HSM)
The emergency signing of the CRL is performed with the following command line command:
certutil -sign {Sperrliste-Alt}.crl {Sperrliste-Neu}.crl now+{Tage}:{Stunden} -2.5.29.46The argument -2.5.29.46 removes the "Freshest CRL" extension from the generated emergency CRL. This extension normally refers to a delta CRL, which would naturally expire in the same way as the base CRL. For this reason, the reference to the delta CRL is removed.
For example, if a CRL with the file name crl.crl is to be written into an emergency CRL called emergency.crl with a validity of 30 days, one would execute the following command.
certutil -sign crl.crl emergency.crl now+30:00 -2.5.29.46During the signature process, you are prompted to select a certificate for signing the CRLs. Here, exactly the certification authority certificate matching the CRL must be selected. Particularly if the certification authority has multiple certification authority certificates and keys, attention must be paid to this fact, otherwise the CRL will not have a valid signature.
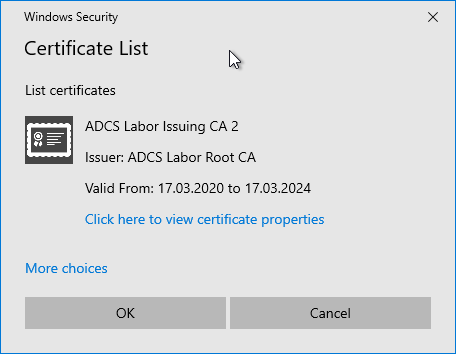
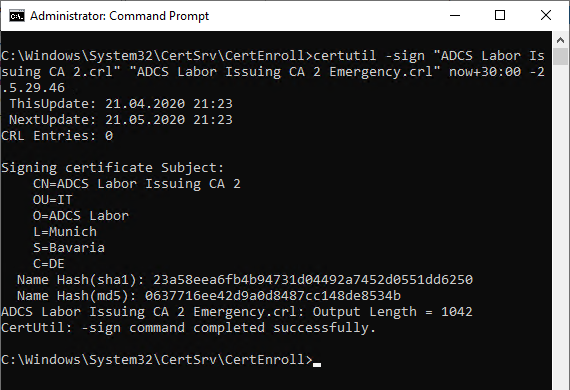
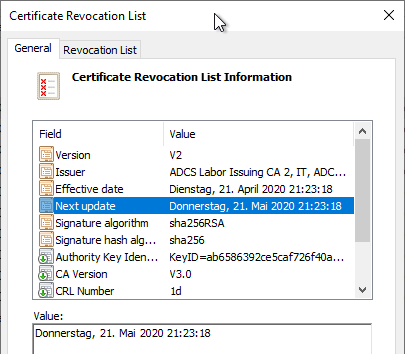
The emergency CRL now generated should have an expiration date of 30 days from the time of the emergency signature.
Publishing the emergency CRLs to the CRL distribution points
The emergency CRL can now either be kept for emergency use or published directly to the CRL distribution points.