Publishing a certificate revocation list (CRL) to an Active Directory CRL distribution point (CDP)
Sometimes it is necessary for a certificate issued by a certification authority to be withdrawn from circulation even before its expiration date. To make this possible, a certification authority maintains a certificate revocation list. This is a signed file with a relatively short expiration date, which is used in combination with the certificate to check its validity.
In some cases (for example, with an offline certification authority, or if non-standard LDAP CRL distribution points have been configured), the certificate revocation list must be manually published to Active Directory.
Required permissions
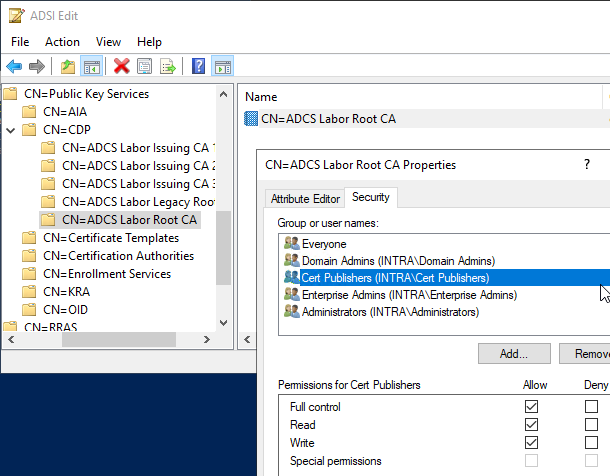
To publish the certificate revocation list in Active Directory, you need write permissions on the corresponding cRLDistributionPoint object in the CDP path below the Public Key Services container in the Configuration partition of the Active Directory forest. By default, the following have this right:
- The Administrators security group of the root domain of the forest
- The Domain Admins security group of the root domain of the forest
- The Enterprise Admins security group of the forest
- The Cert Publishers security group of the root domain of the forest
Required configuration on the certification authority
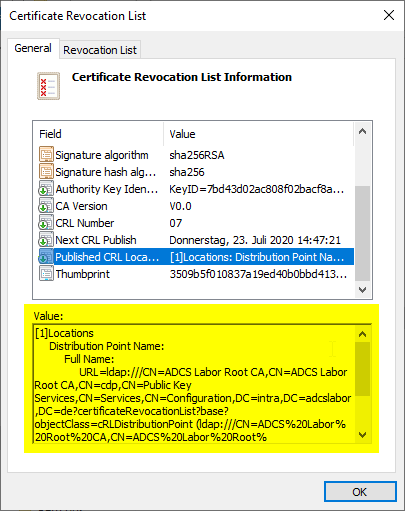
In order for the certificate revocation list to be manually written to Active Directory, a "Published CRL Locations" extension is required within the certificate revocation list.
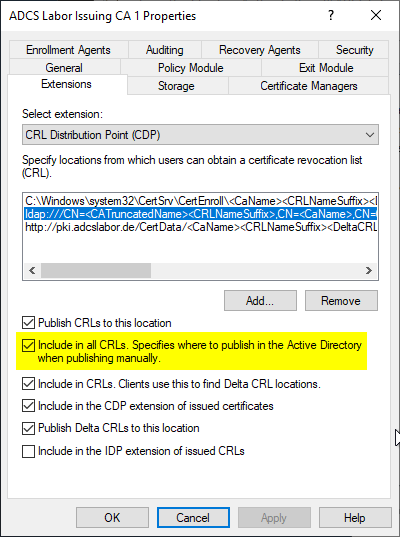
This extension is only written to the certificate revocation list if, for the corresponding CDP extension on the certification authority, the option "Include in all CRLs. Specifies where to publish in the Active Directory when publishing manually." has been set.
Create a certificate revocation list
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
If no current certificate revocation list has been created yet, it must be created first. The procedure is described in the article "Create and publish a certificate revocation list ".
Publish the certificate revocation list in Active Directory
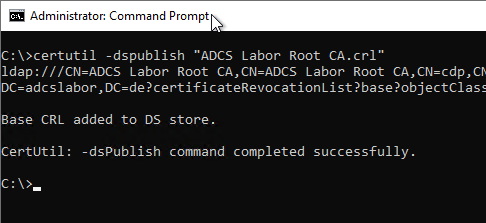
The certificate revocation list can be published with the following command.
certutil -dspublish {Dateiname}As mentioned before, the executing user needs write permissions on the corresponding object.
If the object does not yet exist, it must first be created with the "-f" switch. This requires write permissions to the parent LDAP path.