
Configuring the Trusted Platform Module (TPM) Key Attestation
Since Windows 8, it is possible to protect the private keys of certificates with a Trusted Platform Module (TPM), if one is present . This makes the key non-exportable - even with tools like mimikatz.
However, it is not obvious at first glance that it cannot be guaranteed that a TPM is really used. It is true that no request via the Microsoft Management Console or autoenrollment is possible if the computer does not have a TPM.
However, the configuration in the certificate template is only a default setting for the client. When a certificate is requested, the certification authority will not explicitly check whether a Trusted Platform Module was really used .
To ensure that the private key of a certificate request has really been protected with a Trusted Platform Module, only the TPM Key Attestation remains.
How it works
During TPM Key Attestation, the certification authority checks whether the certificate request has been signed with the Trusted Platform Module's Endorsement Key. This can be achieved in two ways:
- EKPUB: This variant explicitly trusts the individual endorsement keys of the TPM of the individual machines. These are explicitly stored on the certification authority.
- EKCERT: In this variant, the manufacturer certification authorities of the TPMs of the individual machines are trusted. The TPMs are identified on the basis of the endorsement certificate. The manufacturer certificates are stored on the certification authorities in a special trust store.
The third option, User Credentials, in which the user confirms that the certificate request has been protected with a TPM by means of his credentials, is of course not really secure and is therefore not discussed further here.
Setting up the EKPUB method on the certification authority
This method has the disadvantage that it does not scale well. Without a management solution, it will be practically impossible to determine (in a secure way!) all endorsement keys.
The EKPUB method is the most stringent and is therefore also considered to be "High Assurance Level".
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Exporting and storing endorsement keys
A directory is created on the certification authority in which the checksums of the endorsement keys are saved as a file. The following command is then used to include the directory in the configuration of the certification authority.
certutil.exe -setreg CA\EndorsementKeyListDirectories +"{Verzeichnisname}"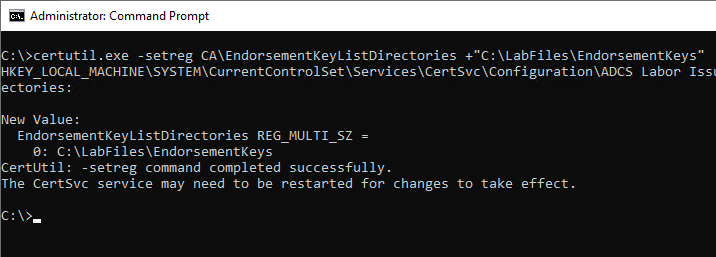
The following Windows PowerShell command can be used to identify the endorsement key hash of a Trusted Platform Module and write it to a compatible file.
New-Item `
-Path (Get-TpmEndorsementKeyInfo -HashAlgorithm SHA256).PublicKeyHash `
-ItemType File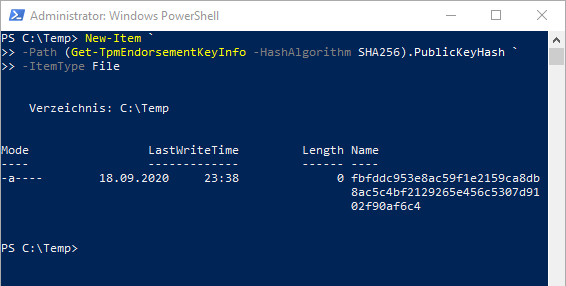
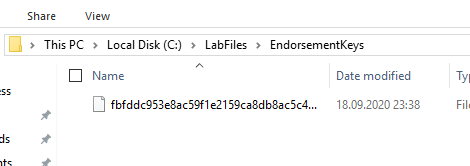
These files must now be saved for each client computer in the directory previously configured on the certification authority.
Setting up the EKCERT method on the certification authority
The EKCERT method is considered "Medium Assurance Level". It has the advantage that it is not necessary to determine each individual endorsement key. Instead, the manufacturer certification authorities are trusted, which (hopefully) have signed an endorsement certificate for the respective Trusted Platform Module.
Creating certificate stores on the certification authority
First, two new certificate stores must be created on the certification authority:
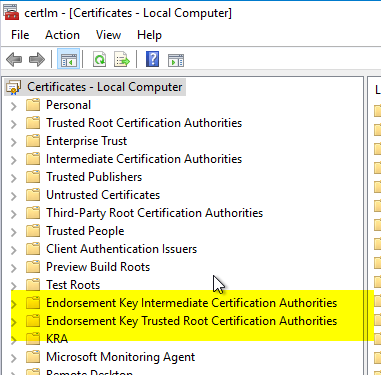
- Endorsement Key Trusted Root Certification Authorities
- Endorsement Key Intermediate Certification Authorities
This can be done with the following Windows PowerShell commands:
cd Cert:\LocalMachine
New-Item -Name EKROOT
New-Item -Name EKCA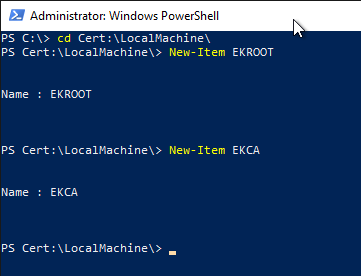
Afterwards, these certificate stores should show up in the Microsoft Management Console (MMC) for computer account certificates (certlm.msc).
Determining the certification authority certificates
Microsoft offers a cabinet file for the Host Guardian Service (HGS), which contains the manufacturer certification authorities for the most common Trusted Platform Modules. This can also be used for the TPM Key Attestation.
The latest version of the list can be downloaded from this link . Since it is very complex to maintain all manufacturer certificates, this is a useful starting point.
If you do not want to use this option, or if the manufacturer certificate of a computer is not included, it can also be extracted manually from the TPM of a computer. Determining a manufacturer certificate from a Trusted Platform Module is described in the article "Determining and exporting a Trusted Platform Module (TPM) endorsement certificate ".
Unfortunately, not every TPM has an endorsement certificate, so it may also be the case that the EKCERT method cannot be used for certain computer models.
Importing the certification authority certificates
First of all, the code signature of the cabinet file should be checked.
Get-AuthenticodeSignature .\TrustedTpm.cab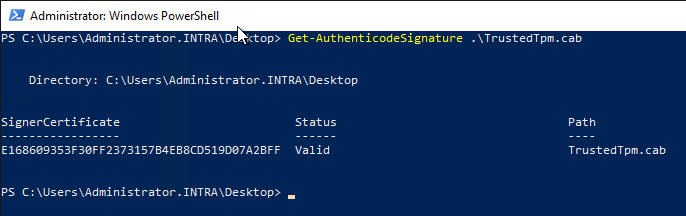
Afterwards the cabinet file can be unpacked:
mkdir .\TrustedTPM
expand.exe -F:* TrustedTpm.cab .\TrustedTPM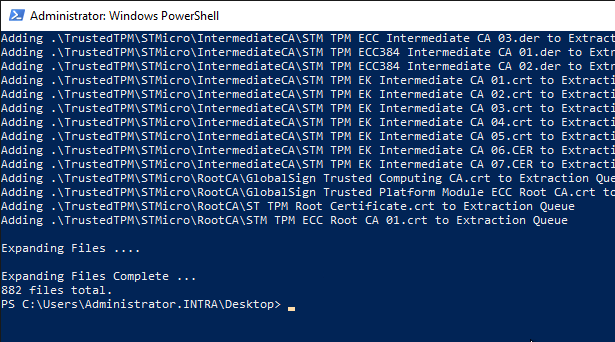
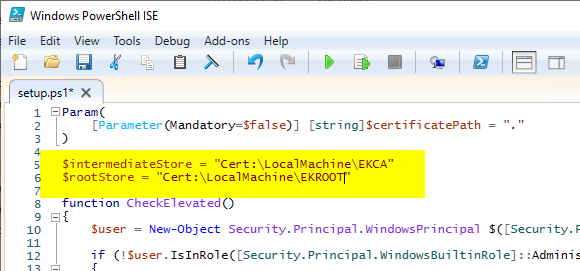
The folder contains the certificates and, conveniently, an installation script. However, since this is intended for the Host Guardian Service, it must be edited to be used for a certification authority.
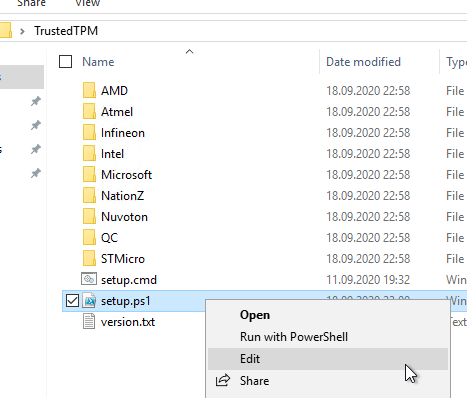
The variables $intermediateStore and $rootStore are adjusted as follows:
$intermediateStore = "Cert:\LocalMachine\EKCA"
$rootStore = "Cert:\LocalMachine\EKROOT"
The file is digitally signed. Changing the file will invalidate the signature, which we have to accept in this case.
Now the certificates can be imported with the script.
.\setup.ps1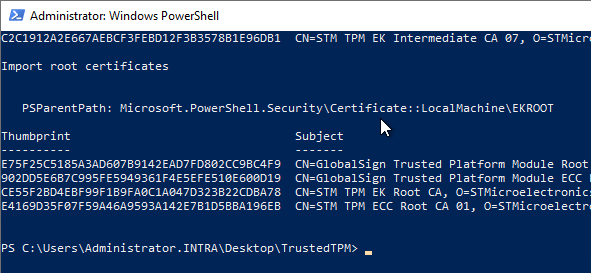
The two trust stores should now be populated.
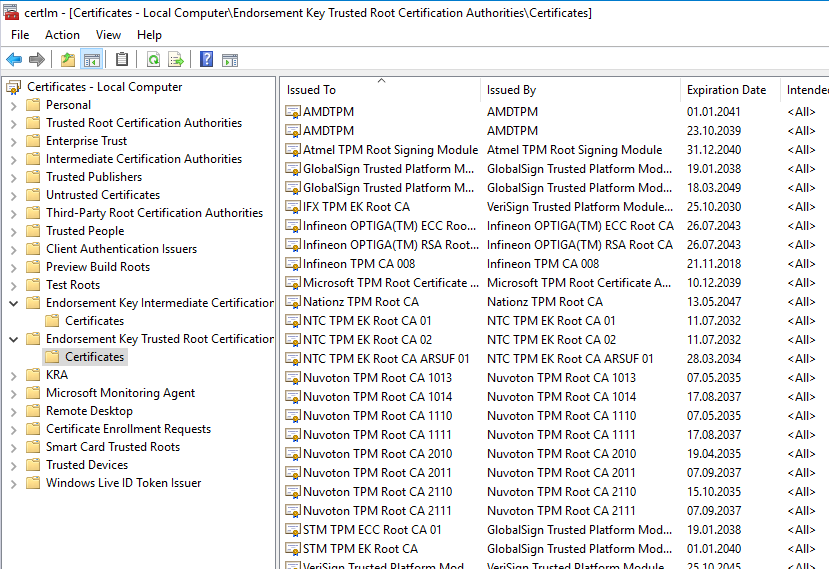
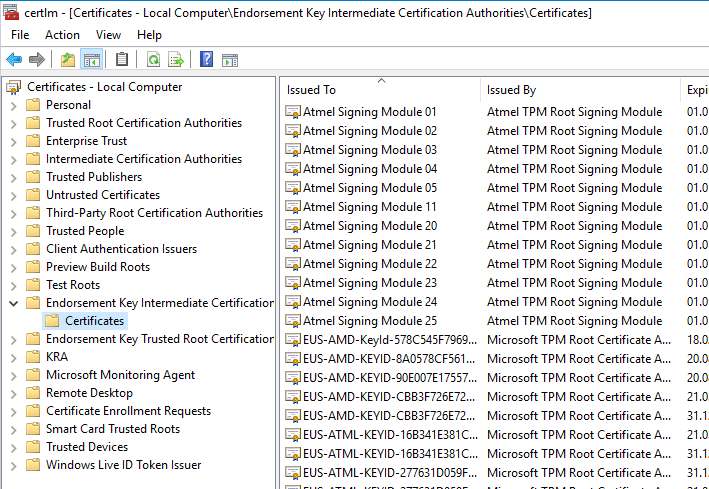
Functional test
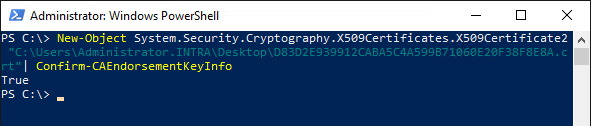
Whether a certification authority trusts a particular endorsement certificate for TPM Key Attestation can be checked with the following PowerShell command:
New-Object System.Security.Cryptography.X509Certificates.X509Certificate2 "{Pfad-zum-Zertifikat}"| Confirm-CAEndorsementKeyInfoFor exporting an endorsement certificate, see the article "Determining and exporting a Trusted Platform Module (TPM) endorsement certificate ".
Configuring the certificate template
In order to be able to issue TPM-protected certificates, a certificate template must first be configured that uses the Microsoft Platform Crypto Provider . This process is described in the article "Configuring a certificate template to use the Microsoft Platform Crypto Provider to enable private key protection by a Trusted Platform Module (TPM) ".
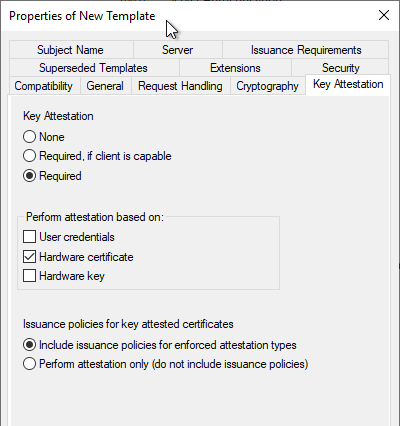
Afterwards, the attestation can be configured in the "Key Attestation" tab. The following options are available:
| Key Attestation | Description |
|---|---|
| None | The certificate request is not checked for attestation. The certificate is issued even if the attestation was not successful. |
| Required, if client is capable | The certificate request is checked for attestation only if the client supports it. The certificate is issued even if attestation was not successful. |
| Required | The certificate request is checked for attestation in any case and the request is denied if it was not successful. |
| Perform Attestation based on | Description |
|---|---|
| User Credentials | The user confirms that the private key is protected with a TPM, which of course is not really secure. |
| Hardware certificate | Corresponds to the EKCERT method. |
| Hardware Key | Corresponds to the EKPUB method. |
The attestation methods can also be combined with each other by multiple selection. For example, clients that do not have an endorsement certificate can be checked via EKPUB and all others via EKCERT. The "User credentials" method is of course not really secure and should therefore not be used.
Including certificate policies in issued certificates
In addition, it can be specified that the certification authority writes an issuance policy into an issued certificate to confirm the type of attestation.
| OID | Meaning |
|---|---|
| 1.3.6.1.4.1.311.21.32 | TPM Key Attestation: User Credentials: (Low Assurance) |
| 1.3.6.1.4.1.311.21.31 | TPM Key Attestation: Endorsement Certificate: (Medium Assurance) |
| 1.3.6.1.4.1.311.21.30 | TPM Key Attestation: Endorsement Key: (High Assurance) |
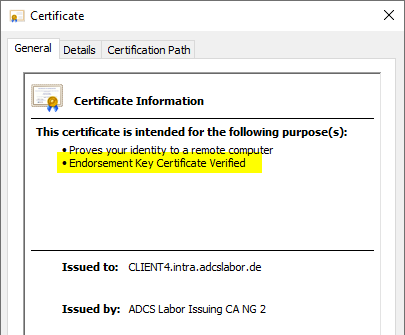
For example, from the combination of these options, it is possible to specify that while every enrollee is granted a certificate, only those whose private keys can be proven to be protected with a TPM (which can be proven via the issuance policy in the certificate) are also granted access to certain resources.
However, in order for these policies to be written to issued certificates, the certification authority certificate must also be configured accordingly. See the articles "Including the issuance policies for Trusted Platform (TPM) Key Attestation in a certification authority certificate " or "Including the wildcard issuance policy (All Issuance Policies) in a certification authority certificate ".
Troubleshooting
Failed TPM attestations can usually be identified on the certification authority by the events with IDs 22 and 53 .
External sources
- TPM Key Attestation (Microsoft)
- Setting up TPM protected certificates using a Microsoft Certificate Authority - Part 1: Microsoft Platform Crypto Provider (Microsoft)
- Setting up TPM protected certificates using a Microsoft Certificate Authority - Part 2: Virtual Smart Cards (Microsoft)
- Setting up TPM protected certificates using a Microsoft Certificate Authority - Part 3: Key Attestation (Microsoft)
- Install trusted TPM root certificates (Microsoft)