
Configuring a certificate template to use the Microsoft Platform Crypto Provider to enable private key protection by a Trusted Platform Module (TPM)
Since Windows 8, it has been possible to protect the private keys of certificates with a Trusted Platform Module (TPM), if one is present. This ensures that the key is truly non-exportable.
The process for setting up a certificate template that uses a Trusted Platform Module is described below.
The configuration of a certificate template to use the Microsoft Platform Crypto Provider described below is merely a default setting for the requesting client. The certification authority cannot guarantee that the enrollee is actually using a Trusted Platform Module. To achieve this level of security, TPM Key Attestation must be used in addition.
Private key must not be configured as exportable
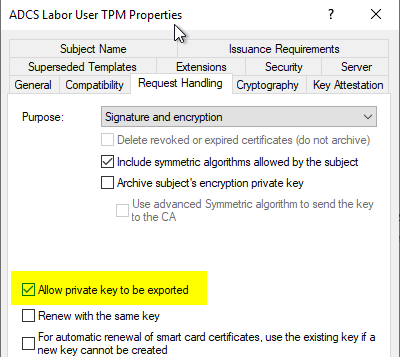
In the "Request Handling" tab, make sure that the "Allow private key to be exported" option is not enabled. The Microsoft Platform Crypto Provider does not support key export. If the option is enabled, certificate requests will fail (see the article "Requesting a Trusted Platform Module (TPM) protected certificate fails with error message "The requested operation is not supported. 0x80090029 (-2146893783 NTE_NOT_SUPPORTED)" ").
Configuring the Key Storage Provider
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
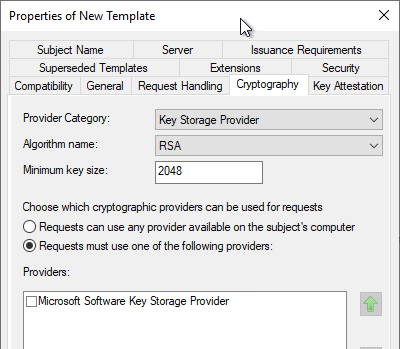
In most cases, when you open the "Cryptography" tab, you will find that the Microsoft Platform Crypto Provider is not available, despite correct configuration of the compatibility settings of the certificate template. This is due to the fact that only key storage providers that are available and usable on the current system are displayed.
If the computer running the Certificate Template Management Console does not have a Trusted Platform Module, it is consequently not possible to select the corresponding KSP.
There are several ways around this problem:
- Installation of the Remote Server Administration Tools (RSAT) on a computer (preferably a Privileged Admin Workstation (PAW)) with a Trusted Platform Module and configuration of the certificate template from there (see also the article "Installing Remote Server Administration Tools for Active Directory Certificate Services on Windows 10 version 1809 and later ").
- Editing the pKIDefaultCSPs attribute using certutil .
- Editing the pKIDefaultCSPs attribute using Windows PowerShell.
- Editing the pKIDefaultCSPs attribute using ADSI Editor.
Editing the pKIDefaultCSPs attribute using Windows PowerShell
The list of key storage providers is stored in the LDAP object of the certificate template in the attribute pKIDefaultCSPs. There it can be changed with Windows PowerShell (ActiveDirectory module).
The current value can be displayed with the following command:
Get-ADObject "CN=ADCSLaborUserTPM,CN=Certificate Templates,CN=Public Key Services,CN=Services,CN=Configuration,DC=intra,DC=adcslabor,DC=de" -Properties pKIDefaultCSPsIf the attribute is not displayed, this may be because it is empty by default, i.e. not defined.
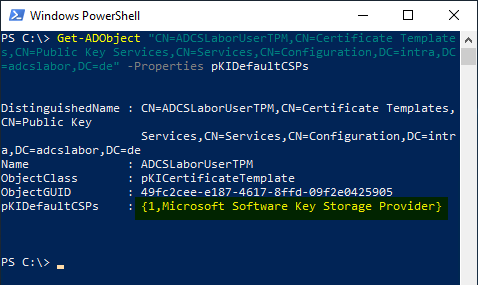
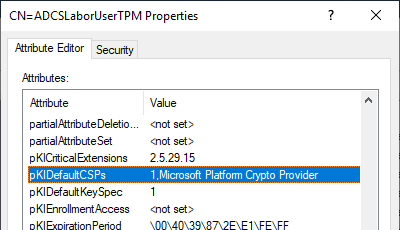
The following two commands can be used to change the content of the attribute. The "Microsoft Platform Crypto Provider" must be configured:
$CSPs=@("1,Microsoft Platform Crypto Provider")
Set-ADObject "CN=ADCSLaborUserTPM,CN=Certificate Templates,CN=Public Key Services,CN=Services,CN=Configuration,DC=intra,DC=adcslabor,DC=de" -Replace @{pKIDefaultCSPs=$CSPs}
To check, you can verify the change by querying the value again.
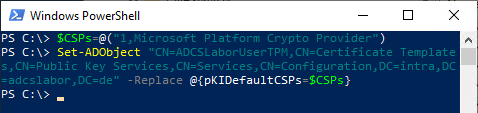
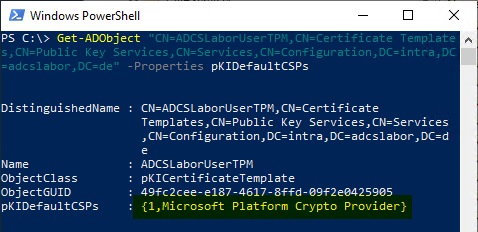
Please note that the pKIDefaultCSPs attribute can be overwritten by the certificate template management console. Therefore, after each change to the certificate template, it is necessary to check whether the attribute is set correctly again.
Editing the pKIDefaultCSPs attribute using ADSI Editor
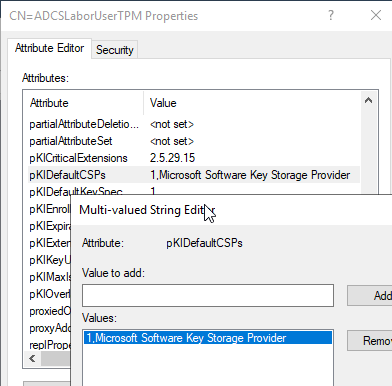
The change is also possible in the same way via ADSI Editor. The information can be found in the "Configuration" partition of the forest.
No certificates are requested if no TPM is present
On systems that do not have a Trusted Platform Module, no certificate is requested. If these systems are also to be served with certificates, a software key storage provider can also be stored as a second entry.
See the article "Requesting a certificate is not possible because the certificate template is not displayed. The error message is "Can not find a valid CSP in the local machine." ".