
Details of the event with ID 84 of the source Microsoft-Windows-CertificationAuthority
| Event Source: | Microsoft-Windows-CertificationAuthority |
| Event ID: | 84 (0x54) |
| Event log: | Application |
| Event type: | Error |
| Symbolic Name: | MSG_E_INVALID_KRA_CERT |
| Event text (English): | Active Directory Certificate Services will not use key recovery certificate %1 because it could not be verified for use as a Key Recovery Agent. %2 %3 |
| Event text (German): | Das Schlüsselwiederherstellungszertifikat %1 wird von den Active Directory-Zertifikatdiensten nicht verwendet, da es nicht für die Verwendung als Key Recovery Agent verifiziert werden konnte. %2 %3 |
Parameter
The parameters contained in the event text are filled with the following fields:
- %1: KRACertIndex (win:UnicodeString)
- %2: KRACertSubjectName (win:UnicodeString)
- %3: ErrorCode (win:UnicodeString)
Example events
Active Directory Certificate Services will not use key recovery certificate 0 because it could not be verified for use as a Key Recovery Agent. CN=Administrator, CN=Users, DC=intra, DC=adcslabor, DC=de The revocation function was unable to check revocation because the revocation server was offline. 0x80092013 (-2146885613 CRYPT_E_REVOCATION_OFFLINE)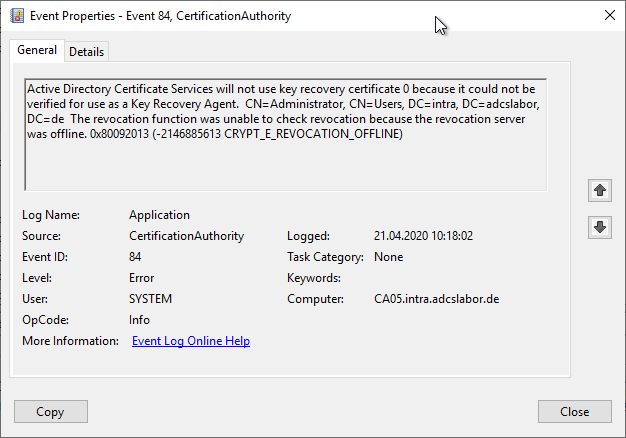
Description
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
Since the certification authority refuses to accept certificate requests for which private key archival is configured, and such certificates therefore cannot be requested, availability is affected.
Microsoft's rating
Microsoft evaluates this event in the Securing Public Key Infrastructure (PKI) Whitepaper with a severity score of "Low".
Related links:
- Overview of Windows events generated by the certification authority
- Overview of audit events generated by the certification authority
External sources
- Event ID 84 - AD CS Key Archival and Recovery (Microsoft)
- Securing Public Key Infrastructure (PKI) (Microsoft)