
Details of the event with ID 29 of the source Microsoft-Windows-Kerberos-Key-Distribution-Center
| Event Source: | Microsoft-Windows-Kerberos-Key-Distribution-Center |
| Event ID: | 29 (0x8000001D) |
| Event log: | System |
| Event type: | Warning |
| Event text (English): | The Key Distribution Center (KDC) cannot find a suitable certificate to use for smart card logons, or the KDC certificate could not be verified. Smart card logon may not function correctly if this problem is not resolved. To correct this problem, either verify the existing KDC certificate using certutil.exe or enroll for a new KDC certificate. |
| Event text (German): | Vom Schlüsselverteilungscenter (Key Distribution Center, KDC) kann kein passendes Zertifikat für Smartcard-Anmeldungen gefunden werden, oder das KDC-Zertifikat konnte nicht verifiziert werden. Das Anmelden per Smartcard funktioniert möglicherweise nicht ordnungsgemäß, so lange dieses Problem nicht behoben wurde. Verifizieren Sie zum Beheben dieses Problems entweder das vorhandene KDC-Zertifikat mithilfe von "certutil.exe", oder registrieren Sie sich für ein neues KDC-Zertifikat. |
Example events
The Key Distribution Center (KDC) cannot find a suitable certificate to use for smart card logons, or the KDC certificate could not be verified. Smart card logon may not function correctly if this problem is not resolved. To correct this problem, either verify the existing KDC certificate using certutil.exe or enroll for a new KDC certificate.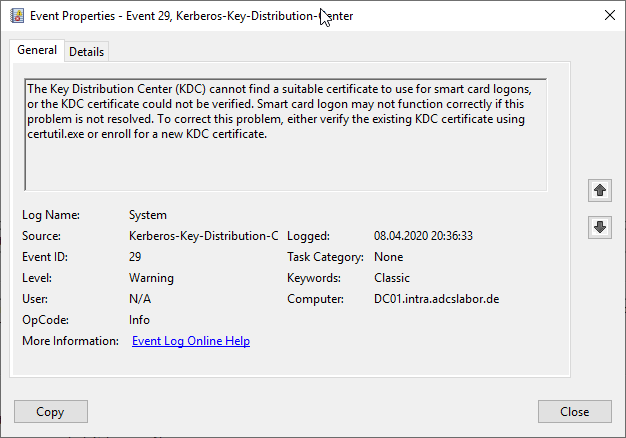
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Description
This message occurs when a smart card logon takes place, but the domain controller's certificate does not have any of the required Extended Key Usages (EKU) .
This is the case, for example, when a customized security-hardened certificate template that does not allow smart card logon is used for the domain controllers.
The event occurs together with event no. 19 .
See also the article "Smart card logon fails with error message "Signing in with a security device isn't supported for your account." ".
It can also occur when the domain controllers cannot check the validity of their own certificates, for example because the CRL distribution points are offline, or because trust in the root certification authority has not been established.
More information
- For more information on the default certificate templates for domain controllers, see the article "Overview of the different generations of domain controller certificates ".
- For more information on smart card logon, see the article "Domain Controller Certificate Templates and Smart Card Logon ".
- For the correct configuration of a certificate template for domain controllers, see the article "Configuring a Certificate Template for Domain Controllers ".
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
If security-hardened certificate templates for the domain controller certificates are used that do not allow smart card logon, this event can indicate an unauthorized logon attempt as well as the compromise of a certification authority. In this case, it would be rated as "critical" in terms of integrity.
For a description of the underlying problem, see the article "Attack vector on the Active Directory directory service via the smart card logon mechanism ".
Related links:
- Overview of Active Directory events relevant for PKI
- Overview of Windows events generated by the certification authority
- Overview of audit events generated by the certification authority
- Domain Controller Certificate Templates and Smart Card Logon
- Configuring a Certificate Template for Domain Controllers
- Attack vector on the Active Directory directory service via the smart card logon mechanism
External sources
- Event ID 29 — KDC Certificate Availability (Microsoft)