
Details of the event with ID 131 of the source Microsoft-Windows-CertificationAuthority
| Event Source: | Microsoft-Windows-CertificationAuthority |
| Event ID: | 131 (0x83) |
| Event log: | Application |
| Event type: | Warning |
| Event text (English): | An invalid OID has been detected in the EKUOIDsForPublishExpiredCertInCRL configuration setting. To resolve, run: "certutil -getreg ca\EKUOIDsForPublishExpiredCertInCRL" to identify the invalid OID and correct it. The default OIDs ("1.3.6.1.5.5.7.3.3" and "1.3.6.1.4.1.311.61.1.1") will be used. |
| Event text (German): | In der Konfigurationseinstellung "EKUOIDsForPublishExpiredCertInCRL" wurde eine ungültige OID festgestellt. Führen Sie zum Beheben den Befehl "certutil -getreg ca\EKUOIDsForPublishExpiredCertInCRL" aus, um die ungültige OID zu ermitteln und zu korrigieren. Die Standard-OIDs ("1.3.6.1.5.5.7.3.3" und "1.3.6.1.4.1.311.61.1.1") werden verwendet. |
Example events
An invalid OID has been detected in the EKUOIDsForPublishExpiredCertInCRL configuration setting. To resolve, run: "certutil -getreg ca\EKUOIDsForPublishExpiredCertInCRL" to identify the invalid OID and correct it. The default OIDs ("1.3.6.1.5.5.7.3.3" and "1.3.6.1.4.1.311.61.1.1") will be used.
Description
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Occurs when the EKUOIDsForPublishExpiredCertInCRL value in the registry of the certification authority contains an invalid entry. It is located under the following path:
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\CertSvc\Configuration\{Common-Name-der-Zertifizierungsstelle}This value is used to enter the object identifiers for certificates whose serial numbers must continue to be entered in issued certificate revocation lists even after their expiration date.
See also article "Handling of expired certificates when issuing certificate revocation lists ".
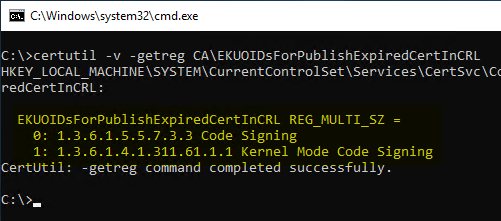
Only valid object identifiers may be entered. See also article "Frequently Used Extended Key Usages and Issuance Policies ".
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
As a rule, it is not necessary to change the EKUOIDsForPublishExpiredCertInCRL value. Since the certification authority falls back to the default values in case of misconfigurations, no threat to availability is expected.
Microsoft's rating
Microsoft evaluates this event in the Securing Public Key Infrastructure (PKI) Whitepaper with a severity score of "Low".
Related links:
- Overview of Windows events generated by the certification authority
- Overview of audit events generated by the certification authority
External sources
- Securing Public Key Infrastructure (PKI) (Microsoft)