
Configuring the Network Device Enrollment Service (NDES) for use with an alias
The following describes the steps required to configure the Network Device Enrollment Service (NDES) for use with an alias.
The term alias means that the service is not called with the name of the server on which it is installed, but with a generic name independent of this name. The use of an alias allows the service to be moved to another system at a later time without having to inform all participants of the new address.
The Network Device Enrollment Service (NDES) provides a way for devices that do not have an identifier in Active Directory (for example, network devices such as routers, switches, printers, thin clients, or smartphones and tablets) to request certificates from a certification authority. For a more detailed description, see the article "Network Device Enrollment Service (NDES) Basics ".
Implementation
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and can be used free of charge. Professional maintenance is also offered.
To configure the Network Device Enrollment Service (NDES) for use with an alias, the following steps are required:
- Create a DNS record for the alias
- Configuring a Service Principal Name (SPN) for the service account
- Optional: Request an SSL certificate customized to the alias
- Perform a functional test
- Communication of the alias to the participants
Details: Creating a DNS record for the alias
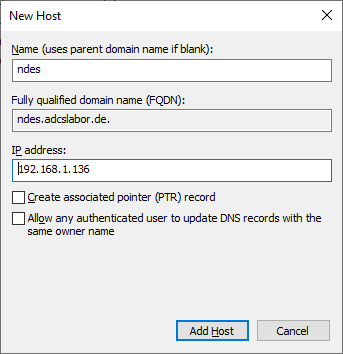
The alias must first be created in the Domain Name System (DNS).
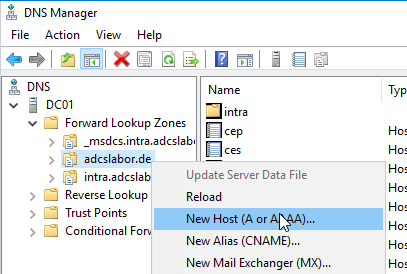
It is essential to use an A record. When using a CNAME, the Kerberos logon on the NDES administration web page will fail and you will be asked to log on again and again .
Details: Configuring a Service Principal Name (SPN) for the service account
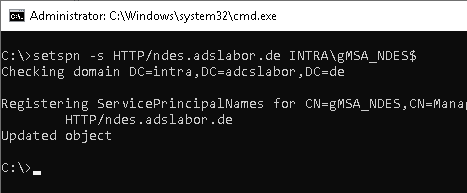
For Kerberos logon to the NDES administration website (mscep_admin), a service principal name must be set on the NDES server service account. This is done with the following command line command:
setspn -s HTTP/{Alias} {Domäne}\{Dienstkonto}If a Group Managed Service Account (gMSA) is used for NDES, a dollar sign must be included at the end when entering the account name so that the appropriate account can be found.
Details: Requesting an SSL certificate customized to the alias
This step is only required if the NDES administration web page has been configured with SSL, which is, however, strongly recommended (see article "Enabling Secure Sockets Layer (SSL) for the Network Device Enrollment Service (NDES) ").
The identity configured in the certificate (DNSName in the Subject Alternative Name field) must match the alias.
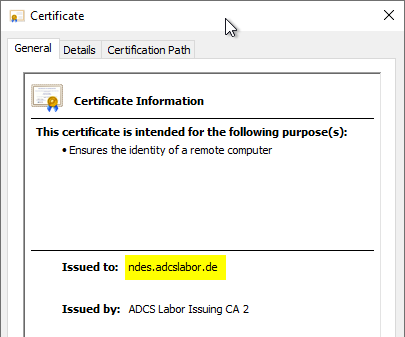
The generation of a corresponding certificate request is described in the article "Generating an RFC 2818 compliant certificate request for SSL certificates ".
Changing the SSL certificate does not require a restart of the web server and thus of the NDES service.
Details: Perform a functional test
After each change to an IT service, an extensive functional test should be performed. The procedure for NDES is described in the article "Performing a functional test for the Network Device Enrollment Service (NDES) ".
Details: communication of the alias to the participants
If the functional test was successful, the participants (for example, Mobile Device Management (MDM) administrators) must be notified of the change so that the new alias can be used.