
Configuring the certification authority to a static port (RPC endpoint)
In the default configuration, the certification authority's certificate request interface is configured to negotiate dynamic ports for the incoming RPC/DCOM connections (for more details, see the article "Firewall rules required for Active Directory Certificate Services ").
| Network protocol | Destination port | Protocol |
|---|---|---|
| TCP | 135 | RPC Endpoint Mapper |
| TCP | 49152-65535 | RPC dynamic ports |
This configuration is not feasible in every enterprise environment. Often there are restrictive firewall rules that do not allow the use of dynamic network ports.
In such a case, the certification authority must be configured to a static port.
Procedure
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
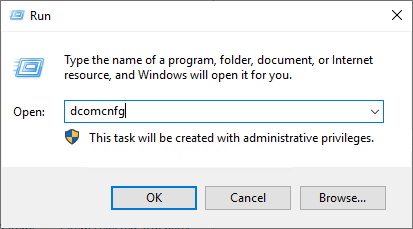
Configuration is done through the Component Services Management Console (dcomcnfg).
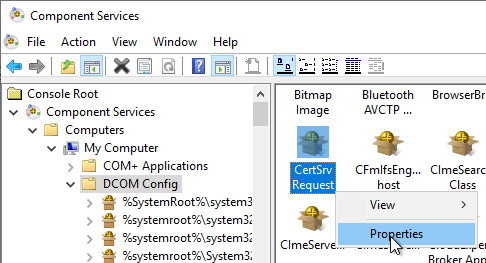
In the console, navigate to "Component Services" - "Computers" - "My Computer" - "DCOM Config". Look there for the entry "CertSrv Request". It is edited by right-clicking and then selecting "Properties".
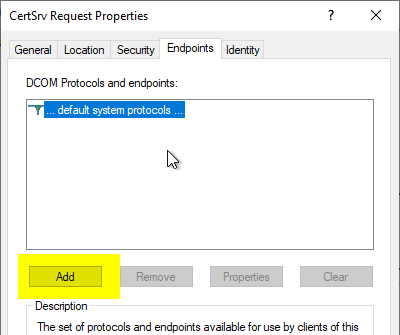
In the "Endpoints" tab, click on "Add..." to add a new endpoint.
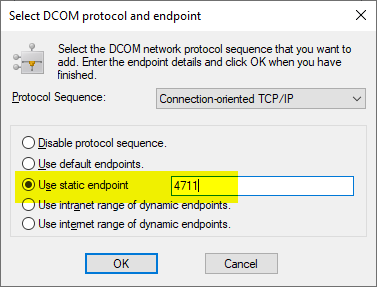
Here you select the option "Use static endpoint" and assign a network port.
For the settings to take effect, the certification authority service must be restarted.