
Subsequent archiving of private keys
For the encryption of email messages, companies typically use the Secure / Multipurpose Internet Message Extensions (S/MIME) standard and provide their users with appropriate certificates for this purpose.
An important aspect here is that the users' private keys should be secured centrally - in contrast to the signing certificates that are otherwise mostly used. Incoming messages are encrypted for a specific private key and can only be decrypted again by this key . Thus a backup of these keys must absolutely be available - this is also indispensable for synchronization to mobile devices . For this purpose, the Microsoft Active Directory Certificate Services offer the private key archival function.
But what if private key archival has not been set up and users have already requested corresponding certificates?
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Fortunately, it is possible to archive private keys - albeit with corresponding effort - even after the fact.
The prerequisites for this are:
- At least one valid Key Recovery Agent certificate has been set up on the corresponding certification authority.
- The private keys were exported from the user profiles and are available as a PKCS#12 (PFX) file including the password.
The import into the certification authority can then be done with the following command:
certutil [-p {Passwort}] -importKMS {Dateiname-PFX}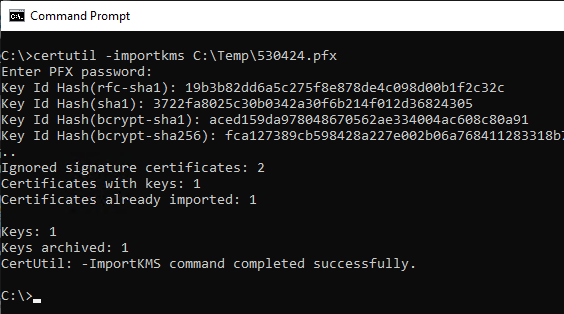
External sources
- certutil (Microsoft Corporation)