
Performing a functional test for the Certificate Enrollment Policy Web Service (CEP)
After installing a Certificate Enrollment Policy Web Service (CEP), or after more extensive maintenance work, an extensive functional test should be performed to ensure that all components are working as desired.
The Certificate Enrollment Web Services (Certificate Enrollment Policy Web Service, CEP, and Certificate Enrollment Web Service, CES) enable the automatic request and renewal of certificates from a certification authority via a web-based interface. This eliminates the need to contact the certification authority directly via Remote Procedure Call (RPC). For a more detailed description, see the article "Basics: Requesting certificates via Certificate Enrollment Web Services (CEP, CES) ".
Procedure
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
A functional test of the Certificate Enrollment Policy Web Service includes the following steps:
- Ensure that the Certificate Enrollment Policy Web Service starts
- Check the Event Viewer of the Certificate Enrollment Policy Web Service
- Verify the connection to the Certificate Enrollment Policy Web Service
- Create a certificate enrollment policy
- Query certificate templates via the Certificate Enrollment Policy Web Service
- Request a certificate with CEP
Details: Ensure that the Certificate Enrollment Policy Web Service starts
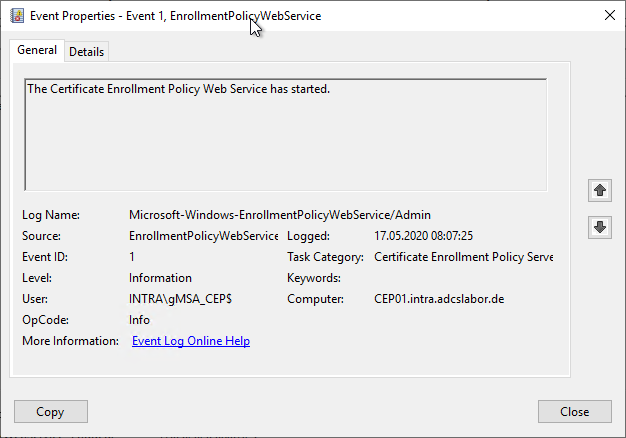
Since the Certificate Enrollment Policy Web Service is implemented as a module within the Internet Information Server (IIS) service, it is not possible to check the service startup via the management console for services (services.msc). Instead, a corresponding event with no. 1 is logged in the Event Viewer.
However, this is only generated the first time it is called by a requester, so the step "Verify the connection to the Certificate Enrollment Policy Web Service" described below must be performed first for this purpose.
Details: Check the Event Viewer of the Certificate Enrollment Policy Web Service
See also article "Overview of the Windows events generated by the Certificate Enrollment Policy Web Service (CEP) ".
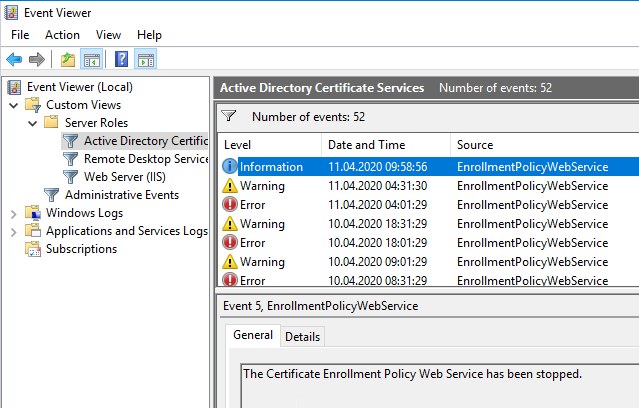
First, the Windows Event Viewer on the Certificate Enrollment Policy Web Service should be examined for any relevant events that might indicate an error. For this purpose, there is a predefined view in the Event Viewer under "Custom Views" - "Server Roles" - "Active Directory Certificate Services", which has already defined the required filters on the Event Viewer.
Details: Verify the connection to the Certificate Enrollment Policy Web Service
Kerberos authentication can be tested with the following command line command.
certutil -ping -kerberos -config "https://{Servername}/ADPolicyProvider_CEP_Kerberos/service.svc/CEP" CEP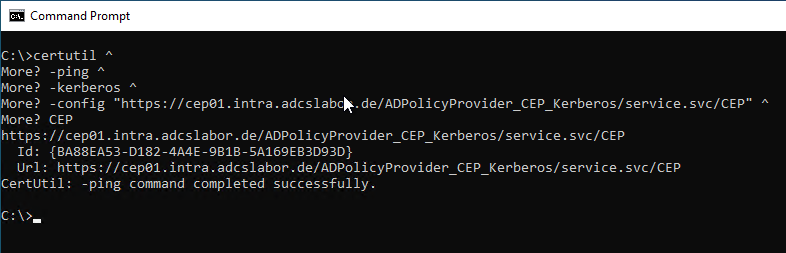
Authentication with username and password can be tested with the following command line command.
certutil -username {Domäne}\{Benutzername} -p {Passwort} -ping -config "https://{Servername}/ADPolicyProvider_CEP_UsernamePassword/service.svc/CEP" CEP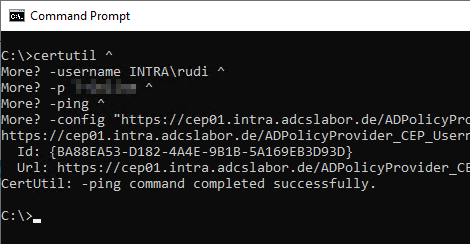
Authentication with a client certificate can be tested with the following command line command.
certutil -ClientCertificate {Thumbprint} -ping -config "https://{ServerName}/ADPolicyProvider_CEP_Certificate/service.svc/CEP" CEP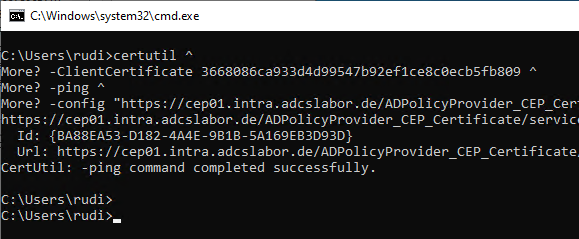
If you encounter problems with this step, the following articles may be helpful:
Details: Create a certificate enrollment policy
Now a certificate enrollment policy can be configured. The procedure is described in the article "Configuring a certificate enrollment policy (enrollment policy) for the Certificate Enrollment Web Services (CEP, CES)".
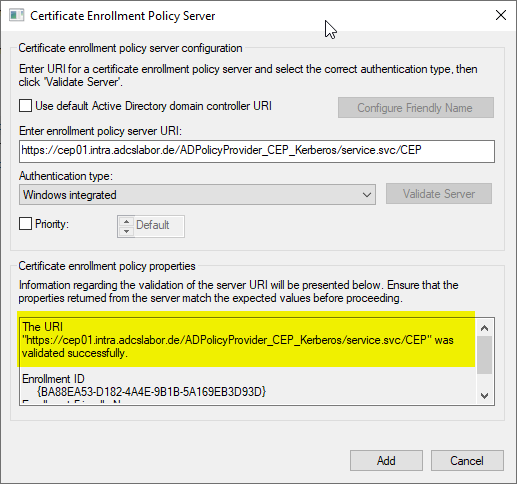
If you encounter problems with this step, the following articles may be helpful:
- The creation of a certificate enrollment policy for the Certificate Enrollment Policy Web Service (CEP) fails with the error message "This ID conflicts with an existing ID."
- The creation of a certificate enrollment policy for the Certificate Enrollment Policy Web Service (CEP) fails with error code "WS_E_INVALID_FORMAT"
- The creation of a certificate enrollment policy for the Certificate Enrollment Policy Web Service (CEP) fails with error code "WS_E_ENDPOINT_NOT_FOUND"
- Checking the certificate enrollment policy via the Certificate Enrollment Policy Web Service (CEP) fails with error code "WS_E_ENDPOINT_FAULT_RECEIVED"
- Requesting a certificate fails with the error message "You cannot request a certificate at this time because no certificate types are available."
Details: Query certificate templates via the Certificate Enrollment Policy Web Service
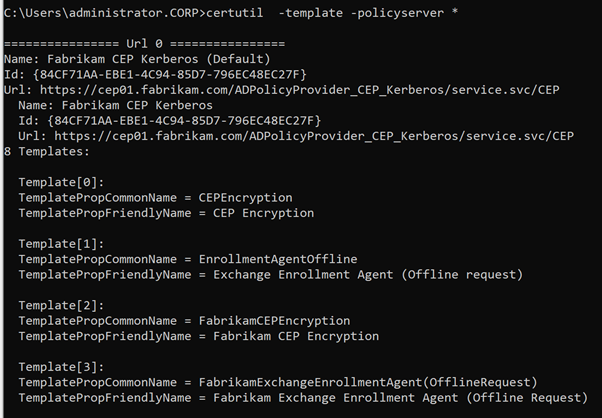
If a certificate enrollment policy has been configured for the current user as described previously, it can now be used to query the certificate templates via the Certificate Enrollment Policy Web Service.
certutil -template -policyserver *This is cached information that is generated only after a query has been made with the Microsoft Management Console (MMC).
Request a certificate with CEP
For this, a Certificate Enrollment Web Service (CES) must also first be installed in the network. A description of the procedure can be found in the article "Installing a Certificate Enrollment Web Service (CES)".
A certificate enrollment policy can then be set up and a certificate can be requested via the web services.
If you encounter problems with this step, the following articles may be helpful:
- Requesting a certificate via the Certificate Enrollment Web Services fails with error message "Error: The remote endpoint is unable to process the request due to being overloaded. 0x803d0012 (-2143485934 WS_E_ENDPOINT_TOO_BUSY)"
- Requesting a certificate via the Certificate Enrollment Web Services fails with error message "Error: A message containing a fault was received from the remote endpoint. 0x803d0013 (-2143485933 WS_E_ENDPOINT_FAULT_RECEIVED)"
- Requesting a certificate via the Certificate Enrollment Web Services fails with error message "Error: The operation timed out 0x80072ee2 (WinHttp: 12002 ERROR_WINHTTP_TIMEOUT)"
- Requesting a certificate via the Certificate Enrollment Policy Web Service (CEP) fails with error message "ERROR_WINHTTP_CONNECTION_ERROR"
- Requesting a certificate via the Certificate Enrollment Policy Web Service (CEP) fails with error message "The requested certificate template is not supported by this CA."
- Requesting a certificate via the Certificate Enrollment Policy Web Service (CEP) fails with error message "A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted."
- Requesting a certificate via the Certificate Enrollment Policy Web Service (CEP) fails with error message "Error: Access was denied by the remote endpoint. 0x803d0005 -2143485947 WS_E_ENDPOINT_ACCESS_DENIED"
- Requesting a certificate via the Certificate Enrollment Web Service (CES) fails with error code "ERROR_WINHTTP_INVALID_CA"
Other possible errors that can occur at this point and are caused by the Certificate Enrollment Web Service (CES) are described in the article "Performing a functional test for the Certificate Enrollment Web Service (CES)".
Follow-up tasks
If a certificate enrollment policy was set up manually for testing, it can now be removed again. The procedure for this is described in the article "Deleting a manually configured certificate enrollment policy (enrollment policy) ".