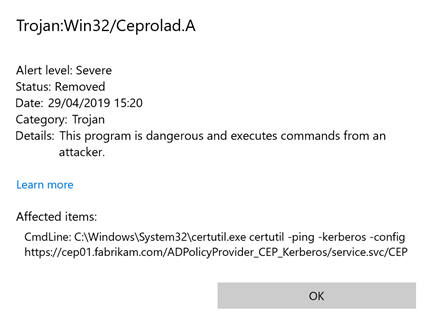
Windows Defender detects certutil as malware (Win32/Ceprolad.A)
Assume the following scenario:
- One performs a functional test for the Certificate Enrollment Policy Web Service (CEP) .
- For this, one uses a certutil command that uses Kerberos authentication, e.g.:
certutil -ping -kerberos -config "https://{Servername}/ADPolicyProvider_CEP_Kerberos/service.svc/CEP" CEP The certutil command is incorrectly detected by Windows Defender or Windows Defender Advanced Threat Protection as Win32/Ceprolad.A.