
Requesting a certificate fails with the error message "A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted."
Assume the following scenario:
- You try to request a certificate from an Active Directory integrated certification authority (enterprise CA).
- To do this, you use the Microsoft Management Console (MMC), either for the logged-on user (certmgr.msc) or for the computer (certlm.msc).
- However, the desired certificate template is not offered for selection, even though it has been correctly published on the certification authority.
- The logged-on user (or computer) also has the necessary permissions to request certificates from the certificate template in question (Enroll).
- In the list of available certificate templates within the MMC, you have all certificate templates displayed. The desired certificate template shows:
A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted.A general overview of how this works is provided by the articles "Basics: Manual and automatic certificate enrollment via Lightweight Directory Access Protocol (LDAP) and Remote Procedure Call / Distributed Common Object Model (RPC/DCOM) " and "Troubleshooting automatic certificate enrollment (autoenrollment) via RPC/DCOM ".
Causes
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
To narrow down the error further, a closer look at the description text helps.
Error "The requested certificate template is not supported by this CA."
The German variant of the description reads "Die angeforderte Zertifikatvorlage wird von dieser Zertifizierungsstelle (CA) nicht unterstützt.".
Of course, this only applies if the requested certificate template has actually been published on the certification authority.
The requested certificate template is not supported by this CA.
A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted.
This error indicates that trust in the issuing certification authority cannot be established.
In this case, the following should be checked:
- Is the root certification authority ("root CA") stored in the corresponding Trusted Root Certification Authorities store?
- Are all intermediate certification authorities (if any) stored in the Intermediate Certification Authorities store? (On domain clients, this store is automatically populated from the "AIA" object of the Public Key Services container in Active Directory. Accordingly, it should be checked whether the certificates are also stored there.)
Error "The permissions on this certification authority do not allow the current user to enroll for certificates" or "Cannot find object or property"
The permissions on this certification authority do not allow the current user to enroll for certificates.
A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted.
or
The German variant of the description is "Das Objekt oder die Eigenschaft wurde nicht gefunden".
Cannot find object or property.
A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted.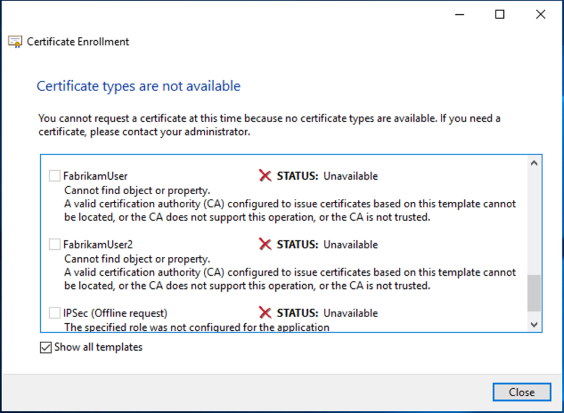
This error can occur, for example, if the logged-on user does not have the right to request certificates from the certification authority.
Root cause analysis
In addition to the permission within the certificate template, there is also a permission directly on the certification authority that is required to obtain certificates from it (Request Certificates).
The corresponding dialog can be accessed in the management console of the certification authority (certsrv.msc) by right-clicking the CA name, then "Properties", in the "Security" tab. By default, Authenticated Users have the right to request certificates.
In the present case, this right was also displayed accordingly in the "Security" tab of the certification authority. Nevertheless, no certificates could be requested from the certification authority. As a test, the certificate template was published on another certification authority, where it could be requested.
The permissions set in the "Security" tab are stored in two places:
- In the registry of the certification authority service under
HKLM:\SYSTEM\CurrentControlSet\Services\CertSvc\Configuration\{name-of-certification authority}\in the value "Security". - In the access control list (ACL) of the "Public Key Services" object in Active Directory, in the pKIEnrollmentService object belonging to the certification authority below CN=Enrollment Services. If the security permissions have been changed with the certification authority's management console, the certification authority's computer account updates the Active Directory object accordingly.
The value within the registry can be viewed either through the certification authority management console (certsrv.msc) or with the following command:
certutil -getreg CA\Security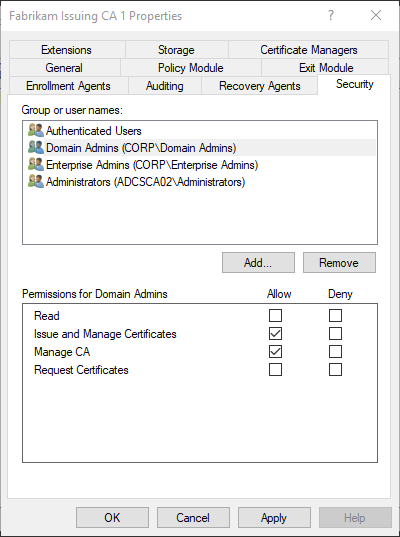
Example:
certutil -getreg CA\Security
 HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\CertSvc\Configuration\Fabrikam Issuing CA 1\Security:
 Security REG_BINARY =
     Allow Enroll        NT AUTHORITY\Authenticated Users
     Allow CA Administrator Certificate Manager  CORP\Domain Admins
     Allow CA Administrator Certificate Manager  CORP\Enterprise Admins
     Allow CA Administrator Certificate Manager  BUILTIN\Administrators
 CertUtil: -getreg command completed successfully.
The permissions on the Active Directory object can be displayed either via the ADSI Editor (adsiedit.msc) or via the command line.
The ADSI Editor is only suitable for this task to a limited extent, since AD CS-specific permissions are partly not resolved. The command line variant is better suited:
certutil [Options] -ds [CN]For example, with the -v option, the CN (Common Name) of the corresponding pKIEnrollmentService object, and the nTSecurityDescriptor attribute, the command looks like this:
certutil -ds -v "CN={CA-Common-Name},CN=Enrollment Services,CN=Public Key Services,CN=Services,CN=Configuration,{Forest-Root-Distinguished-Name}" nTSecurityDescriptor For the certification authority in question, this output came to light:
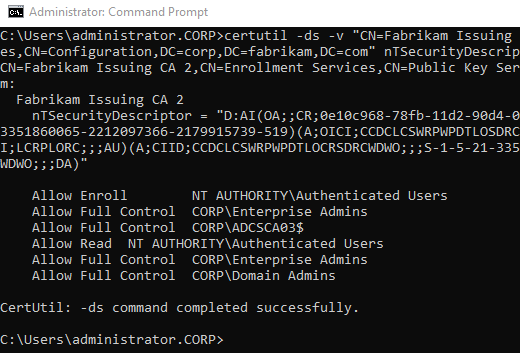
Allow Full Control  CORP\Enterprise Admins
Allow Full Control  CORP\ADCSCA03$
Allow Read  NT AUTHORITY\Authenticated Users
Allow Full Control  CORP\Enterprise Admins
Allow Full Control  CORP\Domain Admins
As you can see, the permission for the authenticated users to request certificates is missing here. Apparently, the registry and Active Directory are not in sync.
Cause
In the present case, the certification authority had been migrated to a new server . For this purpose, a backup of the certification authority was created and restored on a new server. To prevent certificates from being requested during the migration of the certification authority, the Authenticated Users principal was temporarily stripped of the right to request certificates. However, this was done after the registry of the certification authority had been backed up on the source server.
Thus, a registry was restored on the target server that apparently allows Authenticated Users to request certificates, but the pKIEnrollmentService object in Active Directory was not correctly updated again.
Solution
The solution was to remove the permission locally on the certification authority once more and enter it again. Afterwards, the pKIEnrollmentService object was in sync with the certification authority again:
External sources
- certutil (Microsoft)