
Installation of the default certificate templates fails with error message "This security ID may not be assigned as the owner of this object."
Assume the following scenario:
- For the first time, a certification authority (Enterprise Certification Authority) integrated into Active Directory is to be installed in the network.
- The rights to install the certification authority have been delegated to a separate security group or account for security reasons, so no logon as Enterprise Administrator is required. Put another way: The user used is not a member of the Enterprise Admins group in the Active Directory forest.
- Since this is the first certification authority in the network, no default certificate templates are installed in Active Directory yet. When opening the certificate template management console (certtmpl.msc), one is prompted to install them.
- The installation fails with the following error message:
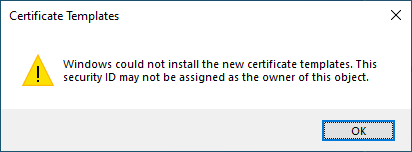
Windows could not install the new certificate templates. This security ID may not be assigned as the owner of this object.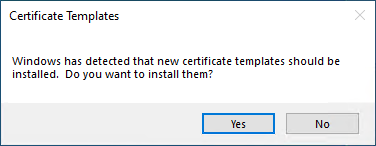
When trying to install the default certificate templates via certutil, a similar error message appears:
CertUtil: -InstallDefaultTemplates command FAILED: 0x8007051b (WIN32: 1307 ERROR_INVALID_OWNER)
CertUtil: This security ID may not be assigned as the owner of this object.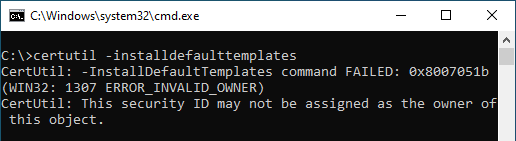
Cause
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
The installation of the default certificate templates must be performed once by an account with Enterprise Administrator privileges, since the "Restore Files and Directories" privilege on domain controllers is required to create the default certificate templates.
The creation of the default certificate templates can be done with the following command:
certutil -installdefaulttemplatesThis command can also be executed on a domain controller without installing additional software, as it is part of the standard Windows operating system delivery.
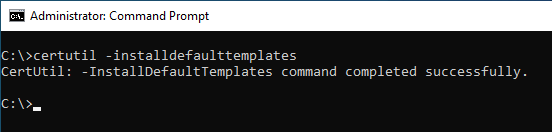
However, it must be ensured that the command is executed with elevated rights (Run as Administrator), otherwise the error message ERROR_DS_INSUFF_ACCESS_RIGHTS is reported.
CertUtil: -InstallDefaultTemplates command FAILED: 0x80072098 (WIN32: 8344 ERROR_DS_INSUFF_ACCESS_RIGHTS)
CertUtil: Insufficient access rights to perform the operation.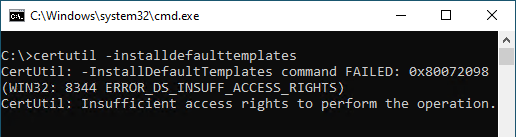
External sources
- Delegated Installation for an Enterprise Certification Authority (Microsoft Corporation)
- Error loading default templates on new Enterprise Root CA (Microsoft TechNet Forums)