
Details of the event with ID 4887 of the source Microsoft-Windows-Security-Auditing
| Event Source: | Microsoft-Windows-Security-Auditing |
| Event ID: | 4887 (0x1317) |
| Event log: | Security |
| Event type: | Information |
| Event text (English): | Certificate Services approved a certificate request and issued a certificate. Request ID: %1 Requester: %2 Attributes: %3 Disposition: %4 SKI: %5 Subject: %6 |
| Event text (German): | Die Zertifikatdienste haben eine Zertifikatanforderung genehmigt und ein Zertifikat ausgestellt. Anforderungs-ID: %1 Antragsteller: %2 Attribute: %3 Disposition: %4 SKI: %5 Betreff: %6 |
Parameter
The parameters contained in the event text are filled with the following fields:
- %1: RequestId (win:UnicodeString)
- %2: Requester (win:UnicodeString)
- %3: Attributes (win:UnicodeString)
- %4: Disposition (win:UnicodeString)
- %5: SubjectKeyIdentifier (win:UnicodeString)
- %6: Subject (win:UnicodeString)
In contrast to operational events, which are often understood under the term "monitoring", auditing for the certification authority is the configuration of logging of security-relevant events.
Example events
 Certificate Services approved a certificate request and issued a certificate.

 Request ID:	130
 Requester:	INTRA\TCA2008$
 Attributes:
 cdc:DC01.intra.adcslabor.de
 rmd:TCA2008.intra.adcslabor.de

 ccm:TCA2008.intra.adcslabor.de
 Disposition:	3
 SKI:		71 98 9a e4 99 fd f0 fd 72 6a 78 ac 38 9d 58 74 b0 1b 2c 86
 Subject:
Certificate Services approved a certificate request and issued a certificate.
Request ID: 110910
Requester: INTRA\rudi
Attributes:
CertificateTemplate:ADCSLaborSmartcardLogon
ccm:NDES01.intra.adcslabor.de
Disposition: 3
SKI: 16 2f 74 e1 8e 6c bd 18 5c e3 ad 2d 10 22 ff 4d 7d 88 ba be
Subject: CN=Administrator, CN=Users, DC=intra, DC=adcslabor, DC=de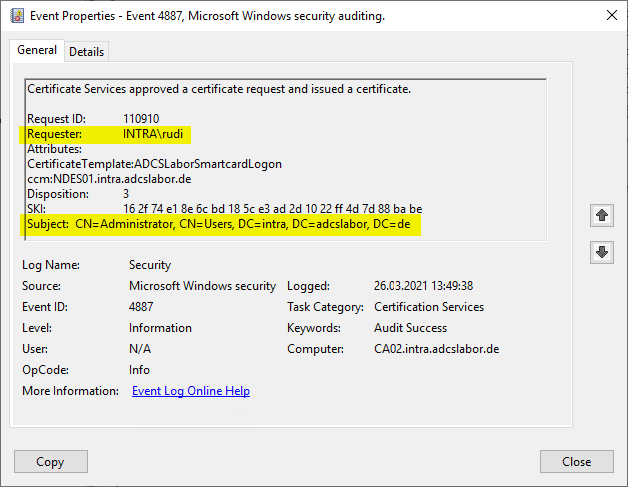
Description
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Triggered when a certificate is issued by the certification authority.
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
The event may contain indications of an unauthorized certificate request. An alert can be useful if, for example, certificates for administrative identities are issued via the Enroll on Behalf of (EOBO) process.
In addition, a vulnerability was disclosed under the name CertiGhost that exploits the "cdc" and "rmd" attributes contained in the request attributes to compromise Active Directory. Checking the "cdc" attribute against a list of known domain controllers—along with setting up alerts—can be very effective in detecting an attack.
Also alerting in case of issuing certificates with empty commonName can be useful, this can happen in connection with a Mobile Device Management (MDM) system, e.g. if a device is not assigned to any user.
Microsoft's rating
Microsoft evaluates this event in the Securing Public Key Infrastructure (PKI) Whitepaper with a severity rating of "Medium".
The reasoning behind this is:
Issuance of certificates that contain usages that allow the owner to perform privileged operations (Enrollment Agent, Code Signing etc.) or certificates issued to VIP users should be monitored.
External sources
- Securing Public Key Infrastructure (PKI) (Microsoft)
- Certighost Exploit Lets Low-Privileged Active Directory Users Impersonate a Domain Controller (The Hacker News)
- CVE-2026-54121.md (Muhammad Ali)