
Configuring a Group Policy (GPO) for Remote Desktop (RDP) Certificates
After configuring a certificate template for the distribution of Remote Desktop certificates (see the article "Configuring a Certificate Template for Remote Desktop (RDP) Certificates "), a Group Policy is still required that instructs the participating computers to also use the certificates originating from the template.
Implementation
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
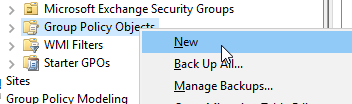
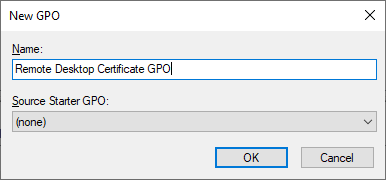
First, a new Group Policy Object (GPO) is created and edited via the Group Policy Management Console (gpmc.msc).
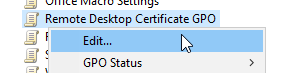
Navigate to "Computer Configuration" - "Windows Components" - "Remote Desktop Services" - "Remote Desktop Session Host" - "Security". There you select the option "Server authentication certificate template" and edit it.
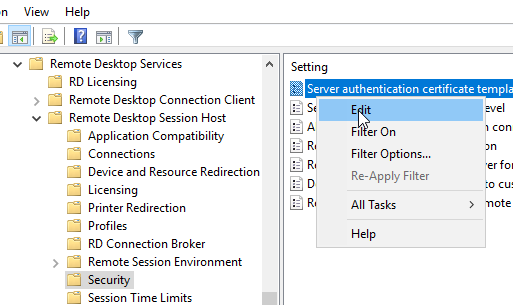
Set the setting to "Enabled" and specify the object name (the name without spaces) of the certificate template.
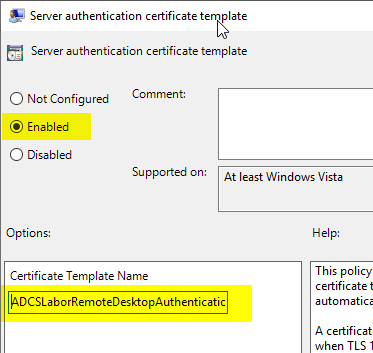
The Group Policy can now be distributed to the participating machines.
Client-side behavior
To better understand the client-side behavior, it helps to have a look at the description within the configuration dialog:
If no certificate can be found that was created with the specified certificate template, the RD Session Host server will issue a certificate enrollment request and will use the current certificate until the request is completed. If more than one certificate is found that was created with the specified certificate template, the certificate that will expire latest and that matches the current name of the RD Session Host server will be selected.
This means that the client will behave as follows:
- If a (valid) certificate based on the configured certificate template is already present (for example, because it was distributed in advance via autoenrollment), it is used and bound on the Remote Desktop Session Host.
- If no certificate is present, the Remote Desktop Session Host requests one, even if the certificate template is not configured for autoenrollment (indicated by the event with ID 1063 of the source Terminalservices-RemoteConnectionManager ).
- If only a certificate is present that will expire in less than two days, a new one is requested by the Remote Desktop Session Host (also indicated by the event with ID 1063 of the source Terminalservices-RemoteConnectionManager ).
Thus, the configuration will work even if the certificate template for Remote Desktop certificates has not been configured for autoenrollment. However, because it is easier to manage, using autoenrollment is still recommended.
For example, vulnerability scanners such as Qualys will report a finding if Remote Desktop certificates are not renewed until two days before expiration.
Next steps
How to verify that the clients are actually using the Remote Desktop certificates is described in the article "Identifying the active Remote Desktop (RDP) certificate ".
External sources
- Configuring Remote Desktop certificates (Microsoft, archive.org)