
Certificate request fails with error message "Error Parsing Request The request subject name is invalid or too long. 0x80094001 (-2146877439 CERTSRV_E_BAD_REQUESTSUBJECT)".
Assume the following scenario
- A certificate request is sent to a certification authority.
- The certificate request fails with the following error message:
Error Parsing Request The request subject name is invalid or too long. 0x80094001 (-2146877439 CERTSRV_E_BAD_REQUESTSUBJECT)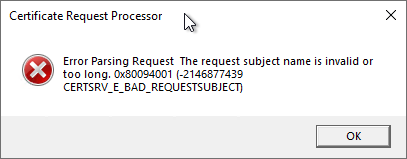
The certification authority logs event no. 22 :
Active Directory Certificate Services could not process request 166086 due to an error: The request subject name is invalid or too long. 0x80094001 (-2146877439 CERTSRV_E_BAD_REQUESTSUBJECT). The request was for CN=aaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaaa. Additional information: Error Parsing Request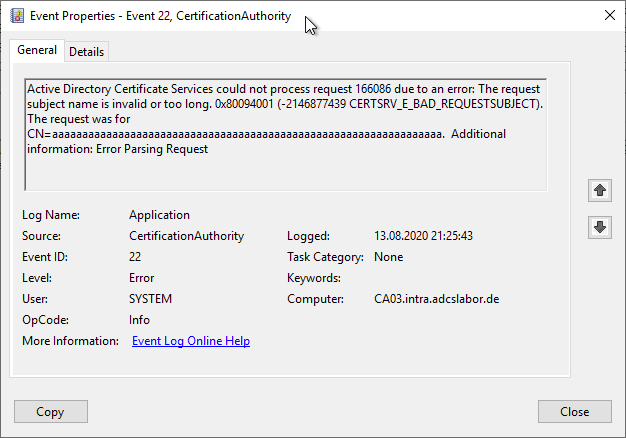
Possible causes:
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
- The Subject (Subject Distinguished Name) field in the certificate request is identical to that of the certification authority.
- A Relative Distinguished Name (RDN) requested in the Subject (Subject Distinguished Name) field is longer than permitted
- A certificate request does not contain any subject information (empty Subject Distinguished Name and no Subject Alternative Name)
Details: The Subject field in the certificate request is identical to that of the certification authority
The certification authority compares its own subject name (Subject) with that of the enrollee and rejects certificate requests that request the name of the certification authority.
Details: A Relative Distinguished Name (RDN) requested in the Subject (Subject Distinguished Name) field is longer than permitted
The error can also occur if one of the requested Relative Distinguished Names (RDN) in the Subject field is too long. You can display the length of the RDNs with the following command line command:
certutil -v -dump {Zertifikatanforderung}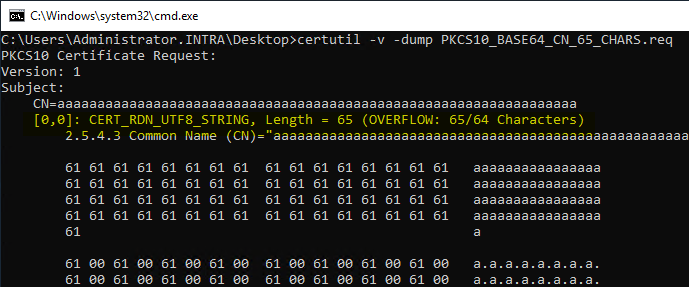
Microsoft Active Directory Certificate Services limits the length of requested RDNs on the certification authority (in the case of the CN to 64 characters. See also article "Allowed Relative Distinguished Names (RDNs) in the Subject of Issued Certificates "). However, this behavior can be prevented with the following command line command:
certutil -setreg ca\EnforceX500NameLengths 0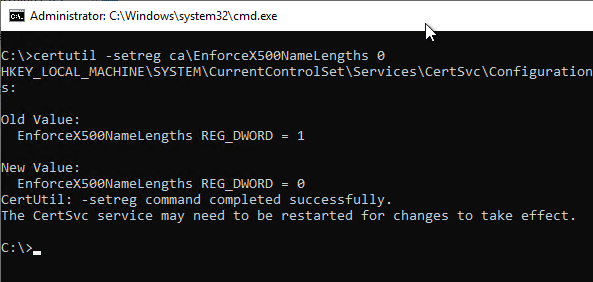
Afterwards, the certification authority service must be restarted to apply the changes.
Provided that the Common PKI standard is used, it must be noted that this limits the length of Relative Distinguished Names (RDNs) to 64 characters.
Whether the restriction is currently set can be checked with the following command line command:
certutil -getreg ca\EnforceX500NameLengths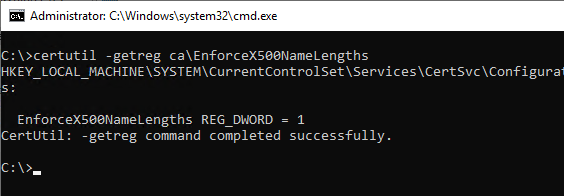
This restriction does not apply to the Subject Alternative Name (SAN). Depending on the certificate type (e.g. for SSL) it may be useful or even necessary (see RFC 2818 ) to prefer the Subject Alternative Name over the Common Name.
Details: A certificate request does not contain any subject information (empty Subject Distinguished Name and no Subject Alternative Name)
If a certificate request does not contain any identity information, this error message also occurs.
This phenomenon can also occur in connection with Mobile Device Management (MDM) systems if no valid user is assigned to a managed device. Specifically, I have observed this behavior with Baramundi Enterprise Mobility Management .
This can be determined by exporting the certificate request from the certification authority database and then displaying the ASN.1 encoded raw data with the following command.
certutil -asn {Dateiname}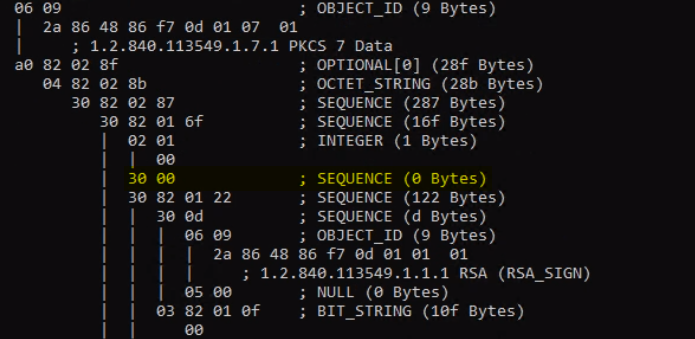
A certificate request does not contain any Subject Distinguished Name (DN), the sequence is empty.
For comparison, a certificate request that contains an empty commonName.
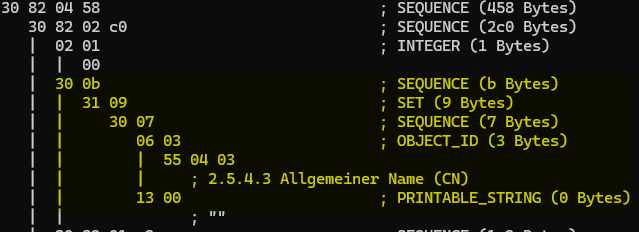
A certificate request contains a Subject Distinguished Name (DN) with an empty commonName, the sequence is not empty.
Related links:
- Generating a RFC 2818 compliant certificate request for SSL certificates
- Description of the necessary configuration settings for the "Common PKI" certificate profile
- Allowed Relative Distinguished Names (RDNs) in the Subject of Issued Certificates
External sources
- Request for Certificate Is Denied and a "The Request Subject Name Is Invalid or Too Long" Error Message Occurs (Microsoft)
- RFC 2818 - HTTP Over TLS (Internet Engineering Task Force)