
Details of the event with ID 51 of the source Microsoft-Windows-CertificationAuthority
| Event Source: | Microsoft-Windows-CertificationAuthority |
| Event ID: | 51 (0x33) |
| Event log: | Application |
| Event type: | Error |
| Symbolic Name: | MSG_E_CA_CERT_REVOKED |
| Event text (English): | A certificate in the chain for CA certificate %3 for %1 has been revoked. %2. |
| Event text (German): | Ein Zertifikat in der Zertifizierungsstellen-Zertifikatkette %3 für %1 wurde gesperrt. %2. |
Parameter
The parameters contained in the event text are filled with the following fields:
- %1: CACommonName (win:UnicodeString)
- %2: ErrorCode (win:UnicodeString)
- %3: CACertIdentifier (win:UnicodeString)
Example events
A certificate in the chain for CA certificate 0 for ADCS Labor Issuing CA 3 has been revoked. The certificate is revoked. 0x80092010 (-2146885616 CRYPT_E_REVOKED).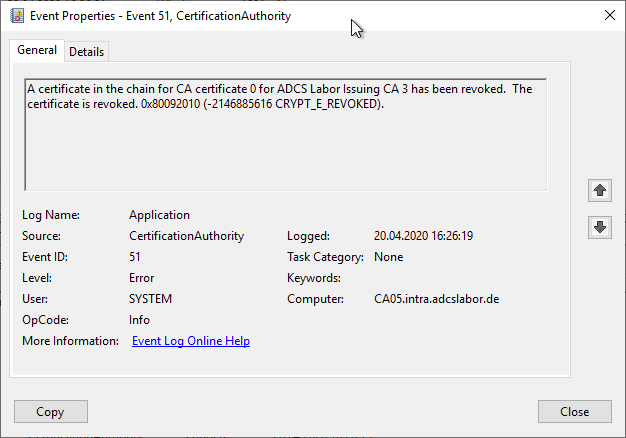
Description
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
This event occurs when the certification authority service is started if one of the previous certification authority certificates has been revoked by the parent certification authority. See also the article "What impact does the revocation of a certification authority certificate have on the certification authority? ". If the revocation concerns the current certification authority certificate, the event with ID 100 is logged instead.
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
The certification authority service will start normally, so no impact on availability is expected.
Microsoft's rating
Microsoft evaluates this event in the Securing Public Key Infrastructure (PKI) Whitepaper with a severity score of "Low".
Related links:
- Overview of Windows events generated by the certification authority
- Overview of audit events generated by the Certification Authority