
Details of the event with ID 32 of the source Microsoft-Windows-Kerberos-Key-Distribution-Center
| Event Source: | Microsoft-Windows-Kerberos-Key-Distribution-Center |
| Event ID: | 32 (0x80000020) |
| Event log: | System |
| Event type: | Warning |
| Event text (English): | The Key Distribution Center (KDC) uses a certificate without KDC Extended Key Usage (EKU) which can result in authentication failures for device certificate logon and smart card logon from non-domain-joined devices. Enrollment of a KDC certificate with KDC EKU (Kerberos Authentication template) is required to remove this warning. |
| Event text (German): | Vom Schlüsselverteilungscenter (Key Distribution Center, KDC) wird ein Zertifikat ohne erweiterte Schlüsselverwendung (Extended Key Usage, EKU) für das KDC verwendet. Dies kann bei Gerätezertifikatanmeldungen und Smartcardanmeldungen von Geräten ohne Domänenzugehörigkeit zu Authentifizierungsfehlern führen. Die Registrierung eines KDC-Zertifikats mit KDC-EKU (Kerberos-Authentifizierungsvorlage) ist erforderlich, um diese Warnung zu beseitigen. |
Example events
The Key Distribution Center (KDC) uses a certificate without KDC Extended Key Usage (EKU) which can result in authentication failures for device certificate logon and smart card logon from non-domain-joined devices. Enrollment of a KDC certificate with KDC EKU (Kerberos Authentication template) is required to remove this warning.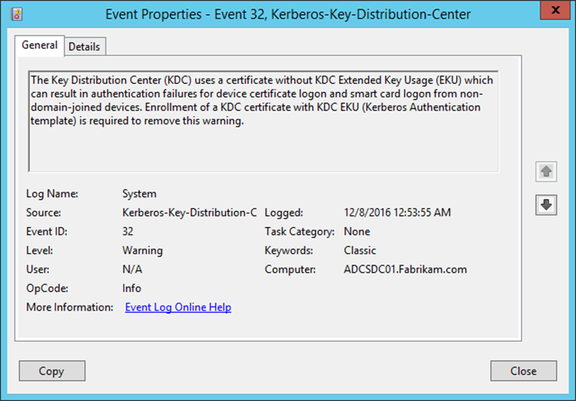
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Description
This message occurs when a smart card logon was processed and the domain controller certificate does not contain an Extended Key Usage (EKU) for "Kerberos Authentication".
This is the case, for example, if the domain controller uses a certificate based on the default Domain Controller certificate template. This does not contain the extended key usage for "Kerberos Authentication". The same applies to the deprecated Domain Controller Authentication certificate template.
The "Domain Controller" certificate template is - if it is offered by a certification authority - automatically requested by the domain controllers. It is therefore often used unknowingly.
More information
- For more information regarding the default certificate templates for domain controllers, see the article "Overview of the different generations of domain controller certificates ".
- For more information regarding smart card logon, see the article "Domain Controller Certificate Templates and Smart Card Logon ".
- For the correct configuration of a certificate template for domain controllers, see the article "Configuring a Certificate Template for Domain Controllers ".
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
Since it is very likely that the "Domain Controller" certificate template will be used inadvertently for the reasons described previously, it should also be checked whether it is intended that users log on via smart card at all.
If this is not the case, this event could be an indication of an attack on Active Directory via the certification authority, and in this case would be considered critical for the integrity of the network.
For a description of the underlying problem, see the article "Attack vector on Active Directory directory service via smart card logon mechanism ".
External sources
- What's New in Kerberos Authentication (Microsoft)
- You cannot use a smart card certificate to log on to a domain from a Windows Vista-based client computer (Microsoft)
- Enabling Strict KDC Validation in Windows Kerberos (Microsoft)
- Configure Windows Logon With An Electronic Identity Card (EID) (Thomas Vuylsteke)