
Details of the event with ID 200 of the source Microsoft-Windows-Kerberos-Key-Distribution-Center
| Event Source: | Microsoft-Windows-Kerberos-Key-Distribution-Center |
| Event ID: | 200 (0xC8) |
| Event log: | Microsoft-Windows-Kerberos-Key-Distribution-Center/Operational |
| Event type: | Warning |
| Event text (English): | The Key Distribution Center (KDC) cannot find a suitable certificate to use. This KDC is not enabled for smart card or certificate authentication. |
| Event text (German): | Das Schlüsselverteilungscenter (KDC) kann kein geeignetes Zertifikat finden. Dieses KDC ist nicht für die Smartcard- oder Zertifikatauthentifizierung aktiviert. |
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Example events
The Key Distribution Center (KDC) cannot find a suitable certificate to use. This KDC is not enabled for smart card or certificate authentication.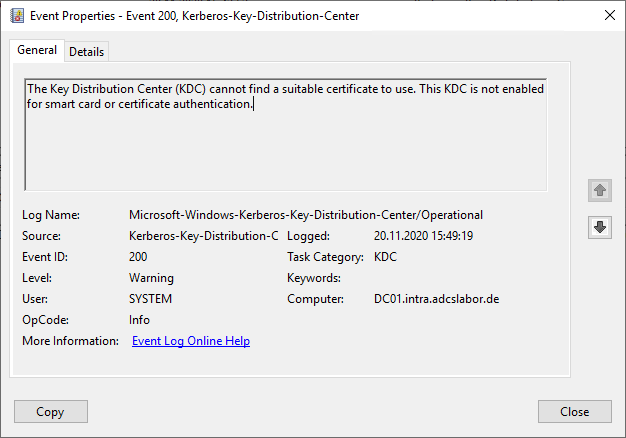
Description
Occurs when the domain controller does not have a certificate that can be used to provide smart card logon .
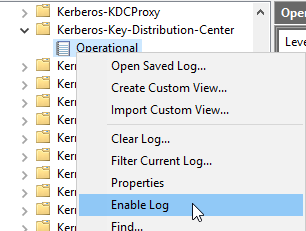
This event is generated only if the corresponding event log has been explicitly enabled.
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
If smart card logon is to be used, the availability of this service is limited and the event must be rated as critical.
External sources
- What's New in Kerberos Authentication (Microsoft)