
Details of the event with ID 34 of the source Microsoft-Windows-CertificationAuthority
| Event Source: | Microsoft-Windows-CertificationAuthority |
| Event ID: | 34 (0x22) |
| Event log: | Application |
| Event type: | Error |
| Event text (English): | Active Directory Certificate Services did not start: Could not initialize RPC for %1. %2. |
| Event text (German): | Die Active Directory-Zertifikatdienste wurden nicht gestartet: RPC für %1 konnte nicht initialisiert werden. %2. |
Parameter
The parameters contained in the event text are filled with the following fields:
- %1: CACommonName (win:UnicodeString)
- %2: ErrorCode (win:UnicodeString)
Example events
Active Directory Certificate Services did not start: Could not initialize RPC for ADCS Labor Issuing CA 1. The endpoint is a duplicate. 0x6cc (WIN32: 1740 RPC_S_DUPLICATE_ENDPOINT).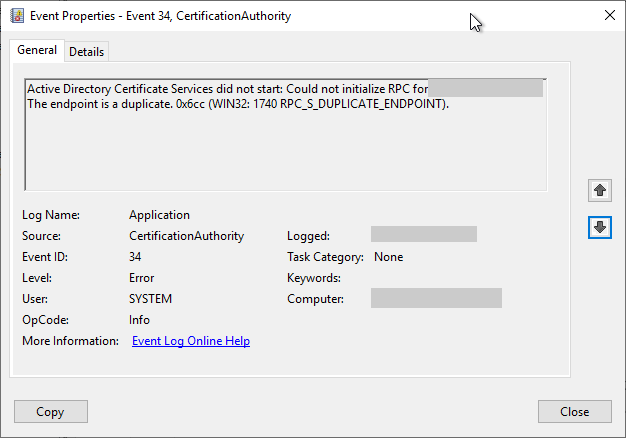
Description
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
The error indicates that the certification authority can no longer bind the RPC port because it has not yet been released again. A typical suspect here is the key storage provider of the hardware security module (HSM).
Especially with Gemalto / SafeNet HSMs there is a known bug in some key storage providers that can trigger this behavior.
When restarting the certification authority service, there must be sufficient time (approx. 1 minute) between termination and start of the service.
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
The availability of the certification authority service is no longer given if this event occurs. Therefore, an alert should definitely take place.
Microsoft's rating
Microsoft evaluates this event in the Securing Public Key Infrastructure (PKI) Whitepaper with a severity score of "Low".
Related links:
- Overview of Windows events generated by the certification authority
- Overview of audit events generated by the certification authority
External sources
- Securing Public Key Infrastructure (PKI) (Microsoft)