
Details of the event with ID 128 of the source Microsoft-Windows-CertificationAuthority
| Event Source: | Microsoft-Windows-CertificationAuthority |
| Event ID: | 128 (0x80) |
| Event log: | Application |
| Event type: | Warning |
| Symbolic Name: | MSG_W_REQUEST_CONTAINS_AKI |
| Event text (English): | An Authority Key Identifier was passed as part of the certificate request %1. This feature has not been enabled. To enable specifying a CA key for certificate signing, run: "certutil -setreg ca\UseDefinedCACertInRequest 1" and then restart the service. |
| Event text (German): | Im Rahmen der Zertifikatanforderung %1 wurde eine Stellenschlüsselkennung weitergegeben. Dieses Feature ist nicht aktiviert. Führen Sie zum Angeben eines Zertifizierungsstellenschlüssels für die Zertifikatsignierung den Befehl "certutil -setreg ca\UseDefinedCACertInRequest 1" aus, und starten Sie den Dienst neu. |
Parameter
The parameters contained in the event text are filled with the following fields:
- %1: RequestId (win:UnicodeString)
Example events
An Authority Key Identifier was passed as part of the certificate request 166131. This feature has not been enabled. To enable specifying a CA key for certificate signing, run: "certutil -setreg ca\UseDefinedCACertInRequest 1" and then restart the service.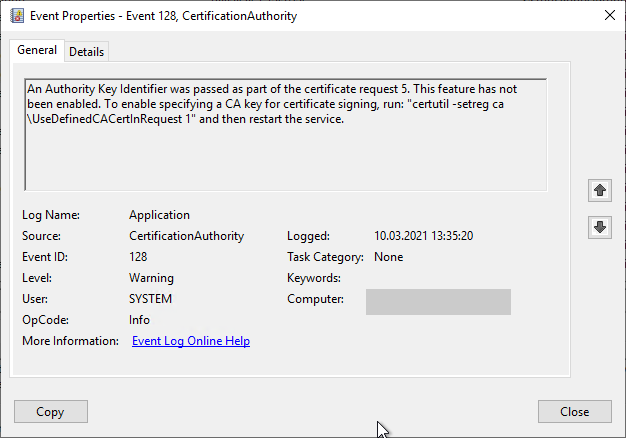
Description
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
This event occurs when a certificate request includes an Authority Key Identifier (AKI) extension, but the certification authority does not allow it.
The AKI extension is used, for example, by the Online Responder (OCSP) to have the signing certificate for the OCSP responses signed with a specific certification authority key (if the certification authority has multiple CA certificates - the OCSP response signature must always be made with the same key as the certificate whose revocation status the Online Responder checks.
See also article "Allow requesting a specific signature key on a certification authority ".
See also Event no. 35 of the Online Responder.
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
If the lifecycle process for certification authorities provides for renewal with a new key pair, an alert should be issued because the availability of the Online Responder's revocation configuration is affected and errors or undesirable behavior may occur during certificate revocation checks.
Microsoft's rating
Microsoft evaluates this event in the Securing Public Key Infrastructure (PKI) Whitepaper with a severity score of "Low".
Related links:
- Overview of Windows events generated by the certification authority
- Overview of audit events generated by the certification authority