What does the "Enable Certificate Privacy" option mean when exporting certificates?
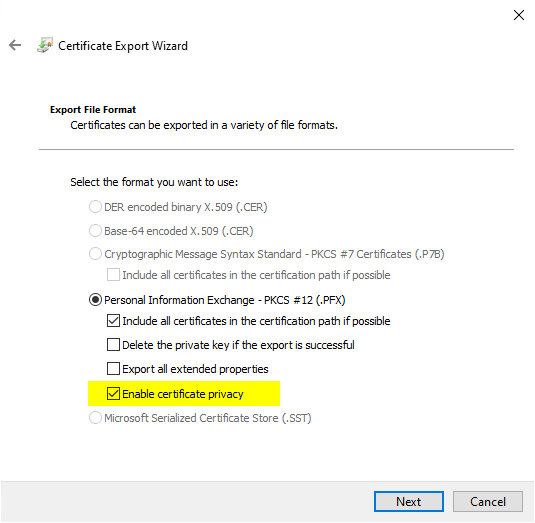
With Windows Server 2016 and Windows 10, a new "Enable Certificate Privacy" option has been implemented for exporting certificates with a private key via the Microsoft Management Console (MMC).
When exporting certificates with a private key, the certificate is exported to a PKCS#12 (.PFX) file.
How it works
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
In previous Windows versions, the entire contents of the PKCS#12 file were encrypted. Without the password it was not possible to view the file, not even to read meta information.
If the option is deactivated, only the private key in the PKCS#12 file is encrypted, all other contents are thus readable without password.
On Windows Server 2016 and Windows 10 versions at that time, the option was by default deactivated.
On Windows Server 2019 and current Windows 10 versions, it is activated by default again and thus reproduces the same behavior as previous Windows versions.
Functional test
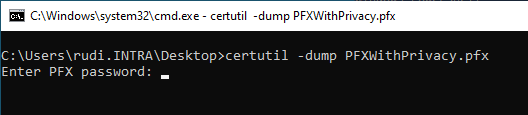
For comparison, two PKCS#12 files with the different settings, each examined with the following command line command:
certutil -dump {Datei}Option enabled
If the "Enable Certificate Privacy" option is enabled, a password is absolutely required to view the file
Option not activated
If the "Enable Certificate Privacy" option is not enabled, the public information can be viewed even without a password.
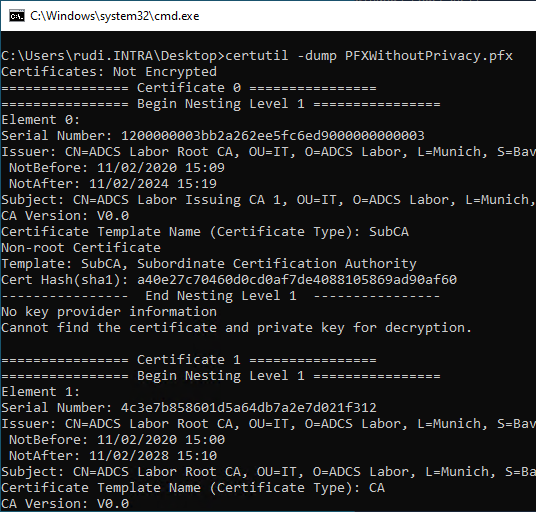
Due to this change in the application behavior, such a PKCS#12 file does not ask for a password for the private part and accordingly no test of the private key is performed.
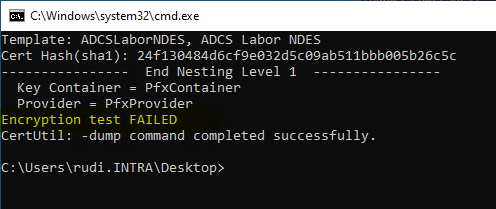
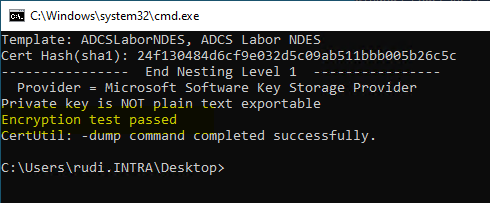
If you want to check the function of the private key, unfortunately you now have to specify the password directly in the command line:
certutil -p {Passwort} -dump {Datei}