The certification authority service does not start and throws the error message "The parameter is incorrect. 0x80070057 (WIN32: 87 ERROR_INVALID_PARAMETER)"
Assume the following scenario:
- A certification authority is implemented in the network.
- The certification authority service does not start.
- When trying to start the certification authority service, you get the following error message:
The parameter is incorrect. 0x57 (WIN32: 87 ERROR_INVALID_PARAMETER)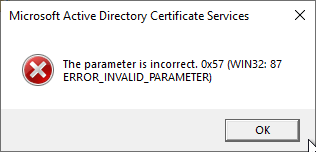
A corresponding event no. 100 can also be found in the Event Viewer of the certification authority:
Active Directory Certificate Services did not start: Could not load or verify the current CA certificate. FabrikamRootCA The parameter is incorrect. 0x80070057 (WIN32: 87 ERROR_INVALID_PARAMETER).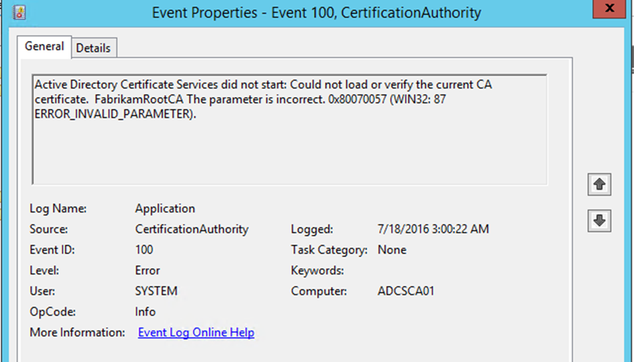
Cause
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Usually, the error is due to the fact that there is a problem with the CACertHash registry value of the certification authority.
This is located in the following path:
HKLM\System\CurrentControlSet\Services\CertSvc\Configuration\{Common-Name-der-Zertifizierungsstelle}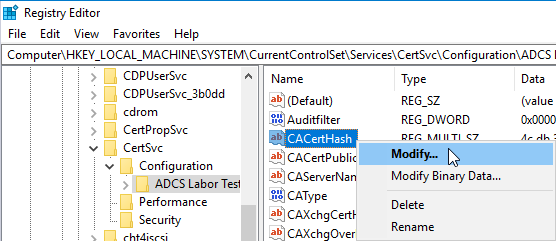
CACertHash contains invalid thumbprints
The error may occur if the CACertHash value contains invalid (e.g.: incomplete) thumbprints.
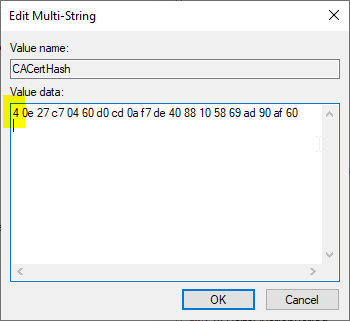
CACertHash contains hidden control character
The error occurred in the example because the registry value CACertHash could not be read. Here a thumbprint value was replaced , copying an invisible character into the registry value "CACertHash".
You can check this with the following command line command:
certutil -getreg CA\CaCertHash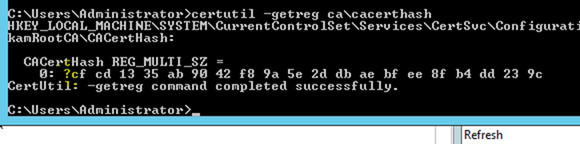
When copying the thumbprint from the certificate dialog, a space often creeps in that you don't see in Regedit or the text editor.
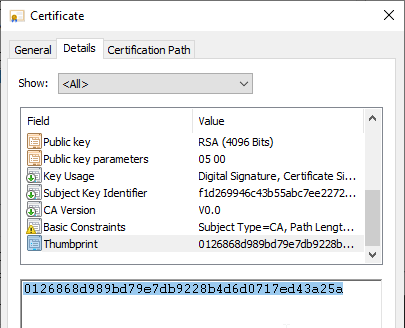
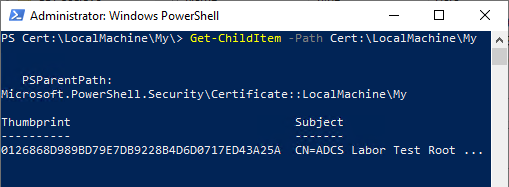
It is therefore advisable to type in the thumbprint for such an operation or to determine it from another source, such as Windows PowerShell. In Windows PowerShell, this can be done using the Get-ChildItem command.
For machine certificates:
Get-ChildItem -Path Cert:\LocalMachine\MyFor user certificates:
Get-ChildItem -Path Cert:\CurrentUser\My