
Details of the event with ID 94 of the source Microsoft-Windows-CertificationAuthority
| Event Source: | Microsoft-Windows-CertificationAuthority |
| Event ID: | 94 (0x5E) |
| Event log: | Application |
| Event type: | Warning |
| Symbolic Name: | MSG_CA_CERT_NO_AUTH_STORE |
| Event text (English): | Active Directory Certificate Services %1 can not open the certificate store at CN=NTAuthCertificates,CN=Public Key Services,CN=Services in the Active Directory's configuration container. |
| Event text (German): | Der Zertifikatspeicher unter "CN=NTAuthCertificates,CN=Public Key Services,CN=Services" im Konfigurationscontainer von Active Directory kann von Active Directory-Zertifikatdienste %1 nicht geöffnet werden. |
Parameter
The parameters contained in the event text are filled with the following fields:
- %1: CACommonName (win:UnicodeString)
Example events
Active Directory Certificate Services ADCS Labor Issuing CA 1 can not open the certificate store at CN=NTAuthCertificates,CN=Public Key Services,CN=Services in the Active Directory's configuration container.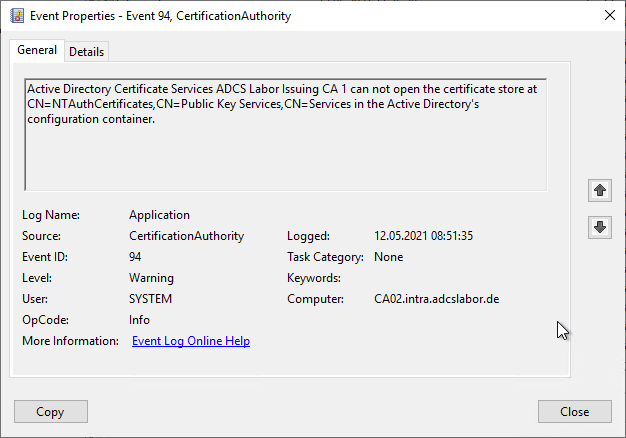
Description
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Usually occurs when the certification authority cannot connect to a domain controller, for example, due to lack of network connectivity, firewall rules, or because all domain controllers are offline. See also events no. 91 , 44 and 9 .
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
No description has been written for this yet.
Microsoft's rating
Microsoft evaluates this event in the Securing Public Key Infrastructure (PKI) Whitepaper with a severity score of "Low".