
Requesting certificates via the Certificate Enrollment Policy Web Service (CEP) fails with error message "A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted."
Assume the following scenario:
- You try to request a certificate via a Certificate Enrollment Policy Web Service (CEP) from an Active Directory-integrated certification authority (Enterprise Certification Authority).
- To do this, you use the Microsoft Management Console (MMC), either for the logged-on user (certmgr.msc) or for the computer (certlm.msc).
- However, the list of available certificate templates within the MMC is completely empty.
- In the list of available certificate templates within the MMC, you choose to show all certificate templates. All desired certificate templates show:
Cannot find Object or property.
A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted.
The Certificate Enrollment Web Services (Certificate Enrollment Policy Web Service, CEP, and Certificate Enrollment Web Service, CES) enable the automatic request and renewal of certificates from a certification authority via a web-based interface. This eliminates the need to contact the certification authority directly via Remote Procedure Call (RPC). For a more detailed description, see the article "Basics: Requesting certificates via Certificate Enrollment Web Services (CEP, CES) ".
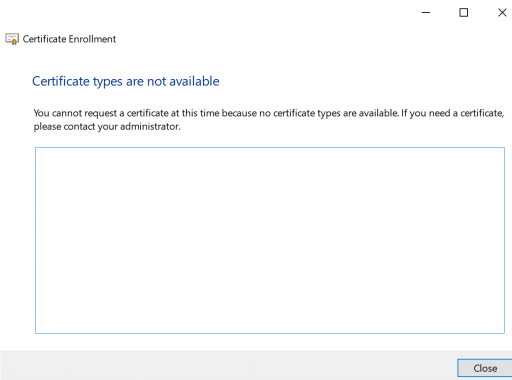
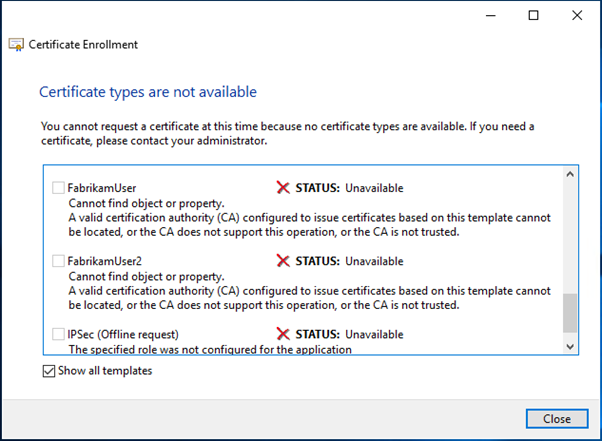
The CEP server will log Event no. 10 in Event Viewer:
There is no enterprise certification authority (CA) configured with the Certificate Enrollment Web Service in the current forest. Confirm that at least one enterprise CA is available in the forest and that at least one server running the Certificate Enrollment Web Service is configured to work with this CA.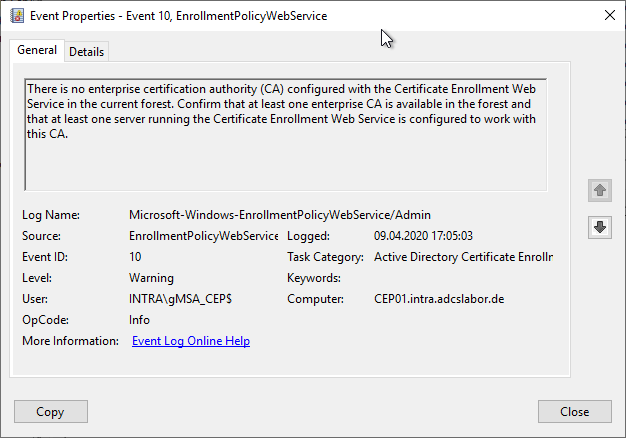
Possible causes
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
This error is not caused by the Certificate Enrollment Policy Web Service (CEP), but by the Certificate Enrollment Web Service (CES), and can occur under the following circumstances:
- The user has no permissions on the certificate templates.
- There is a bug that causes certificate templates set to Windows Server 2016 compatibility not to be displayed.
- If the Windows logon service provider on the CEP server has been disabled (for example, by a hardening action), the logon service provider in Internet Information Services (IIS) for CEP must be changed from Negotiate to Negotiate:Kerberos (in this case, no event is logged on the CEP).
- There is no CES on the network. Accordingly, none of the pKIEnrollmentService objects in Active Directory has a populated msPKI-Enrollment-Servers attribute.
- The CES address in the msPKI-Enrollment-Servers attribute within the pKIEnrollmentService object of the certification authority is configured incorrectly.
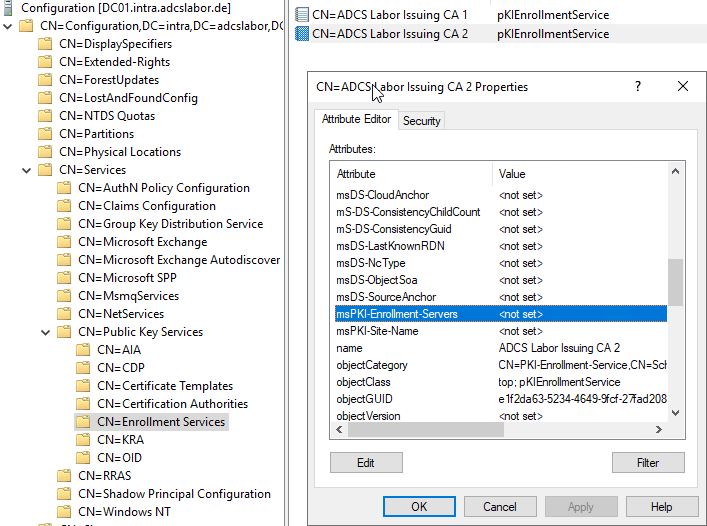
You can view the Certificate Enrollment Web Services configured for a certification authority with the following command:
certutil -config "{Host-Name-des-CA-Servers}\{CA-Common-Name}" -enrollmentserverurlDetails: There is a bug that causes certificate templates set to Windows Server 2016 compatibility not to be displayed.
There is a known issue that, via CES, certificate templates configured for Windows Server 2016 compatibility cannot be displayed .
The bug has not been fixed yet, so this statement also applies to Windows Server 2019.
The only way around this is to set the certificate template to Windows Server 2012 R2 compatibility at most.
For the background, see the article "Description of certificate template generations ".
Configuration error examples
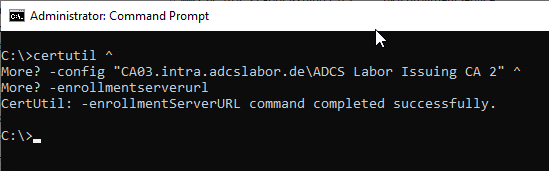
No output of the command - because no enrollment server is configured for this certification authority
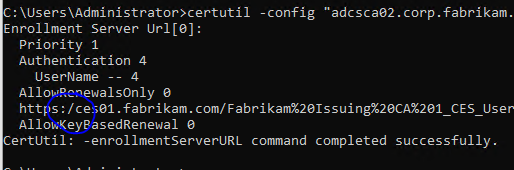
Wrong: A backslash "/" for the web address was forgotten here.
The enrollment server addresses should always be edited with the associated command line tools. Editing with the ADSI editor, for example, will result in the entry in the msPKI-Enrollment-Servers attribute not being processed correctly.
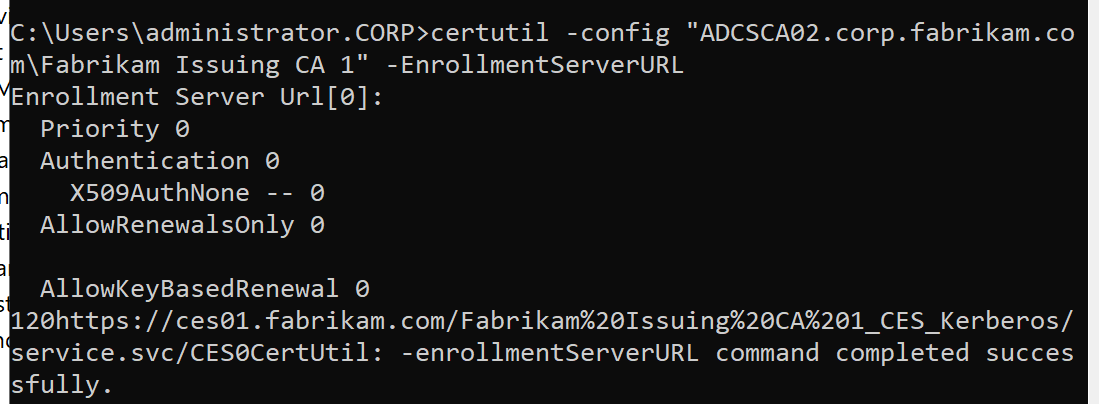
Wrong: Here the Enrollment Server URL was entered with the ADSI Editor and cannot be read out.
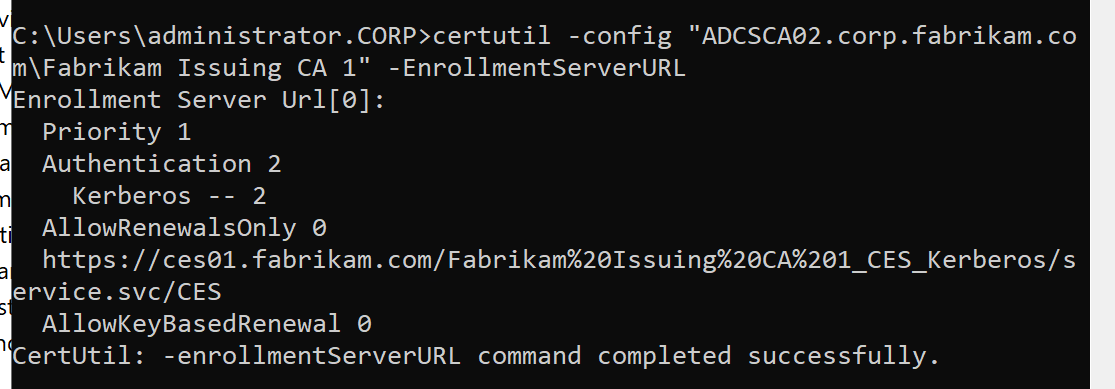
Correct: This is what the output of the command should look like.
Related links:
- The Certificate Enrollment Policy Web Service (CEP) does not display certificate templates configured for compatibility with Windows Server 2016 or Windows 10
- Configure the Certificate Enrollment Policy Web Service (CEP) to work with a domain account.
- Configure the Certificate Enrollment Policy Web Service (CEP) to work with a Group Managed Service Account (gMSA).