The certification authority service does not start and throws the error message "A certificate chain processed, but terminated in a root certificate which is not trusted by the trust provider. 0x800b0109 (-2146762487 CERT_E_UNTRUSTEDROOT)"
Assume the following scenario:
- A certification authority is implemented in the network.
- The certification authority service does not start.
- When trying to start the certification authority service, you get the following error message:
A certificate chain processed, but terminated in a root certificate which is not trusted by the trust provider. 0x800b0109 (-2146762487 CERT_E_UNTRUSTEDROOT)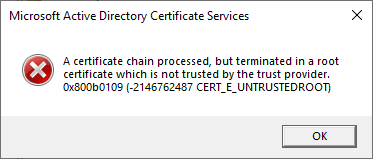
A corresponding event no. 100 can also be found in the Event Viewer of the certification authority:
Active Directory Certificate Services did not start: Could not load or verify the current CA certificate. ADCS Labor Issuing CA 3 A certificate chain processed, but terminated in a root certificate which is not trusted by the trust provider. 0x800b0109 (-2146762487 CERT_E_UNTRUSTEDROOT).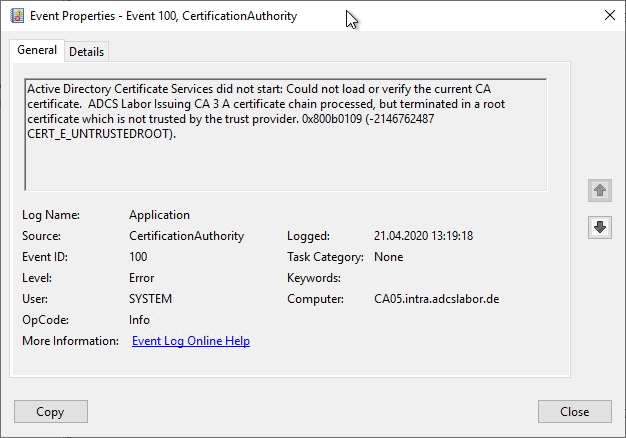
Cause
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
This error is closely related to the error CERT_E_CHAINING . In this case, the certificate chain can be formed up to the root certification authority certificate, but this certificate is not located in the "Trusted Root Certification Authorities" store on the certification authority.
Solution
In addition to the certification authority itself, all other participants must of course also trust the certificates. It therefore makes sense not only to import the certificates into the local certificate store of the certification authority, but also to distribute them centrally throughout the entire Active Directory forest, e.g. via Group Policy.
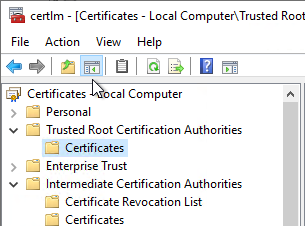
In order to start the certification authority service, the certificate chain, i.e. all certificates up to the root certification authority, must be installed in the computer certificate store of the certification authority computer. This can be done via the certificate management console for the local computer account (certlm.msc).
- Root certification authority certificates must be stored in the "Trusted Root Certification Authorities" certificate store of the computer account.