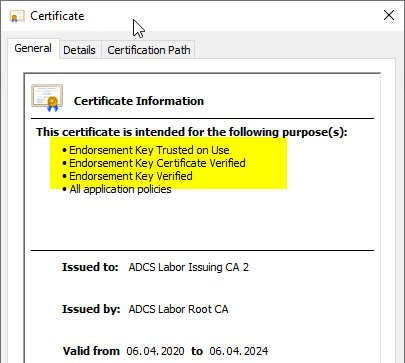
Include the issuance policies for Trusted Platform (TPM) Key Attestation in a certification authority certificate
If you install an issuing CA and do not explicitly request an issuance policy, the resulting CA certificate does not contain any issuance policies.
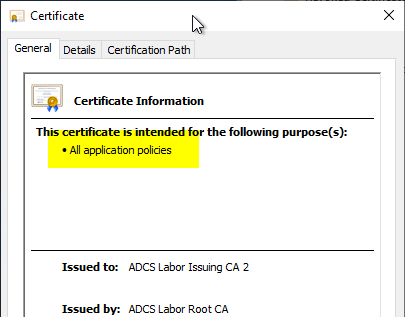
If you want to include the issuance policies for Trusted Platform (TPM) Key Attestation in the certification authority certificate, you must proceed as follows.
The following OIDs are used for TPM Key Attestation.
| OID | Meaning |
|---|---|
| 1.3.6.1.4.1.311.21.32 | TPM Key Attestation: User Credentials: (Low Assurance) |
| 1.3.6.1.4.1.311.21.31 | TPM Key Attestation: Endorsement Certificate: (Medium Assurance) |
| 1.3.6.1.4.1.311.21.30 | TPM Key Attestation: Endorsement Key: (High Assurance) |
Implementation
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
In order to include issuance policies in a certification authority certificate, it is necessary to submit a new certificate request and issue a new certification authority certificate. Since the existing certificate is signed, it cannot be changed.
In order for the issuance policies to be included in the certificate request, the C:\Windows\capolicy.inf file must be edited before the request is submitted. The following section must be added:
[PolicyStatementExtension]
Policies=TpmLowAssurancePolicy,TpmMediumAssurancePolicy,TpmHighAssurancePolicy

; TPM Key Attestattion: User Credentials (Low Assurance)
[TpmLowAssurancePolicy]
OID=1.3.6.1.4.1.311.21.32

; TPM Key Attestattion: Endorsement Certificate (Medium Assurance)
[TpmMediumAssurancePolicy]
OID=1.3.6.1.4.1.311.21.31

; TPM Key Attestattion: Endorsement Key (High Assurance)
[TpmHighAssurancePolicy]
OID=1.3.6.1.4.1.311.21.30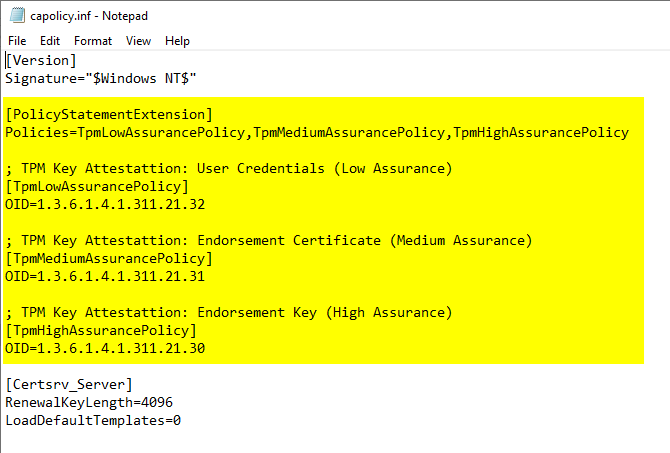
A new certificate request can then be submitted.
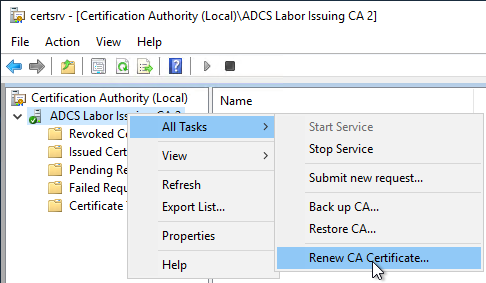
After the certificate request is signed by the parent certification authority, the new certification authority certificate should include the issuance policies for Trusted Platform (TPM) Key Attestation.