
How the TameMyCerts Policy Module for Active Directory Certificate Services (ADCS) can prevent attacks against the ESC1 attack vector
Attacks on Microsoft certification authorities can be aimed at exploiting permissions on certificate templates. In many cases, certificate templates must be configured to grant the enrollee the right to request arbitrary identities. This can lead to the attacker taking over the identities of Active Directory accounts and subsequently to privilege escalation. Attacks of this type are known in the security scene as "ESC1 ".
TameMyCerts is a policy module to secure the Microsoft certification authority (Active Directory Certificate Services). It extends the functions of the certification authority and enables the extended application of rule sets to enable the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem and is available under a free license. It can be downloaded via GitHub and used free of charge.
TameMyCerts is open source and can be used free of charge. For use in the corporate sector, however, we recommend concluding a maintenance contract. This ensures that you receive qualified support and that the module can be further developed to a high quality in the long term.
ESC1 targets certificate templates that have the "Supply in the request" setting configured (also called "offline" certificate templates, because the identity in the issued certificate is determined by the enrollee, in contrast to "online" certificate templates, where it is formed from the Active Directory based on the enrollee's logon credentials).
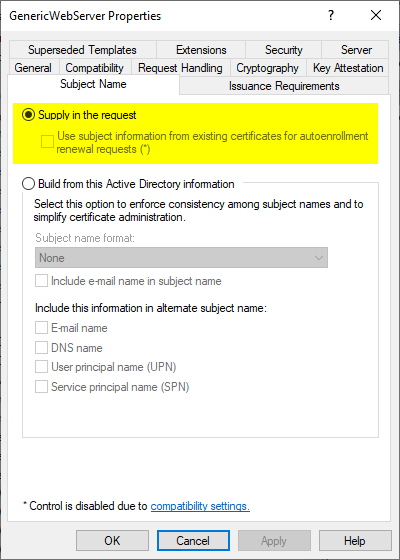
A certificate template that allows the enrollee to supply the identity of the issued certificate in the certificate request
Once the attacker has located a certificate template that is configured accordingly and grants them "Enroll" permissions, all they have to do is submit a corresponding certificate request with the desired identity to the certification authority.
TameMyCerts can either completely prevent attacks against ESC1 or drastically reduce the resulting damage:
- TameMyCerts can enforce identity types and thus ensure that issued certificates only contain certain defined field types.
- TameMyCerts can apply syntax rules to certificate requests and thus ensure that only certificate content that complies with the defined naming conventions is issued.
- TameMyCerts can map identities requested in the certificate back against Active Directory and apply rules based on status, security group or organizational unit memberships and account attributes.
Without TameMyCerts, this fine-grained control over the certificate content is not possible with a Microsoft certification authority, so there is a large window for attacks, which in the worst case could allow an attacker to take over the entire Active Directory forest.
Rule violations are logged in the certification authority's event log and thus allow an alarm to be raised for rule violations.
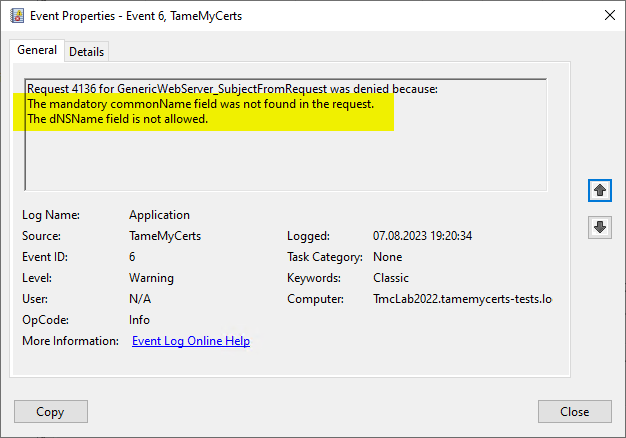
A certificate request that does not contain the defined certificate fields was rejected and logged by TameMyCerts
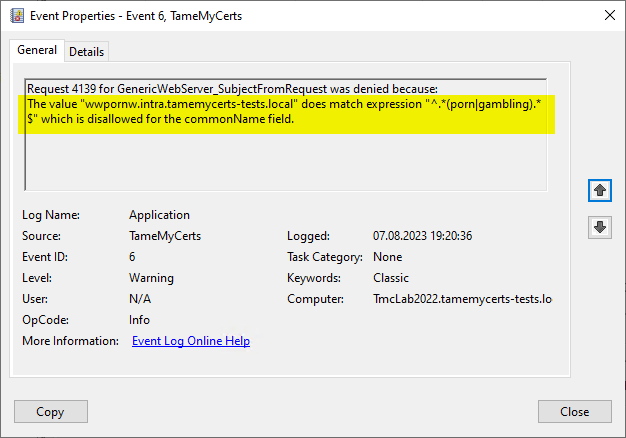
A certificate request that contains prohibited content and thus violates defined syntax rules was rejected and logged by TameMyCerts
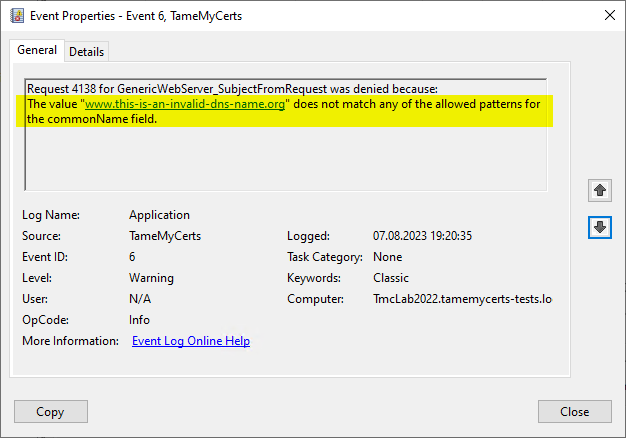
A certificate request that does not conform to the defined syntax rules was rejected and logged by TameMyCerts
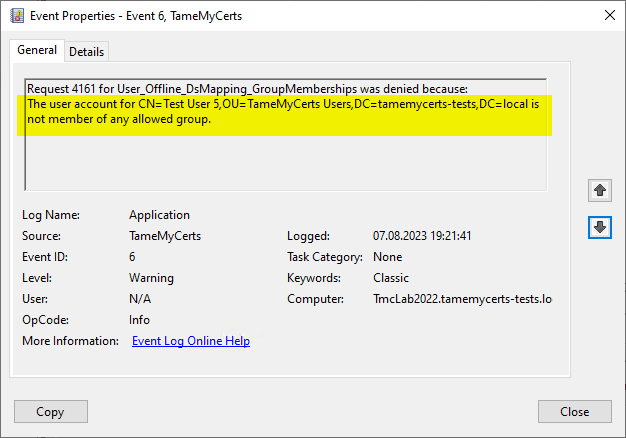
A certificate request containing the identity of an account that is not a member of a defined security group was rejected and logged by TameMyCerts
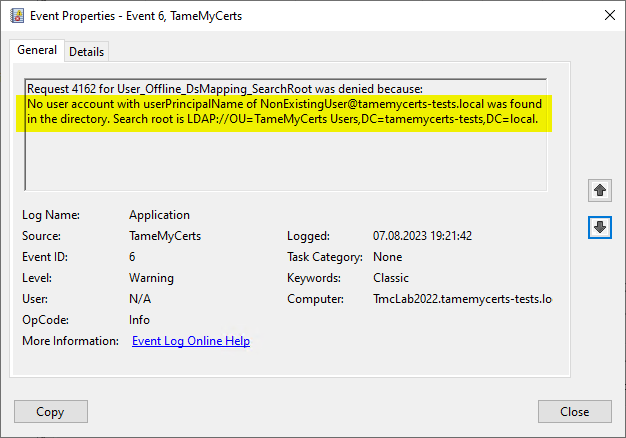
A certificate request containing the identity of an account that does not exist in the defined search path was rejected and logged by TameMyCerts
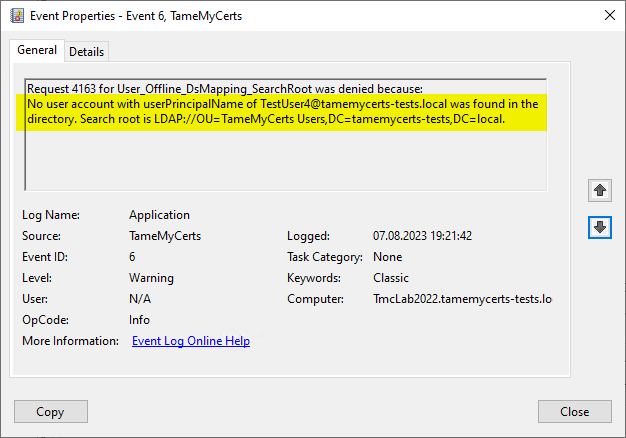
A certificate request for an account that is not in the defined organizational unit was rejected and logged by TameMyCerts
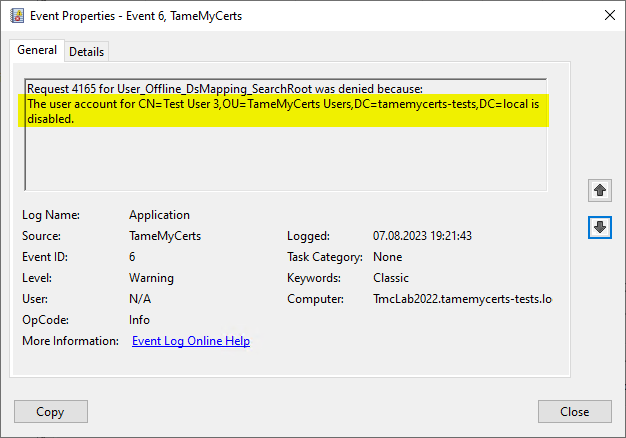
A certificate request containing the identity of a deactivated account was rejected and logged by TameMyCerts
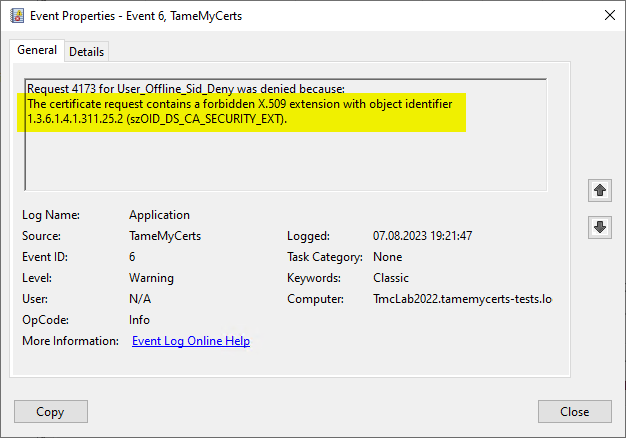
A certificate request with an unauthorized certificate extension
A certificate request containing the identity of a deactivated account was rejected and logged by TameMyCerts
Related links:
- A policy module to tame them all: Introducing the TameMyCerts Policy Module for Microsoft Active Directory Certificate Services
- Attack vector on the Active Directory directory service via the smart card logon mechanism