
Details of the event with ID 9 of the source Microsoft-Windows-CertificationAuthority
| Event Source: | Microsoft-Windows-CertificationAuthority |
| Event ID: | 9 (0x9) |
| Event log: | Application |
| Event type: | Error |
| Symbolic Name: | MSG_NO_POLICY |
| Event text (English): | The Active Directory Certificate Services did not start: Unable to load an external policy module. |
| Event text (German): | Die Active Directory-Zertifikatdienste wurden nicht gestartet: Es konnte kein externes Richtlinienmodul geladen werden. |
Example events
The Active Directory Certificate Services did not start: Unable to load an external policy module.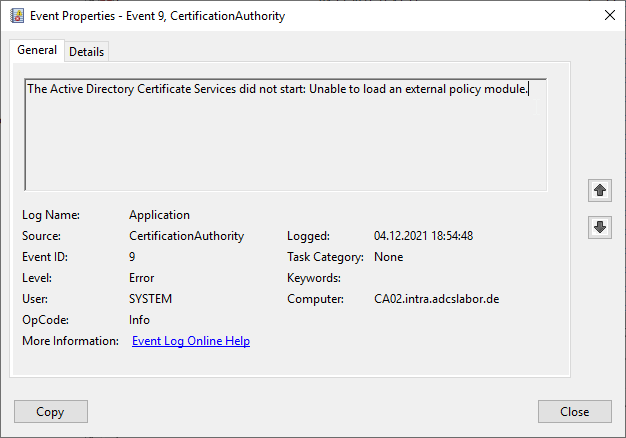
Description
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Occurs when the certification authority cannot load a policy module. Occurs in conjunction with event no. 44 .
It may occur due to the cause when no connection to the Active Directory can be established when the certification authority service is started. In this case, events no. 91 and 94 are also logged.
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
Since the certification authority service cannot start, the certification authority is not available. In addition to it no longer being possible to request certificates, this will in the long term also mean that no new CRLs will be issued and thus services that depend on the PKI will fail.
It is therefore essential to raise the alarm. Emergency measures should also be initiated to keep CRL operation running.
Microsoft's rating
Microsoft evaluates this event in the Securing Public Key Infrastructure (PKI) Whitepaper with a severity score of "Low".
Related links:
- Overview of Windows events generated by the certification authority
- Overview of audit events generated by the certification authority
- Perform emergency signing of certificate revocation lists
External sources
- Event ID 9 - AD CS Policy Module Processing (Microsoft)
- Securing Public Key Infrastructure (PKI) (Microsoft)