
Details of the event with ID 302 of the source Microsoft-Windows-Kerberos-Key-Distribution-Center
| Event Source: | Microsoft-Windows-Kerberos-Key-Distribution-Center |
| Event ID: | 302 (0x12E) |
| Event log: | Microsoft-Windows-Kerberos-Key-Distribution-Center/Operational |
| Event type: | Information |
| Event text (English): | The Key Distribution Center (KDC) uses the below KDC certificate for smart card or certificate authentication. Kdc Certificate Information: Issuer Name: %1 Serial Number: %2 Thumbprint: %3 Template: %4 |
| Event text (German): | Das Schlüsselverteilungscenter (KDC) verwendet das folgende Zertifikat für die Smartcard- oder Zertifikatauthentifizierung. KDC-Zertifikatinformationen: Ausstellername: %1 Seriennummer: %2 Fingerabdruck: %3 Vorlage: %4 |
Do you know TameMyCerts? TameMyCerts is an add-on for the Microsoft certification authority (Active Directory Certificate Services). It extends the function of the certification authority and enables the application of rule sets to realize the secure automation of certificate issuance. TameMyCerts is unique in the Microsoft ecosystem, has already proven itself in countless companies around the world and is available under a free license. It can be downloaded via GitHub and used free of charge. Professional maintenance is also offered.
Parameter
The parameters contained in the event text are filled with the following fields:
- %1: Issuer (win:UnicodeString)
- %2: SerialNumber (win:UnicodeString)
- %3: Thumbprint (win:UnicodeString)
- %4: Template (win:UnicodeString)
Example events
The Key Distribution Center (KDC) uses the below KDC certificate for smart card or certificate authentication.
Kdc Certificate Information:
Issuer Name: ADCS Labor Issuing CA 1
Serial Number: 73000000EBB33E677E96254B750000000000EB
Thumbprint: C230A32DCDFE93F82B7E255E374AA5C0869604ED
Template: ADCS Labor Kerberos Authentication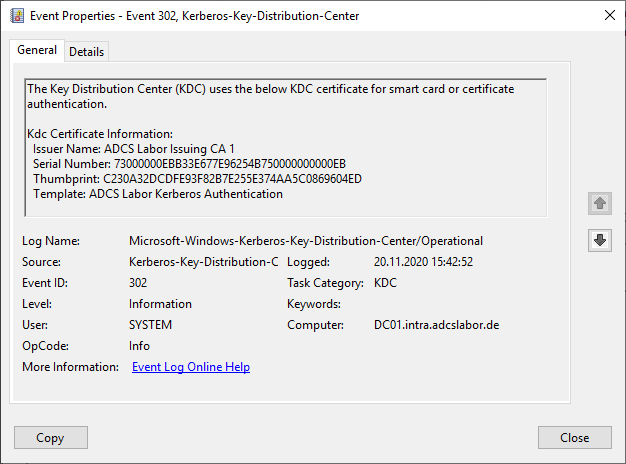
Description
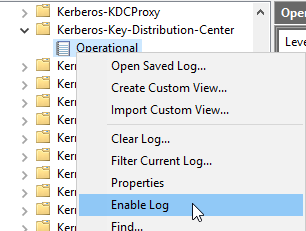
This event is generated only if the corresponding event log has been explicitly enabled.
Security assessment
The security assessment is based on the three dimensions of confidentiality, integrity and availability.
No description has been written for this yet.
External sources
- What's New in Kerberos Authentication (Microsoft)