
Certificate request fails with error message "The certificate request could not be submitted to the certification authority. Error: The RPC server is unavailable. 0x800706ba (WIN32: 1722 RPC_S_SERVER_UNAVAILABLE)".

Assume the following scenario:

  • A user or a computer requests a certificate from an Active Directory integrated certification authority (enterprise CA)
  • The certificate request fails with the following error message:
The certificate request could not be submitted to the certification authority. Error: The RPC server is unavailable. 0x800706ba (WIN32: 1722 RPC_S_SERVER_UNAVAILABLE) 
Continue reading "Certificate request fails with error message "The certificate request could not be submitted to the certification authority. Error: The RPC server is unavailable. 0x800706ba (WIN32: 1722 RPC_S_SERVER_UNAVAILABLE)"."

Basics: Cryptography

The need for the use of cryptography can be summarized under the notion of ensuring secure communication in the presence of untrusted third parties. The goals of cryptography are:

  1. To prevent data from falling into unauthorized hands (To ensure the confidentiality of data).
  2. Find out if data has been modified during transport (Ensure the integrity of the data).
  3. To clearly identify the source of the data (To ensure the authenticity of the data).
  4. Additionally, users or computers can authenticate themselves using cryptography.

Continue reading "Basics: Cryptography"

Editing the NTAuthCertificates object in Active Directory

In the default configuration, all certification authority certificates of Active Directory integrated certification authorities (enterprise CAs) are located in an object of type CertificationAuthority named NTAuthCertificates within the Configuration Partition of the Active Directory forest.

Continue reading "Editing the NTAuthCertificates object in Active Directory"

Publishing a certificate revocation list (CRL) fails with the error message "Insufficient access rights to perform the operation. 0x80072098 (WIN32: 8344 ERROR_DS_INSUFF_ACCESS_RIGHTS)"

Assume the following scenario:

  • An attempt is made to publish a new certificate revocation list (CRL) on a certification authority
  • The certification authority is configured to publish the certificate revocation lists to Active Directory (LDAP CDP).
  • Publishing the certificate revocation list fails with the following error message:
Insufficient access rights to perform the operation. 0x80072098 (WIN32: 8344 ERROR_DS_INSUFF_ACCESS_RIGHTS)

Continue reading "Publishing a certificate revocation list (CRL) fails with the error message "Insufficient access rights to perform the operation. 0x80072098 (WIN32: 8344 ERROR_DS_INSUFF_ACCESS_RIGHTS)""

Publishing a certificate revocation list (CRL) fails with the error message "Directory object not found. 0x8007208d (WIN32: 8333 ERROR_DS_OBJ_NOT_FOUND)"

Assume the following scenario:

  • An attempt is made to publish a new certificate revocation list (CRL) on a certification authority.
  • The certification authority is configured to publish the certificate revocation lists to Active Directory (LDAP CDP).
  • Publishing the certificate revocation list fails with the following error message:
Directory object not found. 0x8007208d (WIN32: 8333 ERROR_DS_OBJ_NOT_FOUND)

Continue reading "Publishing a certificate revocation list (CRL) fails with the error message "Directory object not found. 0x8007208d (WIN32: 8333 ERROR_DS_OBJ_NOT_FOUND)""

Firewall rules required for Active Directory Certificate Services

Implementing an Active Directory integrated certification authority often requires planning the firewall rules to be created on the network. The following is a list of the required firewall rules and any pitfalls.

Continue reading "Firewall rules required for Active Directory Certificate Services"

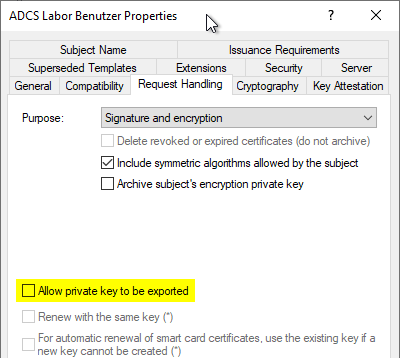
How secure is the "Allow private key to be exported" setting in the certificate templates?

PKI administrators often assume that the option in the certificate template not to allow the private key to be exported is binding.

However, that is not the case.

Continue reading "How secure is the "Allow private key to be exported" setting in the certificate templates?"

Advanced queries against the certification authority database

The certification authority database stores much of the information about a certification authority's activities. Among other things, it contains information about:

  • Certificates issued
  • Revoked certificates
  • Published certificate revocation lists (CRLs)
  • Pending certificate requests
  • Rejected certificate requests
  • Failed certificate requests

Viewing the contents of the certification authority database is usually done via the certification authority's management console (certsrv.msc), but the possibilities for evaluation and especially for machine processing are very limited.

Continue reading "Advanced queries against the certification authority database"

Requesting a certificate fails with the error message "A certification chain processed correctly, but one of the CA certificates is not trusted by the policy provider. 0x800b0112 (-2146762478 CERT_E_UNTRUSTEDCA)"

Here's the scenario:

  • A user requests a certificate from an Active Directory integrated certification authority (enterprise CA).
  • The certificate of the certification authority is trusted, i.e. it is located in the Trusted Root Certification Authorities store.
  • The certificate request fails with the following error message:
A certification chain processed correctly, but one of the CA certificates is not trusted by the policy provider. 0x800b0112 (-2146762478 CERT_E_UNTRUSTEDCA)

Continue reading "Requesting a certificate fails with the error message "A certification chain processed correctly, but one of the CA certificates is not trusted by the policy provider. 0x800b0112 (-2146762478 CERT_E_UNTRUSTEDCA)""

Requesting a certificate fails with the error message "The requested operation cannot be completed. The computer must be trusted for delegation and the current user account must be configured to allow delegation. 0x80090345 (-2146892987 SEC_E_DELEGATION_REQUIRED).". When importing PFX files, the private key is missing.

Here's the scenario:

  • The import of a PFX file seems to be successful, but afterwards the private key is missing. A check with certutil ends with the error message "Missing stored keyset".
  • Requesting a certificate on a client fails with the following error message:
The requested operation cannot be completed. The computer must be trusted for delegation and the current user account must be configured to allow delegation. 0x80090345 (-2146892987 SEC_E_DELEGATION_REQUIRED).

Continue reading "Requesting a certificate fails with the error message "The requested operation cannot be completed. The computer must be trusted for delegation and the current user account must be configured to allow delegation. 0x80090345 (-2146892987 SEC_E_DELEGATION_REQUIRED).". When importing PFX files, the private key is missing."

Requesting a certificate for a domain controller fails with error message "The RPC server is unavailable. 0x800706ba (WIN32: 1722 RPC_S_SERVER_UNAVAILABLE)"

Here's the scenario:

  • Requesting a certificate for a domain controller fails.
  • On the certification authority, the certificate request is logged in the failed requests. The error message reads:
The RPC server is unavailable. 0x800706ba (WIN32: 1722 RPC_S_SERVER_UNAVAILABLE)

Continue reading "Requesting a certificate for a domain controller fails with error message "The RPC server is unavailable. 0x800706ba (WIN32: 1722 RPC_S_SERVER_UNAVAILABLE)""

Incremental backups of the certification authority database fail with the error message "The database missed a previous full backup before incremental backup"

Assume the following scenario:

  • You use certutil.exe or the PowerShell commandlet Backup-CAService to back up your Active Directory Certificate Services database.
  • In addition to a full backup, you also perform regular incremental backups of the CA database.
  • The incremental backups fail with error message "The database missed a previous full backup before incremental backup".
Incremental database backup for…
 Backing up Log files: 0%CertUtil: -backupDB command FAILED: 0xc8000230 (ESE: -560 JET_errMissingFullBackup)
 CertUtil: The database missed a previous full backup before incremental backup

Continue reading "Incremental backups of the certification authority database fail with the error message "The database missed a previous full backup before incremental backup""

Requesting a certificate fails with the error message "A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted."

Assume the following scenario:

  • You try to request a certificate from an Active Directory integrated certification authority (enterprise CA).
  • To do this, you use the Microsoft Management Console (MMC), either for the logged-on user (certmgr.msc) or for the computer (certlm.msc).
  • However, the desired certificate template is not offered for selection, even though it has been correctly published on the certification authority.
  • The logged-on user (or computer) also has the necessary permissions to request certificates from the certificate template in question (Enroll).
  • In the list of available certificate templates within the MMC, you have all certificate templates displayed. The desired certificate template shows:
A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted.

Continue reading "Requesting a certificate fails with the error message "A valid certification authority (CA) configured to issue certificates based on this template cannot be located, or the CA does not support this operation, or the CA is not trusted.""